Network Detection and Response: A Practical Guide

Modern organisations rely on networks to connect users, devices, applications and cloud services. That connectivity also creates opportunities for cyber attackers. Threats can enter through compromised accounts, vulnerable devices, malicious software or trusted services, and may move across a network without immediately attracting attention.

Network Detection and Response (NDR) helps security teams identify suspicious activity across network traffic and investigate or contain potential threats. It is not a replacement for other security controls. Instead, it adds visibility into how systems communicate, helping teams spot activity that endpoint or identity tools may not reveal on their own.

What is Network Detection and Response?

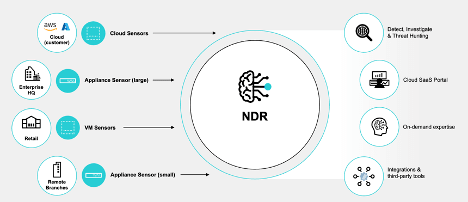
NDR is a cybersecurity approach that analyses network activity to detect threats and support an effective response. NDR platforms typically collect and examine network traffic metadata, such as which systems are communicating, when they communicate and how much data is transferred. Some solutions can also inspect selected traffic content, depending on the organisation’s architecture, policies and encryption practices.

Using analytics, threat intelligence and behavioural models, an NDR system looks for activity that may indicate a security incident. Examples include an unusual connection to an external server, unexpected data transfers, communications between devices that do not normally interact, or signs that a compromised system is attempting to spread across the network.

How does NDR work?

Although capabilities vary between products, an NDR deployment commonly involves several stages:

  1. Collecting network data: Sensors or integrations gather information from network traffic, cloud environments and other relevant sources. Data may come from network taps, traffic mirrors, flow records or existing security tools.
  2. Establishing normal behaviour: Analytics build a picture of typical communication patterns across users, devices and services. This provides context for identifying activity that appears unusual.
  3. Detecting suspicious activity: The platform combines behavioural analysis, known threat indicators and security rules to flag potential threats. A single unusual event is not necessarily malicious, so context is important.
  4. Investigating alerts: Security teams can review related events, trace communications and identify which systems may be affected. Linking activity across time can help reveal a wider attack sequence.
  5. Supporting response: Depending on the solution and its integrations, teams may be able to isolate a device, block a connection, disable an account through another security tool or guide a manual investigation.

What can NDR help detect?

NDR can be useful for identifying threats that are difficult to spot through a single endpoint or perimeter alert. These may include:

  • lateral movement between systems after an initial compromise;
  • command-and-control communications between malware and external infrastructure;
  • unusual data transfers that could indicate data theft;
  • unexpected access to sensitive services or network segments;
  • activity involving unmanaged or poorly monitored devices; and
  • changes in communication patterns that may point to a compromised account or system.

Detection is not guaranteed. Attackers may use encryption, legitimate services or low-volume activity to make their actions harder to distinguish from normal business traffic. NDR should therefore form part of a broader security strategy.

Benefits of Network Detection and Response

Greater network visibility

NDR can give security teams a clearer view of communication across on-premises networks, data centres and cloud environments. This can be especially valuable where an organisation has a large number of devices or does not manage every endpoint directly.

Earlier threat discovery

By examining relationships and patterns across network activity, NDR may reveal signs of an intrusion that would be missed by looking at isolated events. Earlier discovery can give teams more time to investigate and limit potential harm.

Support for incident investigations

Network records can help establish what happened, when it happened and which systems communicated with one another. This evidence can support incident response, recovery and post-incident reviews.

Improved security operations

Integrations with tools such as security information and event management (SIEM) platforms, endpoint detection and response (EDR) systems and security orchestration tools can help teams connect alerts and coordinate action. The quality of these integrations and the processes around them matters as much as the technology itself.

NDR compared with other security tools

NDR, EDR and SIEM tools address different parts of the security picture:

  • EDR focuses on activity on individual endpoints, such as laptops and servers.
  • NDR focuses on communication and behaviour across networks.
  • SIEM collects and correlates security events from multiple sources to support monitoring, investigation and reporting.

These capabilities can complement one another. For example, NDR may identify suspicious traffic, while EDR provides detail about processes on the device generating it. A SIEM platform may bring those events together with identity, cloud and application logs. The best combination depends on an organisation’s risks, existing tools and available resources.

Planning an NDR deployment

Successful NDR adoption starts with clear objectives rather than simply installing sensors. Organisations should consider:

  • Coverage: Identify which networks, cloud services and critical systems need monitoring, and where visibility gaps exist.
  • Data and privacy: Understand what information is collected, how long it is retained, who can access it and how monitoring complies with applicable laws and internal policies.
  • Alert handling: Define who reviews alerts, how they are prioritised and when incidents should be escalated.
  • Integration: Check how NDR will work with existing identity, endpoint, SIEM and response tools.
  • Staffing and skills: Ensure the security team has the time and expertise to investigate alerts and tune detections.
  • Measurement: Track meaningful outcomes, such as investigation time, alert quality, coverage of critical assets and the ability to contain incidents.

A phased deployment can help teams validate data quality, reduce false positives and refine response procedures before extending monitoring across the whole environment.

Challenges and limitations

NDR can generate alerts that require investigation, particularly during initial deployment when the system is learning normal behaviour. Poorly tuned detections may create alert fatigue, while limited network coverage can leave blind spots. Encrypted traffic can also restrict what a platform can inspect, although metadata and behavioural patterns may still provide useful clues.

Automated response requires careful planning. Blocking a connection or isolating a device can disrupt legitimate work if an alert is incorrect. Organisations should define approval levels and safeguards that reflect the potential impact of each action.

Conclusion

Network Detection and Response helps organisations understand what is happening across their networks and identify behaviour that may signal a cyber threat. Its greatest value comes from combining broad network visibility with skilled investigation, reliable data and well-practised response procedures.

When integrated with endpoint, identity and monitoring controls, NDR can strengthen an organisation’s ability to detect and investigate attacks. It is most effective as part of a layered security programme, supported by clear ownership, regular review and a response plan that is tested before an incident occurs.


Enhancing Network Security: Six Key Advantages of Network Detection and Response

  1. Improves visibility across network activity.
  2. Helps detect threats earlier.
  3. Can identify lateral movement.
  4. Supports faster incident investigations.
  5. Complements endpoint security tools.
  6. Helps teams prioritise suspicious behaviour.


Challenges of Network Detection and Response: False Positives, Skill Requirements, and Encryption Limitations

  1. Can generate false positives and alert fatigue.
  2. May require specialist skills to investigate alerts.
  3. Encrypted traffic can limit visibility.

Improves visibility across network activity.

Network Detection and Response improves visibility across network activity by monitoring communications between users, devices, applications and services. This broader view helps security teams understand what normal behaviour looks like, identify unusual connections and investigate how a potential threat may be moving through the environment. With clearer insight into network activity, teams can spot suspicious behaviour that might otherwise go unnoticed and respond with greater context.

Helps detect threats earlier.

Network Detection and Response can help security teams spot threats earlier by continuously analysing network activity for unusual patterns. By identifying signs such as unexpected connections, suspicious data transfers or communication between systems that rarely interact, it can reveal potential attacks before they spread further or cause greater damage. Earlier detection gives organisations more time to investigate and respond.

Can identify lateral movement.

Network Detection and Response (NDR) can help identify lateral movement: when an attacker moves from an initially compromised device to other systems on the network. By analysing communication patterns between devices, NDR can flag unusual connections, unexpected access to services or attempts to reach systems that a user or device would not normally contact. This can help security teams investigate a potential breach and contain it before the attacker reaches more critical parts of the organisation’s network.

Supports faster incident investigations.

Network Detection and Response (NDR) supports faster incident investigations by bringing network activity into one view. Security teams can trace connections between devices, identify unusual communication and see how an event developed over time. This context helps analysts narrow down which systems may be affected and prioritise their next steps, reducing the time spent piecing together evidence from separate sources.

Complements endpoint security tools.

Network Detection and Response (NDR) complements endpoint security tools by adding visibility into the traffic flowing between devices, users and services. While endpoint detection and response (EDR) focuses on activity on individual laptops and servers, NDR can help identify suspicious communications or lateral movement across the wider network. Together, they provide a more complete picture of potential attacks, helping security teams connect endpoint alerts with network activity and investigate threats more effectively.

Helps teams prioritise suspicious behaviour.

Network Detection and Response helps security teams prioritise suspicious behaviour by analysing activity in context rather than treating every alert as equally urgent. By highlighting unusual communications, potential attack patterns and risks to important systems, NDR can help analysts focus their attention on the events most likely to require investigation. This makes it easier to use limited time and resources effectively, while reducing the chance that a serious threat is overlooked among routine alerts.

Can generate false positives and alert fatigue.

A key drawback of Network Detection and Response (NDR) is that it can generate false positives, flagging legitimate activity as suspicious. If alerts are too frequent or poorly prioritised, security teams may experience alert fatigue and struggle to distinguish genuine threats from routine network behaviour. This can delay investigations and increase the risk that an important warning is overlooked. Careful configuration, regular tuning and clear alert-prioritisation processes can help reduce the problem.

May require specialist skills to investigate alerts.

Network Detection and Response can generate alerts that require specialist knowledge to interpret. Security teams need to understand network behaviour, threat indicators and the organisation’s environment to distinguish genuine threats from unusual but legitimate activity. Without those skills, investigations may take longer, important alerts could be missed, or teams may spend too much time chasing false positives. Organisations may need to invest in training, recruit experienced staff or seek support from a specialist provider.

Encrypted traffic can limit visibility.

Encrypted traffic can limit visibility: As more network communications are encrypted, NDR tools may be unable to inspect their contents directly. They can still analyse metadata and communication patterns, but this may make it harder to identify malicious activity hidden within legitimate-looking connections. Decrypting traffic can provide greater insight, but it may raise privacy, compliance and performance concerns, so organisations need to balance visibility with these considerations.
Firewall Protection: A Guide to Keeping Your Network Secure

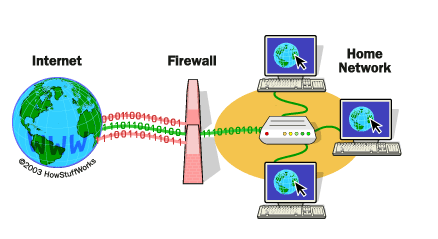
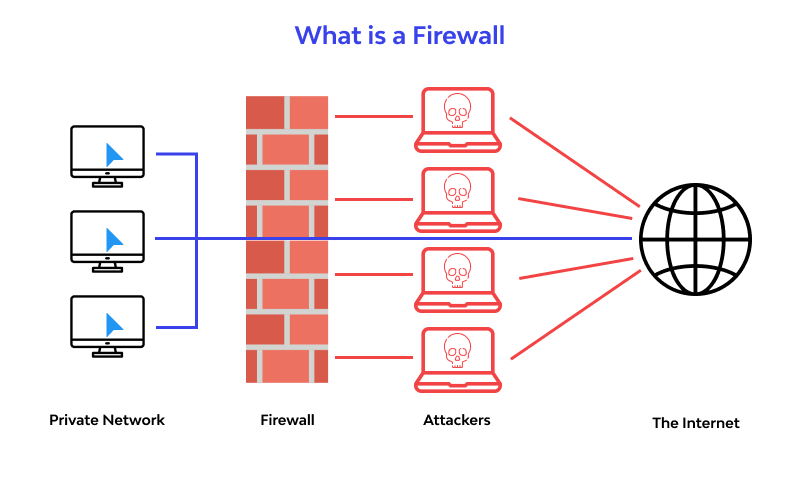
A firewall is one of the foundations of network security. It helps control the traffic entering and leaving a device or network, allowing authorised connections while blocking traffic that may be harmful or unwanted. Used alongside other security measures, firewall protection can reduce the risk of cyber attacks and help safeguard sensitive information.

What is a firewall?

A firewall is a security system that checks network traffic against a set of rules. Depending on its configuration, it can permit, block or restrict connections based on factors such as the source or destination of the traffic, the application being used, or the type of connection.

Firewalls can be installed on individual devices, built into network equipment, or provided as a cloud-based service. Many computers and routers include basic firewall features, while organisations may use more advanced systems to protect larger or more complex networks.

How does firewall protection work?

When data travels across a network, a firewall assesses it before allowing it through. It applies security rules to decide whether the traffic is expected and permitted. For example, a firewall might allow an employee to access an approved business service while blocking an attempt to connect to an unauthorised system.

Modern firewalls can do more than filter traffic by network address or port. Depending on the product, they may also inspect applications, monitor connections, detect suspicious activity and apply different rules to different users or devices.

Common types of firewalls

  • Network firewalls: Protect a network by controlling traffic between it and other networks, including the internet.
  • Host-based firewalls: Run on individual computers or servers and manage traffic to and from that device.
  • Next-generation firewalls: Offer more advanced inspection and security features, such as application awareness and intrusion prevention.
  • Cloud firewalls: Help protect cloud-based services, applications and infrastructure.
  • Web application firewalls: Focus on protecting web applications by filtering and monitoring web traffic.

These categories can overlap, and the right choice depends on the systems being protected, the level of risk and the organisation’s security requirements.

Why is a firewall important?

Firewall protection can help prevent unauthorised access to devices and networks. It can also reduce exposure to malicious traffic, limit access to unnecessary services and make it easier to monitor connections.

For organisations, carefully managed firewall rules can support network segmentation. This means separating parts of a network so that a security incident in one area is less likely to affect everything else. Firewall logs may also provide useful information for investigating unusual activity.

What a firewall cannot do

A firewall is not a complete security solution. It cannot reliably prevent every threat, particularly when a user opens a harmful attachment, enters credentials on a fraudulent website or approves a malicious connection. Nor can it replace secure software, strong authentication, regular updates or staff awareness.

Firewalls may also be less effective if they are poorly configured, out of date or left with unnecessary rules. Treat firewall protection as one layer in a wider security strategy rather than a guarantee that a network is safe.

Firewall best practices

  • Use a default-deny approach where practical: Allow only the connections needed for legitimate work, rather than permitting everything by default.
  • Review rules regularly: Remove rules that are outdated, duplicated or no longer required.
  • Limit access: Restrict administrative access to trusted users and devices, and use multi-factor authentication where available.
  • Keep systems updated: Apply security updates to firewalls, routers, operating systems and related software.
  • Monitor logs and alerts: Investigate unusual connection attempts and repeated blocked traffic.
  • Separate network zones: Use segmentation to limit unnecessary communication between systems, such as guest Wi-Fi and business devices.
  • Test changes carefully: Check that rule updates work as intended and do not create avoidable access or security problems.
  • Back up configurations: Keep secure copies so settings can be restored if a device fails or a change causes issues.

Firewall protection for businesses

Businesses should choose firewall controls that fit their environment, including remote working arrangements, cloud services and the sensitivity of the data they handle. Clear ownership is important: someone should be responsible for approving rule changes, checking alerts and arranging updates.

Organisations should also consider how firewall management fits with other controls, such as endpoint protection, identity and access management, secure backups and incident response plans. A well-maintained firewall can help reduce risk, but its effectiveness depends on consistent configuration and review.

Conclusion

Firewall protection helps control network traffic and block connections that do not meet defined security rules. It can be an important barrier against unauthorised access, but it works best as part of a broader approach that includes regular updates, strong authentication, monitoring and good security practices. Reviewing firewall settings routinely helps ensure that protection remains appropriate as devices, users and services change.


Essential FAQs About Firewall Protection: Understanding, Choosing, and Enabling Your Defence

  1. What is firewall protection?
  2. What are the 5 steps of firewall protection?
  3. Which is best firewall protection?
  4. Do I need antivirus if I have a firewall?
  5. What are the 3 types of firewalls?
  6. What is firewall and its uses?
  7. How do I turn on firewall protection?

What is firewall protection?

Firewall protection is a security measure that monitors and controls the network traffic entering and leaving a computer, device or network. It uses rules to allow legitimate connections and block unauthorised or suspicious traffic, helping reduce the risk of cyber attacks and unauthorised access. A firewall is an important part of online security, but it works best alongside other measures such as software updates, strong passwords and multi-factor authentication.

What are the 5 steps of firewall protection?

The five steps of firewall protection are to assess which devices, systems and data need protecting; choose a firewall suited to your network and security requirements; configure rules to allow necessary traffic and block unauthorised connections; monitor firewall logs and alerts for suspicious activity; and regularly review, update and test the settings as your network changes. A firewall is most effective when combined with other security measures, such as software updates, strong authentication and staff awareness.

Which is best firewall protection?

There is no single “best” firewall protection for everyone: the right choice depends on the devices, network, risks and level of control required. For most people, a built-in firewall on an up-to-date computer, combined with a secure router and sensible settings, provides a useful baseline. Businesses may need a centrally managed network or next-generation firewall with features such as application monitoring, intrusion prevention and detailed reporting. Whichever option you choose, keep it updated, allow only necessary connections and review its settings regularly.

Do I need antivirus if I have a firewall?

Yes. A firewall and antivirus software protect against different threats, so having one does not make the other unnecessary. A firewall controls network traffic to help block unauthorised connections, while antivirus software detects, blocks and removes malicious files and programmes on your device. Use both, keep them up to date and follow good security practices for more complete protection.

What are the 3 types of firewalls?

The three commonly recognised types of firewall are packet-filtering, stateful inspection and proxy firewalls. Packet-filtering firewalls assess traffic using details such as IP addresses and port numbers; stateful inspection firewalls also track active connections to determine whether traffic is expected; and proxy firewalls act as intermediaries between users and online services, inspecting requests before passing them on. Modern firewalls may combine features from more than one type.

What is firewall and its uses?

A firewall is a security system that monitors and controls incoming and outgoing network traffic according to a set of rules. It can be built into a computer or router, installed on a network, or delivered as a cloud service. Its main uses include blocking unauthorised connections, helping protect devices and data from malicious traffic, restricting access to certain services, and recording network activity for monitoring. A firewall is an important layer of protection, but it should be used alongside measures such as software updates, strong passwords and anti-malware tools.

How do I turn on firewall protection?

To turn on firewall protection, open the security or network settings on your device and enable its built-in firewall. On Windows, go to Windows Security, select Firewall & network protection, choose each network profile you use and switch Microsoft Defender Firewall on. On a Mac, open System Settings, select Network, then Firewall, and turn it on. Menu names may vary by operating system or version. If you use a router or business network, check its settings or ask your IT administrator before making changes, as existing security rules may be managed centrally.

Managed Security Services: A Practical Guide for Businesses

Cyber security is an ongoing responsibility. Threats change, systems grow and businesses must protect their data while keeping day-to-day operations running. For organisations without the people or resources to manage every security task in-house, managed security services can provide specialist support.

What are managed security services?

Managed security services are cyber security functions delivered and supported by an external provider. The provider may monitor systems, help detect threats, manage security tools and assist with incident response. Services are usually tailored to an organisation’s size, technology and risk profile.

A managed security service provider (MSSP) may work alongside an internal IT or security team, or take responsibility for specific functions that the organisation does not manage itself. The scope should be clearly agreed, including what the provider will do, when it will do it and how it will report potential issues.

Common managed security services

The services available vary between providers, but often include:

  • Security monitoring: Reviewing alerts and activity across networks, devices, cloud services and other systems.
  • Threat detection: Identifying suspicious behaviour that may indicate an attempted or successful attack.
  • Incident response support: Helping an organisation investigate and contain security incidents, and recover afterwards.
  • Vulnerability management: Finding weaknesses in systems and helping to prioritise remediation.
  • Firewall and endpoint management: Configuring, maintaining or monitoring security controls on networks and devices.
  • Identity and access monitoring: Reviewing access, account activity and changes to permissions, including within directory services.
  • Security reporting: Providing regular updates on alerts, incidents, risks and service performance.
  • Compliance support: Helping gather evidence and improve security processes relevant to applicable standards or regulations.

Why do organisations use managed security services?

Access to specialist skills: Security teams need a broad and frequently updated skill set. An external provider can offer access to expertise that may be difficult or costly to maintain internally.

Additional monitoring capacity: Some services provide monitoring outside normal working hours. This can help organisations respond to suspicious activity sooner, depending on the provider’s coverage and agreed service levels.

Support for existing teams: Managed services can take on defined operational tasks, allowing internal staff to focus on business systems, strategic improvements and other priorities.

More consistent processes: A well-run service can introduce repeatable approaches to alert handling, reporting and escalation. This makes it easier to understand what has happened and who is responsible for the next step.

Scalable support: Services can often be adjusted as an organisation changes its systems, workforce or risk profile. The contract should make clear how changes in scope or usage affect delivery and cost.

What to consider when choosing a provider

Managed security services involve trust and access to important systems, so selecting a provider requires careful assessment. Consider the following questions:

  • Which systems, users and security functions are included in the service?
  • What is monitored, and during which hours?
  • How are alerts assessed, prioritised and escalated?
  • Who is authorised to take action, such as disabling an account or isolating a device?
  • What response times and reporting commitments are written into the agreement?
  • How will the provider protect any data it handles or stores?
  • What experience does the provider have with the organisation’s technology and sector?
  • How will the service work with internal IT, security, legal and management teams?
  • What happens at the end of the contract, including the return or deletion of data?

Ask for clear explanations of the provider’s methods and limitations. A service description should distinguish between detecting an issue, investigating it and taking action to resolve it. These are different responsibilities and may not all be included in the same package.

Managed services and internal responsibility

Using an external provider does not remove an organisation’s responsibility for its security. The organisation still needs to set risk priorities, manage access to its systems and make decisions about business impact. Staff should know how to report concerns, while senior leaders should understand the risks and the service being purchased.

Clear ownership is particularly important during an incident. The organisation and provider should agree who leads the response, who can authorise disruptive actions and how relevant teams will be contacted. Contact details and escalation routes should be tested before they are needed.

Making managed security services effective

A provider can only deliver a useful service when it has accurate information about the environment it is protecting. Keep system inventories, network diagrams, contact lists and access arrangements up to date. Share planned changes that may affect monitoring, such as new cloud services or significant infrastructure updates.

Agree measurable service expectations and review performance regularly. Reports should help the organisation understand important risks and trends, rather than simply list technical alerts. Periodic reviews can identify gaps, refine priorities and ensure the service still matches the organisation’s needs.

Conclusion

Managed security services can strengthen an organisation’s ability to monitor systems, identify threats and respond to incidents. Their value depends on choosing the right scope, setting clear responsibilities and maintaining close communication between the provider and the organisation. With these foundations in place, managed support can complement internal capabilities and contribute to a more resilient security programme.


Essential Tips for Selecting and Managing Security Services

  1. Define clear security goals before choosing a provider.
  2. Check the provider’s certifications and track record.
  3. Agree service levels, response times and escalation routes.
  4. Confirm how your data will be protected and stored.
  5. Review monitoring coverage, including nights and weekends.
  6. Test incident response plans together regularly.
  7. Measure performance and review the service often.

Define clear security goals before choosing a provider.

Before choosing a managed security services provider, define the security goals your organisation needs to achieve. Decide which risks and systems matter most, whether you need round-the-clock monitoring, help with incident response, support for compliance or improved visibility of user activity. Clear priorities make it easier to compare providers, agree on the right scope and set measurable expectations. They also help ensure the service supports your organisation’s needs rather than simply adding more tools or reports.

Check the provider’s certifications and track record.

Check the provider’s certifications and track record before making a decision. Relevant, independently verified certifications can indicate that the provider follows recognised security practices, while case studies, references and years of experience can offer insight into the quality of its work. Ask how its expertise matches your systems and sector, and look for clear evidence of reliable service, effective incident handling and transparent reporting.

Agree service levels, response times and escalation routes.

Agree service levels, response times and escalation routes with your managed security services provider before the service begins. Set out what the provider is responsible for, how quickly alerts will be acknowledged and acted upon, and who will be contacted if an incident needs urgent attention. Clear, documented arrangements help avoid confusion during a security event and ensure the right people can make timely decisions.

Confirm how your data will be protected and stored.

Before choosing a managed security services provider, confirm how your data will be protected, where it will be stored and who can access it. Ask about encryption, access controls, backup arrangements, data retention and secure deletion, as well as how the provider will notify you of a breach. Make sure these safeguards are clearly documented in the contract and meet your organisation’s security and regulatory requirements.

Review monitoring coverage, including nights and weekends.

Review your monitoring coverage to make sure it matches when your organisation is most at risk. Check whether your provider monitors systems overnight, at weekends and on public holidays, and clarify how quickly alerts are assessed and escalated during those periods. If round-the-clock monitoring is not included, agree who will respond to critical alerts and ensure staff know how to contact them.

Test incident response plans together regularly.

Test your incident response plans regularly with your managed security provider, using realistic scenarios such as a compromised account or ransomware alert. These exercises help both teams practise their roles, check that escalation routes and contact details work, and identify gaps in communication or decision-making before a real incident occurs. Record the lessons learnt, update the plan and agree any follow-up actions.

Measure performance and review the service often.

Measure the performance of your managed security service against clear, agreed objectives, such as alert response times, incident handling and reporting quality. Review the service regularly with your provider to discuss results, recurring issues and changes to your organisation’s needs or systems. These conversations help identify gaps early, refine priorities and ensure the service continues to deliver meaningful security support.

Firewall Software: A Guide to Protecting Your Devices and Network

Firewall software helps protect computers and networks by monitoring incoming and outgoing internet traffic. It applies a set of security rules to decide which connections are allowed and which should be blocked. Used alongside other security measures, a firewall can help reduce exposure to unauthorised access and suspicious activity.

What Is Firewall Software?

A firewall acts as a barrier between a trusted device or network and other networks, including the internet. When data is sent or received, the firewall checks it against its rules. Depending on those rules, it may allow the traffic, block it or alert the user or administrator.

Firewalls are available as software, hardware or a combination of both. Firewall software runs on an individual computer or server, while a network firewall protects multiple devices by filtering traffic at the network boundary. Many routers also include basic firewall capabilities.

How Does a Firewall Work?

Firewalls use different methods to assess network traffic. Common approaches include:

  • Packet filtering: Checks details such as the source, destination and type of network traffic against predefined rules.
  • Stateful inspection: Tracks active connections and assesses traffic in the context of those connections.
  • Application-level filtering: Examines traffic associated with particular applications or services, rather than relying only on basic connection details.
  • Host-based monitoring: Runs on a device and can control which programmes are permitted to communicate over a network.

The capabilities available vary between products. Some firewall software focuses on straightforward connection controls, while more advanced solutions may offer central management, detailed logging and additional threat-detection features.

Types of Firewall Software

Personal Firewalls

Personal firewalls are designed for individual computers. They can help control connections made by applications and provide alerts about unfamiliar network activity. They are often included with an operating system or security suite.

Business and Enterprise Firewalls

Organisations may use centrally managed firewall software to apply consistent rules across computers, servers or cloud environments. These products can help administrators monitor activity, manage access and investigate security events. The right configuration depends on the organisation’s network, users and security requirements.

Cloud Firewalls

Cloud firewalls filter traffic to, from or between cloud-based services. They can be managed through a provider’s platform and configured to protect workloads that may not be located in a traditional office network.

Why Is Firewall Software Important?

A firewall can help organisations and individuals:

  • Block unwanted network connections.
  • Restrict communications to approved applications and services.
  • Reduce the risk of unauthorised access to devices and systems.
  • Monitor network activity and support security investigations.
  • Apply access rules that reflect business or household needs.

A firewall is not a complete security solution. It cannot, on its own, prevent every cyber attack, detect every harmful file or protect against unsafe behaviour. It should form part of a broader approach that includes software updates, strong authentication, secure backups and appropriate endpoint protection.

How to Choose Firewall Software

Before selecting firewall software, consider how it will be used and who will manage it. Useful factors to assess include:

  • Compatibility: Check that the software supports your operating systems, devices and network environment.
  • Management: Consider whether you need controls for one device or central administration across many devices.
  • Visibility: Look for clear logs and alerts that make it possible to understand what the firewall is blocking or allowing.
  • Usability: Rules should be manageable without making legitimate work unnecessarily difficult.
  • Support and updates: Check how the provider handles security updates, product maintenance and technical support.
  • Cost and licensing: Review the total cost, including subscriptions, deployment and ongoing administration.

For business use, it is also important to consider regulatory obligations, internal security policies and how the firewall will fit with existing monitoring and incident-response processes.

Firewall Best Practices

Careful configuration is essential. A firewall that is poorly maintained or set up with overly broad rules may offer less protection than expected. Good practices include:

  • Keep the firewall software and related systems up to date.
  • Use a default-deny approach where appropriate, allowing only the traffic required for legitimate tasks.
  • Review rules regularly and remove those that are no longer needed.
  • Limit administrative access and protect it with strong authentication.
  • Check logs and investigate unexpected activity.
  • Test rule changes to make sure essential services continue to work.
  • Document important settings and have a process for responding to alerts.

Firewall Software and Other Security Measures

Firewalls work best as part of a layered security strategy. They can be combined with antivirus or endpoint detection tools, multi-factor authentication, secure configuration, staff awareness training and regular backups. Network segmentation can also help limit the spread of an incident by separating systems according to their purpose and level of sensitivity.

For organisations using directory services such as Microsoft Active Directory, firewall rules should be planned carefully. Overly restrictive settings can disrupt authentication and other essential services, while overly permissive rules may expose systems unnecessarily. Changes should be tested and documented before being applied widely.

Conclusion

Firewall software is an important tool for controlling network traffic and reducing unwanted connections. Its effectiveness depends on choosing a solution that suits your environment, configuring it carefully and keeping its rules up to date. Combined with other security controls, a well-managed firewall can contribute to a more resilient approach to protecting devices, users and business systems.


Essential FAQs on Firewall Software: Understanding, Choosing, and Configuring Your Digital Defence

  1. What is firewall software and how does it work?
  2. Why do I need firewall software?
  3. What is the difference between a software firewall and a hardware firewall?
  4. Is the firewall built into my computer enough to protect me?
  5. Can firewall software slow down my computer or internet connection?
  6. How do I choose the right firewall software for my needs?
  7. How do I configure firewall software safely?
  8. Can firewall software protect me from viruses, malware and phishing attacks?

What is firewall software and how does it work?

Firewall software monitors incoming and outgoing network traffic and applies security rules to decide which connections to allow or block. It acts as a barrier between your device or network and other networks, such as the internet. Depending on the software, it may filter traffic based on details such as its source, destination, connection status or the application involved. By blocking unauthorised or suspicious connections, a firewall can help reduce security risks, although it should be used alongside other protections such as software updates, strong passwords and antivirus tools.

Why do I need firewall software?

Firewall software helps protect your computer or network by checking incoming and outgoing connections and blocking traffic that does not meet your security rules. It can reduce the risk of unauthorised access and help control which applications communicate online. A firewall is not a complete security solution, but alongside regular updates, strong passwords and other security tools, it adds an important layer of protection.

What is the difference between a software firewall and a hardware firewall?

A software firewall is installed on an individual computer or server and controls the network traffic entering and leaving that device. A hardware firewall is a physical appliance, or a firewall built into a router, that filters traffic between networks and can protect several devices at once. Software firewalls offer device-level control, while hardware firewalls provide network-wide protection; many organisations use both as part of a layered security approach.

Is the firewall built into my computer enough to protect me?

The firewall built into your computer provides a useful first layer of protection by controlling incoming and outgoing network connections, but it is not enough on its own to protect you from every online threat. Keep it switched on and up to date, and use it alongside other safeguards, such as regularly updated software, reputable anti-malware protection, strong passwords and multi-factor authentication. For businesses or people with more complex networks, additional firewall controls may also be appropriate.

Can firewall software slow down my computer or internet connection?

Firewall software can use some of your computer’s resources, but for most modern devices the impact is usually small. You may notice slower performance or internet speeds if the software is resource-intensive, poorly configured, out of date or running alongside several other security tools. If this happens, check for updates, review the firewall’s settings and close unnecessary programmes. Avoid switching off the firewall as a quick fix; if the problem continues, consult the software provider or your IT administrator.

How do I choose the right firewall software for my needs?

To choose the right firewall software, consider what you need to protect: a single computer, a home network or an organisation’s devices and cloud services. Check that the software is compatible with your systems, easy to manage and provides clear alerts and activity logs. Businesses may also need centralised controls, reporting and support for compliance requirements. Compare the features, ongoing costs, update policy and level of technical support, and make sure the firewall can work alongside your existing security tools. Choose a solution you can configure and maintain properly, as even capable software may offer limited protection if its rules are out of date or too permissive.

How do I configure firewall software safely?

Configure firewall software by starting with its recommended settings and allowing only the connections and applications you need. Keep the software updated, use strong authentication for administrator access, and avoid disabling the firewall to solve connection problems; instead, create a specific rule for the required traffic. Review rules and activity logs regularly, remove outdated permissions, and test changes to ensure essential services still work. For business networks, document changes and follow your organisation’s security policies.

Can firewall software protect me from viruses, malware and phishing attacks?

Firewall software can help block suspicious network connections and prevent unauthorised access, but it cannot protect you from every virus, malware infection or phishing attack. Some firewalls include extra security features, yet harmful files may still arrive through email, downloads or removable media, and phishing often relies on tricking people into revealing information. Use a firewall alongside reputable antivirus or endpoint protection, keep your software updated, and take care with unexpected links, attachments and requests for sensitive details.

The Power of pfSense: Enhancing Network Security and Performance

pfSense is an open-source firewall and routing platform that offers a wealth of features to enhance network security and performance. Developed based on FreeBSD, pfSense provides a robust, reliable, and cost-effective solution for businesses and individuals looking to fortify their network infrastructure.

Key Features of pfSense

One of the standout features of pfSense is its versatility. Whether you need a simple firewall or a comprehensive security solution, pfSense can be tailored to meet your specific requirements. Some key features include:

  • Firewall Protection: pfSense offers stateful packet filtering to protect your network from unauthorised access and malicious threats.
  • VPN Capabilities: With support for various VPN protocols, including OpenVPN and IPsec, pfSense enables secure remote access and site-to-site connectivity.
  • Quality of Service (QoS): Ensure optimal performance for critical applications by prioritising network traffic with QoS settings.
  • Intrusion Detection and Prevention: Detect and block suspicious activities with built-in IDS/IPS functionality.
  • Multi-WAN Support: Balance traffic across multiple internet connections for improved reliability and bandwidth management.

The Benefits of Using pfSense

Businesses and individuals can reap numerous benefits from implementing pfSense in their network infrastructure:

  • Enhanced Security: With advanced firewall capabilities and intrusion detection features, pfSense helps safeguard sensitive data from cyber threats.
  • Better Performance: Optimise network performance with QoS settings that prioritise important traffic, ensuring smooth operation of critical applications.
  • Cost-Effectiveness: As an open-source solution, pfSense eliminates the need for expensive proprietary hardware or software licenses, making it a budget-friendly choice for organisations of all sizes.
  • User-Friendly Interface: The intuitive web-based interface makes it easy to configure and manage firewall rules, VPN connections, and other settings without the need for extensive technical expertise.

In Conclusion

pfSense stands out as a powerful tool for enhancing network security and performance. Whether you are looking to strengthen your firewall protection, establish secure VPN connections, or optimise bandwidth usage, pfSense offers a comprehensive solution that can be customised to suit your specific needs. By leveraging the capabilities of pfSense, businesses and individuals can create a robust network infrastructure that is both secure and efficient.


Optimising Network Security and Performance: 8 Essential Tips for pfSense Users

  1. Regularly update your pfSense installation to ensure you have the latest security patches and features.
  2. Utilize aliases in pfSense to simplify firewall rule management and make configurations more efficient.
  3. Implement VPNs on pfSense for secure remote access and encrypted communication over untrusted networks.
  4. Take advantage of package management in pfSense to extend its functionality with additional features and services.
  5. Use VLANs in pfSense to segregate network traffic, improve security, and optimize network performance.
  6. Monitor system logs in pfSense to troubleshoot issues, identify security threats, and ensure smooth operation of your firewall.
  7. Set up multi-WAN load balancing in pfSense for increased reliability, bandwidth optimization, and fault tolerance.
  8. Configure port forwarding rules in pfSense to allow external access to internal services while maintaining network security.

Regularly update your pfSense installation to ensure you have the latest security patches and features.

It is crucial to regularly update your pfSense installation to stay ahead of potential security vulnerabilities and benefit from the latest features. By keeping your pfSense system up to date, you ensure that it is equipped with the most recent security patches, bug fixes, and enhancements released by the developers. This proactive approach not only helps in fortifying your network against emerging threats but also ensures that your pfSense firewall operates at its optimal performance level. Remember, staying current with updates is a fundamental step in maintaining a secure and reliable network infrastructure with pfSense.

Utilize aliases in pfSense to simplify firewall rule management and make configurations more efficient.

By utilising aliases in pfSense, users can streamline firewall rule management and enhance the efficiency of configurations. Aliases allow for the grouping of multiple IP addresses, networks, or ports under a single name, simplifying the creation and maintenance of firewall rules. This feature not only reduces the complexity of rule sets but also makes it easier to update configurations as needed. By leveraging aliases in pfSense, administrators can save time and effort while ensuring that their firewall rules remain organised and easy to manage.

Implement VPNs on pfSense for secure remote access and encrypted communication over untrusted networks.

By implementing VPNs on pfSense, users can ensure secure remote access and encrypted communication over untrusted networks. This powerful feature enables individuals and businesses to establish a secure connection to their network from remote locations, safeguarding sensitive data and communications from potential threats. With pfSense’s robust VPN capabilities, such as support for various protocols like OpenVPN and IPsec, users can enjoy peace of mind knowing that their information is protected as it travels across untrusted networks. This proactive approach to network security on pfSense enhances privacy, confidentiality, and overall data protection for users accessing their network remotely.

Take advantage of package management in pfSense to extend its functionality with additional features and services.

By utilising package management in pfSense, users can significantly enhance the capabilities of their firewall and routing platform. By installing additional packages, such as IDS/IPS systems, caching servers, or traffic monitoring tools, users can extend the functionality of pfSense to better suit their specific needs. This flexibility allows for customisation and scalability, empowering users to tailor their network security and performance to meet evolving requirements effectively.

Use VLANs in pfSense to segregate network traffic, improve security, and optimize network performance.

Utilising VLANs in pfSense is a strategic approach to segregating network traffic, enhancing security measures, and optimising network performance. By creating distinct virtual LANs within the network infrastructure, administrators can effectively isolate different types of traffic, such as guest Wi-Fi, IoT devices, and critical business applications. This segregation not only bolsters security by preventing unauthorised access to sensitive data but also allows for more efficient bandwidth management and prioritisation of network resources. Implementing VLANs in pfSense empowers organisations to customise their network architecture to meet specific needs while maintaining a robust level of control and protection over their digital assets.

Monitor system logs in pfSense to troubleshoot issues, identify security threats, and ensure smooth operation of your firewall.

Monitoring system logs in pfSense is a crucial tip for maintaining the security and efficiency of your firewall. By regularly checking system logs, you can troubleshoot issues promptly, identify potential security threats, and ensure the smooth operation of your network. System logs provide valuable insights into the activities and events occurring within your pfSense environment, allowing you to proactively address any anomalies or suspicious behaviour. By staying vigilant and proactive in monitoring system logs, you can enhance the overall effectiveness of your firewall and mitigate potential risks effectively.

Set up multi-WAN load balancing in pfSense for increased reliability, bandwidth optimization, and fault tolerance.

Setting up multi-WAN load balancing in pfSense is a strategic tip that can significantly enhance network performance and reliability. By configuring this feature, businesses can distribute traffic across multiple internet connections, thereby optimising bandwidth utilisation and ensuring uninterrupted connectivity. This setup not only improves overall network efficiency but also provides fault tolerance, as any issues with one connection can be seamlessly mitigated by diverting traffic to alternative links. In essence, implementing multi-WAN load balancing in pfSense is a proactive approach towards achieving increased reliability and maximising the potential of network resources.

Configure port forwarding rules in pfSense to allow external access to internal services while maintaining network security.

Configuring port forwarding rules in pfSense is a crucial step to enable external access to internal services without compromising network security. By setting up specific rules that redirect incoming traffic from designated ports to internal servers or devices, organisations can ensure that external users can access necessary services while maintaining a secure perimeter. This approach allows for the seamless operation of applications such as web servers, VPNs, or remote desktop services, all while controlling and monitoring the flow of traffic to prevent unauthorised access and potential security breaches. With careful configuration of port forwarding rules in pfSense, businesses can strike a balance between accessibility and security, enhancing their network infrastructure’s functionality and protection.

The Importance of Cyber Security Services

The Importance of Cyber Security Services

In today’s digital age, where businesses rely heavily on technology to operate efficiently, the need for robust cyber security services has never been greater. Cyber threats continue to evolve and pose significant risks to organisations of all sizes. Investing in professional cyber security services is essential to safeguard sensitive data, protect against malicious attacks, and ensure business continuity.

One of the primary benefits of cyber security services is the proactive approach they offer in identifying and mitigating potential threats. Experienced professionals utilise advanced tools and techniques to monitor networks, detect vulnerabilities, and respond swiftly to incidents. By staying ahead of cyber criminals, businesses can prevent costly data breaches and minimise downtime.

Furthermore, cyber security services help organisations comply with regulatory requirements and industry standards. Many sectors have strict guidelines regarding data protection and privacy, such as GDPR in Europe or HIPAA in healthcare. By enlisting the expertise of cyber security professionals, businesses can ensure they meet these obligations and avoid hefty fines for non-compliance.

Another crucial aspect of cyber security services is education and training. Human error remains one of the leading causes of security breaches, often due to lack of awareness or understanding of best practices. Cyber security providers offer training programmes to educate employees on how to recognise phishing attempts, create secure passwords, and follow protocols to safeguard company information.

Ultimately, investing in cyber security services is an investment in the future resilience and reputation of your business. By partnering with experts who specialise in protecting digital assets, you can focus on growing your organisation without constantly worrying about cyber threats lurking around the corner.


Essential Cyber Security: Addressing Key Questions for Business Protection

  1. What is cyber security and why is it important?
  2. How can a cyber security service protect my business?
  3. What are the common types of cyber threats I should be aware of?
  4. How do I choose the right cyber security service provider?
  5. What measures can be taken to prevent data breaches?
  6. How often should my business conduct a security audit?
  7. What steps are involved in responding to a cyber attack?
  8. Can small businesses benefit from professional cyber security services?
  9. How does employee training contribute to overall cyber security?

What is cyber security and why is it important?

Cyber security is the practice of protecting digital systems, networks, and data from malicious attacks or unauthorised access. It encompasses a range of strategies, technologies, and processes designed to safeguard sensitive information and ensure the integrity of digital assets. In today’s interconnected world, where cyber threats are constantly evolving, cyber security plays a crucial role in maintaining the confidentiality, availability, and integrity of data. Without adequate cyber security measures in place, organisations are vulnerable to data breaches, financial losses, reputational damage, and legal consequences. By prioritising cyber security, businesses can mitigate risks, protect their valuable assets, and maintain trust with customers and stakeholders in an increasingly digitised environment.

How can a cyber security service protect my business?

Cyber security services play a vital role in safeguarding businesses against a myriad of digital threats. By employing advanced technologies and expert knowledge, these services can protect your business in several ways. Firstly, they conduct thorough assessments of your IT infrastructure to identify vulnerabilities and implement robust security measures to prevent cyber attacks. Additionally, cyber security services offer real-time monitoring of network activities, enabling prompt detection and response to suspicious behaviour or potential breaches. Moreover, they provide regular updates and patches to ensure that your systems are equipped with the latest defences against evolving threats. Overall, investing in a cyber security service can significantly enhance the resilience of your business and mitigate the risks posed by cyber adversaries.

What are the common types of cyber threats I should be aware of?

It is crucial for individuals and organisations to be aware of the common types of cyber threats that pose risks to their digital security. Some prevalent cyber threats include malware, which encompasses viruses, ransomware, and spyware designed to infiltrate systems and steal data. Phishing attacks are another common threat, where malicious actors use deceptive emails or messages to trick users into divulging sensitive information. Additionally, DDoS (Distributed Denial of Service) attacks can overwhelm networks, causing disruptions in services. Being informed about these and other cyber threats is essential in implementing effective security measures to mitigate risks and protect against potential breaches.

How do I choose the right cyber security service provider?

When considering how to select the most suitable cyber security service provider for your organisation, several key factors should be taken into account. Firstly, assess the provider’s experience and track record in the field. Look for a company with a proven history of successfully protecting businesses from cyber threats. Additionally, consider the range of services offered and ensure they align with your specific needs, whether it be network monitoring, threat detection, or incident response. It is also essential to evaluate the provider’s certifications and compliance with industry standards to guarantee they adhere to best practices. Lastly, look for a partner who offers excellent customer support and demonstrates a commitment to ongoing communication and collaboration throughout your engagement with them. By carefully evaluating these aspects, you can confidently choose a cyber security service provider that meets your requirements and safeguards your digital assets effectively.

What measures can be taken to prevent data breaches?

Data breaches are a significant concern in today’s digital landscape, but there are proactive measures that can be implemented to help prevent them. One key step is to regularly update and patch software systems to address known vulnerabilities that cyber criminals may exploit. Implementing strong access controls, such as multi-factor authentication and least privilege access, can limit the exposure of sensitive data. Encrypting data both at rest and in transit adds an additional layer of protection. Conducting regular security awareness training for employees to educate them on common threats like phishing emails and social engineering can also help prevent data breaches by reducing the human error factor. Lastly, having a robust incident response plan in place can enable swift detection and containment of breaches, minimising their impact on the organisation.

How often should my business conduct a security audit?

It is recommended that businesses conduct a security audit regularly to ensure the ongoing protection of their digital assets. The frequency of security audits may vary depending on factors such as the size of the business, industry regulations, and the evolving nature of cyber threats. Typically, businesses should consider conducting security audits at least annually or more frequently if there have been significant changes in the IT infrastructure, such as system upgrades or expansions. Regular security audits help identify vulnerabilities, assess risks, and implement necessary measures to strengthen the overall security posture of the business against potential cyber attacks.

What steps are involved in responding to a cyber attack?

When responding to a cyber attack, several critical steps are involved to mitigate the impact and restore security. The first step is to identify and contain the breach by isolating affected systems to prevent further spread of the attack. Next, it is crucial to assess the extent of the damage and analyse how the breach occurred. This analysis helps in understanding the attacker’s tactics and strengthens defences against future attacks. Following this, organisations must notify relevant stakeholders, including internal teams, regulatory bodies, and possibly law enforcement agencies, depending on the severity of the incident. Finally, a comprehensive recovery plan should be implemented to restore systems, data, and operations back to normalcy while continuously monitoring for any signs of reoccurrence. Swift and coordinated action during a cyber attack response is essential in minimising disruption and safeguarding sensitive information.

Can small businesses benefit from professional cyber security services?

Small businesses can greatly benefit from professional cyber security services. While larger corporations often have dedicated IT departments and resources to manage cyber threats, small businesses are equally vulnerable to attacks but may lack the expertise and tools to effectively protect their digital assets. By investing in cyber security services tailored to their needs, small businesses can enhance their defences against cyber threats, safeguard sensitive data, maintain customer trust, and ensure business continuity. Professional cyber security services provide proactive monitoring, threat detection, incident response, and compliance assistance that can help small businesses mitigate risks and focus on their core operations with peace of mind.

How does employee training contribute to overall cyber security?

Employee training plays a pivotal role in bolstering overall cyber security within an organisation. By educating employees on best practices, recognising common threats, and understanding their role in maintaining a secure environment, organisations can significantly reduce the risk of cyber attacks. Well-trained employees are more vigilant against phishing attempts, better equipped to create strong passwords, and more likely to follow established security protocols. This increased awareness and knowledge empower employees to act as the first line of defence against potential threats, ultimately strengthening the organisation’s cyber security posture and minimising vulnerabilities.

Industrial Cybersecurity Services: Protecting Critical Operations

Industrial organisations rely on connected systems to keep production moving, maintain safety and deliver essential services. From manufacturing plants and energy facilities to water networks and transport infrastructure, operational technology (OT) is increasingly connected to corporate IT, suppliers and the wider internet. This connectivity can improve efficiency, but it also creates new cybersecurity risks.

Industrial cybersecurity services help organisations understand and manage those risks while keeping essential operations safe and reliable. Effective protection takes account of the unique demands of industrial environments, where availability, safety and continuity are just as important as confidentiality.

What are industrial cybersecurity services?

Industrial cybersecurity services are designed to protect the technologies used to monitor and control physical processes. These may include industrial control systems (ICS), supervisory control and data acquisition (SCADA) systems, programmable logic controllers (PLCs), engineering workstations, sensors and other OT assets.

Unlike many conventional IT systems, industrial equipment can remain in service for decades. Some devices cannot be easily updated or taken offline, and even a brief interruption may affect production or create safety concerns. Security measures therefore need to be tailored to the environment, its equipment and its operational requirements.

Core services

OT asset discovery and risk assessment

It is difficult to protect systems that an organisation cannot see. Asset discovery helps identify devices, software, connections and communication pathways across an industrial network. A risk assessment can then highlight weaknesses, unsupported equipment, unnecessary access and potential routes an attacker could use.

Assessments should be planned carefully to avoid disrupting sensitive systems. Passive monitoring is often used to gather information without actively probing devices or affecting production.

Network segmentation

Separating industrial networks from corporate IT can limit the spread of malware and restrict unauthorised access. Segmentation divides a network into controlled zones, with carefully managed connections between them. This can reduce the impact of a compromised account or device and help keep critical processes isolated.

Continuous monitoring and threat detection

Monitoring can help security teams spot unusual activity, such as unexpected changes to a controller, unfamiliar devices joining the network or communication outside normal operating patterns. Industrial monitoring tools can provide visibility into OT protocols and behaviours that conventional IT security products may not recognise.

Alerts are most useful when they are prioritised and understood in context. Combining technical monitoring with knowledge of the plant’s processes can help teams distinguish genuine threats from routine operational activity.

Vulnerability and patch management

Industrial systems may contain vulnerabilities that cannot be fixed immediately because updates require testing, maintenance windows or vendor approval. A structured vulnerability management programme helps organisations assess exposure, prioritise remediation and consider alternatives where patching is not practical.

Those alternatives may include isolating a device, restricting access, adding monitoring or changing firewall rules. The right approach depends on the level of risk and the potential effect on safe operations.

Incident response and recovery

An industrial cyber incident can affect production, safety and the supply chain. Incident response planning helps teams understand who should act, how systems can be isolated and how operations can be restored safely. Plans should cover both IT and OT, with clear responsibilities for security teams, engineers, site managers and external partners.

Regular exercises can test whether response procedures work in practice. Recovery planning should include trusted backups, system configurations, engineering documentation and procedures for verifying that equipment is safe before it returns to service.

Employee training and security awareness

People play an important role in industrial security. Engineers, operators, IT staff and contractors may all have access to sensitive systems. Role-specific training can help them recognise suspicious activity, use remote access securely and report concerns promptly.

Standards, regulation and good practice

Industrial organisations may need to meet sector-specific regulations, contractual requirements or recognised security frameworks. Standards such as the IEC 62443 series provide guidance for securing industrial automation and control systems. Requirements vary by sector and location, so organisations should confirm which obligations apply to their operations.

Compliance is not a substitute for security. A useful programme connects governance and documentation with practical controls, ongoing monitoring and regular review.

Choosing an industrial cybersecurity provider

When evaluating a service provider, consider its experience with OT environments and its ability to work safely around live operations. Ask how assessments are conducted, how findings are prioritised and whether recommendations account for legacy equipment and production constraints.

  • Look for a clear understanding of industrial processes and safety requirements.
  • Confirm how access to sensitive systems is controlled and documented.
  • Ask how the provider supports incident response and recovery planning.
  • Check that recommendations are practical, prioritised and suited to your environment.
  • Agree how findings, risks and progress will be reported to technical and business teams.

A practical approach to protecting industrial operations

Industrial cybersecurity is an ongoing process, not a one-off project. Organisations can begin by building an accurate asset inventory, identifying critical processes and understanding the connections between IT and OT. From there, they can prioritise the most significant risks, improve access controls, strengthen network boundaries and prepare for incidents.

Well-designed industrial cybersecurity services help organisations reduce exposure without losing sight of operational realities. By combining specialist expertise, appropriate technology and clear procedures, businesses can improve resilience, protect people and assets, and support the reliable delivery of essential operations.


Enhancing Industrial Security: 8 Key Benefits of Cybersecurity Services

  1. Protects critical industrial systems from cyber threats.
  2. Helps reduce operational downtime.
  3. Improves visibility across IT and OT networks.
  4. Identifies vulnerabilities before attackers can exploit them.
  5. Supports safer, more reliable operations.
  6. Strengthens incident response and recovery.
  7. Helps meet relevant security standards and requirements.
  8. Provides expert guidance tailored to industrial environments.


Challenges in Implementing Industrial Cybersecurity Services: Key Considerations

  1. Can be costly to implement and maintain
  2. May require specialist expertise
  3. Assessments can disrupt operations if poorly planned
  4. Legacy equipment may be difficult to secure
  5. Integrating tools can be complex
  6. False alarms can burden security teams
  7. Results depend on ongoing monitoring and follow-up

Protects critical industrial systems from cyber threats.

Industrial cybersecurity services help protect critical systems such as industrial control and monitoring equipment from cyber threats. By identifying vulnerabilities, monitoring for unusual activity and strengthening access controls, they can reduce the risk of unauthorised access, disruption or damage. This helps keep essential operations running safely and reliably.

Helps reduce operational downtime.

Industrial cybersecurity services help reduce operational downtime by identifying vulnerabilities and suspicious activity before they cause disruption. Continuous monitoring, risk assessments and well-prepared incident response plans can help teams contain threats quickly and restore affected systems safely. This supports more reliable production, protects essential processes and helps avoid the cost and disruption of unplanned outages.

Improves visibility across IT and OT networks.

Industrial cybersecurity services improve visibility across IT and OT networks by helping organisations identify connected devices, understand how systems communicate and spot unusual activity. This joined-up view can reveal unauthorised connections, overlooked assets and potential pathways between corporate and operational environments. With clearer insight into their network, teams can investigate risks sooner and make better-informed decisions while keeping essential operations in mind.

Identifies vulnerabilities before attackers can exploit them.

Industrial cybersecurity services help identify vulnerabilities before attackers can exploit them. By assessing systems, monitoring network activity and reviewing access controls, specialists can uncover outdated software, misconfigurations and other weaknesses that might otherwise go unnoticed. Organisations can then prioritise fixes or introduce suitable safeguards, reducing the likelihood that a vulnerability will lead to disruption, data loss or damage to critical operations.

Supports safer, more reliable operations.

Industrial cybersecurity services support safer, more reliable operations by helping organisations identify threats and weaknesses before they disrupt critical processes. Monitoring, access controls and network segmentation can reduce the risk of unauthorised changes or system outages, while incident response and recovery planning help teams act quickly when problems arise. By tailoring security measures to the needs of industrial equipment and workflows, organisations can strengthen protection without compromising safety or operational continuity.

Strengthens incident response and recovery.

Industrial cybersecurity services strengthen incident response and recovery by helping organisations prepare for threats before they disrupt operations. Specialists can develop clear response plans, define responsibilities across IT and operational technology teams, and run exercises to test how effectively staff can detect, contain and manage an incident. They can also help establish secure backups and recovery procedures, so critical systems can be restored safely and efficiently. This preparation can reduce downtime, limit the impact on production and support a more resilient return to normal operations.

Helps meet relevant security standards and requirements.

Industrial cybersecurity services can help organisations understand and meet the security standards and regulatory requirements relevant to their sector. Specialists can assess existing controls, identify gaps and recommend practical improvements, while helping teams maintain the documentation and evidence needed for audits. This supports a more consistent approach to compliance and strengthens the protection of industrial systems.

Provides expert guidance tailored to industrial environments.

Industrial cybersecurity services provide expert guidance that reflects the realities of industrial environments, including legacy equipment, safety requirements and the need to keep operations running. Specialists can assess the risks to operational technology, recommend practical security measures and help organisations prioritise improvements without disrupting critical processes.

Can be costly to implement and maintain

Industrial cybersecurity services can be costly to implement and maintain, particularly for organisations with complex operations or legacy equipment. Expenses may include specialist assessments, monitoring tools, system upgrades, staff training and ongoing support. Regular maintenance is also needed to keep controls effective as threats and operational requirements change. For smaller businesses, these costs can make it challenging to protect every system at once, so careful planning and prioritisation are essential.

May require specialist expertise

Industrial cybersecurity services may require specialist expertise because operational technology environments are complex and differ significantly from conventional IT systems. Providers need to understand industrial equipment, control processes and safety requirements, while internal teams may need additional training to manage the recommended tools and procedures. This expertise can be difficult or costly to source, particularly for smaller organisations, and relying on external specialists may also make it harder to build in-house capability over time.

Assessments can disrupt operations if poorly planned

Assessments can disrupt industrial operations if they are not carefully planned. Active scans, system tests or changes to network settings may affect sensitive equipment, interrupt production or create safety risks. Before work begins, the provider should understand the site’s processes, agree suitable timings with operational teams and use methods appropriate for live systems. Clear communication and safeguards help ensure that security testing identifies weaknesses without unnecessarily affecting day-to-day operations.

Legacy equipment may be difficult to secure

Legacy equipment can be difficult to secure because older industrial devices may no longer receive software updates or support modern security controls. Replacing them can be costly and disruptive, while patching or scanning them may affect essential operations. Organisations may need to manage these risks through compensating measures, such as network segmentation, restricted access and continuous monitoring, which can add complexity and expense.

Integrating tools can be complex

Integrating industrial cybersecurity tools can be complex, particularly in environments with a mix of legacy equipment, specialist OT systems and newer IT platforms. Solutions may use different protocols, data formats and management processes, making it difficult to share information or achieve a clear, unified view of risk. Implementation can also require careful testing and coordination to avoid disrupting production or affecting safety. As a result, integration may take more time and resources than expected, and organisations may need specialist support to ensure new tools work reliably with existing systems.

False alarms can burden security teams

False alarms can place a significant burden on security teams, particularly when monitoring systems generate frequent alerts about harmless or routine activity. Investigating each alert takes time and can distract staff from genuine threats, increasing the risk of alert fatigue. Over time, teams may become slower to respond or overlook important warnings. Tuning detection rules, adding context to alerts and regularly reviewing monitoring settings can help reduce unnecessary notifications and keep attention focused on incidents that matter.

Results depend on ongoing monitoring and follow-up

One potential drawback of industrial cybersecurity services is that their effectiveness depends on ongoing monitoring and follow-up. A one-off assessment may identify vulnerabilities, but risks can change as systems, threats and business operations evolve. Organisations need to review alerts, act on recommendations, maintain security controls and reassess their environment regularly. This requires sustained time, expertise and investment; without it, important findings may go unresolved and the benefits of the service can diminish.

The Importance of Cybersecurity Compliance Services

In today’s digital age, where cyber threats are becoming increasingly sophisticated and prevalent, ensuring the security of your organisation’s data and IT infrastructure is paramount. Cybersecurity compliance services play a crucial role in helping businesses adhere to regulatory requirements and industry standards to protect sensitive information and mitigate risks.

What Are Cybersecurity Compliance Services?

Cybersecurity compliance services encompass a range of measures designed to ensure that an organisation’s security practices align with relevant laws, regulations, and standards. These services help businesses establish and maintain robust cybersecurity protocols to safeguard against data breaches, cyber attacks, and other malicious activities.

The Benefits of Cybersecurity Compliance Services

By investing in cybersecurity compliance services, organisations can enjoy a multitude of benefits, including:

  • Legal Compliance: Ensuring that your business meets all legal requirements related to data protection and cybersecurity regulations.
  • Risk Mitigation: Identifying potential vulnerabilities and implementing controls to reduce the risk of security incidents.
  • Enhanced Security: Implementing best practices for securing networks, systems, and data assets.
  • Reputation Protection: Demonstrating to customers, partners, and stakeholders that your organisation takes cybersecurity seriously.
  • Cost Savings: Avoiding costly fines, penalties, and remediation expenses associated with non-compliance.

Key Components of Cybersecurity Compliance Services

Cybersecurity compliance services typically include the following key components:

  • Risk Assessment: Identifying potential threats and vulnerabilities within the organisation’s IT infrastructure.
  • Policies and Procedures Development: Establishing clear guidelines for employees on how to handle sensitive information securely.
  • Security Audits: Conducting regular audits to assess the effectiveness of existing security controls.
  • Incident Response Planning: Developing protocols for responding to security incidents promptly and effectively.

The Future of Cybersecurity Compliance

As cyber threats continue to evolve, cybersecurity compliance services will play an increasingly vital role in helping businesses stay ahead of potential risks. By partnering with experienced cybersecurity professionals and leveraging advanced technologies, organisations can establish a strong security posture that protects their valuable assets from cyber attacks.

In conclusion, investing in cybersecurity compliance services is not just a regulatory obligation; it is a strategic imperative for any business looking to safeguard its reputation, mitigate risks, and secure its future in an increasingly digital world.


Essential Tips for Ensuring Cybersecurity Compliance: A Guide to Protecting Your Organisation

  1. Regularly review and update your cybersecurity policies and procedures.
  2. Ensure that your staff receive regular training on cybersecurity best practices.
  3. Implement strong access controls to protect sensitive data.
  4. Conduct regular security assessments and audits to identify vulnerabilities.
  5. Stay informed about the latest cybersecurity threats and trends.
  6. Encrypt sensitive data both at rest and in transit to enhance security.
  7. Maintain compliance with relevant regulations and standards in the industry.

Regularly review and update your cybersecurity policies and procedures.

It is essential for organisations to regularly review and update their cybersecurity policies and procedures to ensure they remain effective against evolving cyber threats. By staying proactive in assessing and refining security measures, businesses can better protect their valuable data and IT infrastructure. Regular reviews help identify any gaps or weaknesses in existing policies, allowing for timely adjustments to strengthen overall cybersecurity posture. Updating policies in line with the latest industry standards and best practices ensures that organisations are well-prepared to address emerging threats and maintain compliance with regulatory requirements.

Ensure that your staff receive regular training on cybersecurity best practices.

It is crucial to ensure that your staff receive regular training on cybersecurity best practices to strengthen your organisation’s security posture. By educating employees on the latest threats, phishing scams, password hygiene, and data handling procedures, you empower them to become proactive defenders against cyber attacks. Regular training sessions not only enhance awareness but also instil a culture of cybersecurity consciousness throughout the organisation, reducing the likelihood of human error leading to security breaches. Investing in continuous staff training is a proactive approach towards bolstering your cybersecurity defences and safeguarding sensitive information from potential threats.

Implement strong access controls to protect sensitive data.

Implementing strong access controls is a critical aspect of cybersecurity compliance services to safeguard sensitive data. By restricting access to authorised personnel only, organisations can prevent unauthorised users from compromising valuable information. Strong access controls involve implementing multi-factor authentication, role-based permissions, and regular monitoring of user activities to ensure that data remains secure and confidential. By enforcing stringent access controls, businesses can significantly reduce the risk of data breaches and maintain compliance with regulatory requirements, ultimately enhancing their overall cybersecurity posture.

Conduct regular security assessments and audits to identify vulnerabilities.

Conducting regular security assessments and audits is a critical tip in cybersecurity compliance services. By proactively evaluating your organisation’s IT infrastructure, you can identify vulnerabilities and potential weaknesses that may expose your data to cyber threats. These assessments help in understanding the effectiveness of existing security controls and implementing necessary measures to strengthen your defences. By staying vigilant and conducting frequent audits, you can stay one step ahead of cyber attackers and ensure that your cybersecurity practices remain robust and compliant with regulations.

Staying informed about the latest cybersecurity threats and trends is a crucial aspect of maintaining strong cybersecurity compliance services. By keeping abreast of evolving cyber threats and industry trends, organisations can proactively identify potential risks and adjust their security measures accordingly. Regularly monitoring cybersecurity news, attending industry conferences, and engaging with cybersecurity experts can provide valuable insights that help businesses stay one step ahead of cyber attackers. Being informed allows organisations to adapt their security strategies to address emerging threats effectively, ultimately enhancing their overall cybersecurity posture and ensuring compliance with relevant regulations.

Encrypt sensitive data both at rest and in transit to enhance security.

Encrypting sensitive data both at rest and in transit is a fundamental practice in cybersecurity compliance services. By applying encryption techniques to data stored on servers or devices and data transmitted between systems, organisations can significantly enhance their security posture. Encryption ensures that even if unauthorised individuals gain access to the data, they cannot decipher its contents without the encryption key. This proactive measure not only helps protect sensitive information from cyber threats but also demonstrates a commitment to maintaining the confidentiality and integrity of data, in line with regulatory requirements and industry best practices.

Maintain compliance with relevant regulations and standards in the industry.

It is crucial for businesses to maintain compliance with relevant regulations and standards in the industry when it comes to cybersecurity. By adhering to established guidelines and requirements, organisations can demonstrate their commitment to protecting sensitive data and ensuring the security of their IT infrastructure. Compliance with industry regulations not only helps mitigate risks associated with cyber threats but also enhances trust with customers, partners, and stakeholders. Regularly reviewing and updating security protocols in line with regulatory changes is essential to staying ahead of potential vulnerabilities and safeguarding against costly breaches.

Top Cybersecurity Threats

The Top Cybersecurity Threats Facing Businesses Today

In today’s digital age, businesses face an increasing number of cybersecurity threats that can compromise sensitive data, disrupt operations, and damage reputation. It is crucial for organisations to stay vigilant and proactive in defending against these threats. Here are some of the top cybersecurity threats that businesses need to be aware of:

Phishing Attacks

Phishing attacks involve sending deceptive emails or messages to trick individuals into revealing sensitive information such as login credentials or financial details. These attacks are becoming more sophisticated, making it challenging for users to distinguish legitimate communications from fraudulent ones.

Ransomware

Ransomware is a type of malware that encrypts files on a victim’s system and demands payment in exchange for decryption. Ransomware attacks can cause significant financial losses and operational disruptions, making them a serious threat to businesses of all sizes.

Data Breaches

Data breaches involve the unauthorised access or exposure of confidential information, such as customer data or intellectual property. Breaches can result from various factors, including weak security controls, insider threats, or vulnerabilities in software systems.

Insider Threats

Insider threats refer to risks posed by individuals within an organisation who misuse their access privileges to intentionally or unintentionally harm the company’s security posture. These threats can come from employees, contractors, or partners with insider knowledge of the organisation’s systems.

DDoS Attacks

Distributed Denial of Service (DDoS) attacks aim to overwhelm a target system with a flood of traffic, causing it to become inaccessible to legitimate users. DDoS attacks can disrupt online services, leading to downtime and financial losses for businesses.

Businesses must implement robust cybersecurity measures to mitigate these threats effectively. This includes conducting regular security assessments, educating employees on best practices, implementing multi-factor authentication, and keeping software systems up-to-date with security patches.

By staying informed about the latest cybersecurity trends and investing in proactive security measures, businesses can better protect themselves against evolving cyber threats and safeguard their valuable assets.


Understanding the Top 8 Frequently Asked Questions About Current Cybersecurity Threats

  1. What are the 3 major threats to cyber security today?
  2. What is 90% of cyber attacks?
  3. What are the 5 main threats to our cyber security?
  4. What are the 8 main cyber security threats?
  5. What are the top 5 major threats to cybersecurity?
  6. What is the #1 cybersecurity threat today?
  7. What are the biggest security threats right now?
  8. What are the 7 types of cyber security threats?

What are the 3 major threats to cyber security today?

In today’s digital landscape, the three major threats to cybersecurity that organisations face are phishing attacks, ransomware incidents, and data breaches. Phishing attacks involve deceptive tactics to trick individuals into disclosing sensitive information, while ransomware encrypts files and demands payment for decryption. Data breaches expose confidential data to unauthorised parties, leading to financial and reputational damage. These threats underscore the importance of robust cybersecurity measures to protect against evolving risks in the digital realm.

What is 90% of cyber attacks?

One frequently asked question regarding top cybersecurity threats is, “What constitutes 90% of cyber attacks?” It is widely acknowledged that a significant portion of cyber attacks, approximately 90%, are attributed to human error or negligence. This includes factors such as falling victim to phishing scams, using weak passwords, failing to update software promptly, or inadvertently disclosing sensitive information. Addressing these human-centric vulnerabilities through comprehensive training, robust security policies, and regular awareness campaigns is crucial in mitigating the majority of cyber threats faced by organisations today.

What are the 5 main threats to our cyber security?

In the realm of cybersecurity, it is crucial to understand the five main threats that pose significant risks to our digital safety. These threats include phishing attacks, which aim to deceive individuals into disclosing sensitive information; ransomware, a type of malware that encrypts files and demands payment for decryption; data breaches, where confidential information is exposed without authorisation; insider threats, which involve malicious or unintentional actions by individuals within an organisation; and Distributed Denial of Service (DDoS) attacks, designed to overwhelm systems with traffic. Awareness of these top cybersecurity threats is essential for businesses and individuals to enhance their defences and protect against potential cyber incidents.

What are the 8 main cyber security threats?

When it comes to cybersecurity, understanding the eight main cyber security threats is crucial for businesses and individuals alike. These threats encompass a range of risks, including phishing attacks, ransomware, data breaches, insider threats, DDoS attacks, malware infections, social engineering scams, and IoT vulnerabilities. Each threat poses unique challenges and requires specific preventive measures to mitigate potential damage. By staying informed about these top cyber security threats and implementing robust security practices, organisations can better protect their digital assets and reduce the risk of falling victim to malicious activities in today’s interconnected world.

What are the top 5 major threats to cybersecurity?

When it comes to cybersecurity, understanding the top 5 major threats is crucial for organisations to fortify their defences effectively. The landscape of cyber threats is ever-evolving, but some persistent dangers continue to pose significant risks. These include phishing attacks, where deceptive emails aim to trick individuals into divulging sensitive information; ransomware, a type of malware that encrypts files and demands payment for decryption; data breaches that expose confidential information; insider threats from individuals within the organisation misusing access privileges; and Distributed Denial of Service (DDoS) attacks that overwhelm systems with traffic. Staying informed about these prevalent threats allows businesses to implement targeted security measures and mitigate potential risks proactively.

What is the #1 cybersecurity threat today?

The question of what constitutes the number one cybersecurity threat today is a complex and dynamic issue, as the threat landscape continues to evolve rapidly. However, one prevalent and persistent threat that consistently ranks high on the list is phishing attacks. Phishing attacks involve deceptive tactics aimed at tricking individuals into divulging sensitive information, such as login credentials or financial details. These attacks are often sophisticated and can target individuals across various industries and sectors, highlighting the importance of robust cybersecurity measures and ongoing awareness training to mitigate the risks associated with phishing.

What are the biggest security threats right now?

Currently, the biggest security threats in the cybersecurity landscape encompass a range of sophisticated and evolving risks that organisations must contend with. From the pervasive threat of phishing attacks that target unsuspecting individuals to the insidious spread of ransomware that can cripple entire systems, businesses face a multitude of challenges in safeguarding their digital assets. Data breaches, whether due to external hackers or insider threats, continue to pose significant risks to sensitive information. Additionally, the persistent threat of Distributed Denial of Service (DDoS) attacks looms large, capable of disrupting online services and causing substantial financial harm. Staying vigilant and implementing robust security measures are essential in mitigating these top cybersecurity threats and fortifying defences against malicious actors.

What are the 7 types of cyber security threats?

In the realm of cybersecurity, understanding the various types of threats is essential for safeguarding digital assets. The seven primary types of cyber security threats include malware, phishing attacks, ransomware, insider threats, DDoS attacks, SQL injection, and zero-day exploits. Each threat poses unique risks to organisations and individuals, highlighting the importance of implementing robust security measures and staying vigilant against evolving cyber threats. By staying informed about these common threat vectors and adopting proactive security practices, businesses can enhance their resilience against potential cyber attacks.

Cybersecurity Compliance Consulting: A Practical Guide for UK Organisations

Cybersecurity compliance can be challenging to manage. Organisations must protect sensitive information, demonstrate that appropriate controls are in place and keep pace with changing legal and industry requirements. Cybersecurity compliance consulting helps make that work more structured, practical and proportionate to an organisation’s risks.

A consultant can assess existing security arrangements, identify gaps and help develop a clear plan for addressing them. The aim is not simply to prepare for an audit or achieve a certificate. It is to build security practices that support the organisation’s operations and stand up to scrutiny over time.

What is cybersecurity compliance consulting?

Cybersecurity compliance consulting is professional guidance on meeting relevant security standards, regulations and contractual obligations. The scope depends on the organisation’s sector, size, customers, systems and the information it handles.

Consultants may help an organisation understand which requirements apply, assess current controls and prepare evidence that shows how those controls work. They can also advise on policies, risk management, incident response, supplier security and staff awareness.

Compliance is not the same as security. Compliance focuses on meeting defined requirements, while security involves reducing the likelihood and impact of real-world threats. A strong programme connects the two: it meets applicable obligations while addressing the risks most relevant to the organisation.

Why compliance matters

Cybersecurity requirements can come from several sources, including legislation, industry standards, customer contracts and internal policies. Depending on the organisation, relevant considerations may include data protection duties, payment card requirements, sector-specific rules or recognised security frameworks.

Failing to manage these obligations can lead to regulatory action, contractual disputes, disruption and loss of customer confidence. Even where an organisation has no formal certification requirement, customers and business partners may expect it to demonstrate sound security practices.

A well-managed compliance programme can also provide practical benefits. It can clarify responsibilities, make risks easier to prioritise, improve incident readiness and give leadership a more reliable view of the organisation’s security posture.

What does a compliance consultant do?

The work should be tailored to the organisation rather than based on a generic checklist. Typical activities include:

  • Scoping requirements: identifying the laws, standards, contractual terms and customer expectations that apply.
  • Assessing current controls: reviewing policies, processes, technology and evidence against the relevant requirements.
  • Identifying gaps and risks: distinguishing urgent weaknesses from lower-priority improvements.
  • Developing a remediation plan: setting out actions, owners, dependencies and realistic timescales.
  • Improving documentation: helping create or update policies, procedures, risk registers and response plans.
  • Preparing for assessment: organising evidence and helping teams understand what an auditor or assessor may need to verify.
  • Supporting ongoing compliance: establishing processes for reviews, monitoring, staff training and continual improvement.

Consultants may also support technical work, such as reviewing access controls, vulnerability management, backup arrangements or security monitoring. The precise scope should be agreed in advance, including what is advisory and what requires implementation by the organisation or its technology providers.

A typical consulting process

Define the scope

The organisation and consultant agree which business units, systems, locations and information are in scope. Clear boundaries help prevent missed requirements and reduce unnecessary work.

Understand the business and its risks

The consultant gathers information about business operations, key services, data flows, suppliers and existing security arrangements. This context is essential: the same control may need to be applied differently in different organisations.

Review controls and evidence

Policies and technical settings are considered alongside evidence of how processes operate in practice. A written policy alone may not demonstrate that a control is consistently followed.

Prioritise improvements

Findings are translated into an action plan. Priorities should take account of the potential impact of a weakness, applicable deadlines, business constraints and the effort required to address it.

Implement and verify

Control improvements are put into practice, with responsibilities assigned to appropriate staff. Follow-up reviews help confirm that actions have been completed and are working as intended.

Maintain the programme

Compliance needs ongoing attention. Changes to systems, suppliers, business activities and requirements can affect the organisation’s obligations and risk profile. Regular reviews help keep controls relevant.

Choosing the right consultant

A useful consulting engagement depends on experience, independence and a good understanding of the organisation’s needs. When evaluating providers, consider asking:

  • Have they worked with organisations of a similar size or in a similar sector?
  • Can they explain the relevant requirements in clear, practical language?
  • Will the assessment be tailored to the organisation’s actual risks and systems?
  • What will the final deliverables include, and who will own each recommended action?
  • How will sensitive information gathered during the engagement be protected?
  • Can they support remediation or future reviews, if required?
  • Are any potential conflicts of interest disclosed?

Be cautious of promises of guaranteed compliance or certification. A consultant can guide and support an organisation, but accountability for its controls and decisions remains with the organisation. Certification or regulatory outcomes may also depend on independent assessors and the evidence available.

Common challenges to avoid

Organisations sometimes treat compliance as a one-off project, focus only on documentation or attempt to address every finding at once. These approaches can create significant effort without delivering lasting improvements.

It is generally more effective to assign clear ownership, connect recommendations to business risks and maintain evidence as part of normal operations. Staff involvement matters too: controls are more likely to work when people understand their purpose and know what is expected of them.

Another common challenge is overlooking third parties. Suppliers may have access to systems or information, so their security arrangements and contractual responsibilities should be considered as part of the wider programme.

Making compliance part of everyday security

Cybersecurity compliance consulting can help turn complex requirements into manageable actions. The most valuable outcome is not a collection of documents, but a clear understanding of the organisation’s obligations, risks and responsibilities.

By combining expert guidance with active leadership, practical controls and regular review, organisations can build a compliance programme that supports both assurance and resilience. Requirements vary, so organisations should seek advice suited to their circumstances and obtain legal guidance where interpretation of the law is required.


Essential Tips for Effective Cybersecurity Compliance Consulting

  1. Map applicable regulations before starting.
  2. Assess current controls against each requirement.
  3. Prioritise gaps by risk and impact.
  4. Keep evidence organised and up to date.
  5. Review compliance regularly as rules change.

Map applicable regulations before starting.

Before starting a cybersecurity compliance project, map the regulations, standards and contractual requirements that apply to your organisation. These may vary according to your sector, the information you handle, where you operate and the services you provide. A clear requirements map helps define the project’s scope, avoid duplicated effort and focus resources on the controls and evidence that matter. Review it regularly, as changes to your business or relevant requirements may affect your obligations.

Assess current controls against each requirement.

Assess your current controls against each applicable requirement to see where your organisation is meeting its obligations and where improvements are needed. Review not only written policies, but also how processes work in practice and what evidence demonstrates that controls are operating consistently. Recording gaps, risks and supporting evidence makes it easier to prioritise remediation and prepare for an audit or assessment.

Prioritise gaps by risk and impact.

Prioritise compliance gaps by considering the likelihood of exploitation and the potential impact on your organisation, customers and critical services. Address high-risk issues first, such as weaknesses that could expose sensitive data or disrupt essential systems, while scheduling lower-impact improvements appropriately. A risk-based approach helps direct time and resources where they will make the greatest difference, rather than treating every gap as equally urgent.

Keep evidence organised and up to date.

Keep evidence organised and up to date so you can show how your cybersecurity controls work in practice. Maintain a clear, securely stored record of items such as policies, risk assessments, training logs, access reviews, incident reports and supplier checks. Assign owners and review dates, and update documents whenever systems, processes or requirements change. This makes assessments easier, helps staff find reliable information quickly and can reveal gaps before they become compliance issues.

Review compliance regularly as rules change.

Review your compliance arrangements regularly, as cybersecurity rules, industry standards and contractual requirements can change. Schedule periodic reviews and reassess your controls whenever your systems, suppliers or business activities change. This helps identify gaps early and ensures your policies and procedures remain relevant, rather than relying on a one-off assessment.