Windows Defender Firewall: What It Does and How to Use It

Windows Defender Firewall is a security feature built into Windows that helps protect a computer from unwanted network traffic. It monitors connections and applies rules to decide which traffic is allowed through. By limiting unauthorised access, it can help reduce the risk of attacks and unwanted communication with your device.

In newer versions of Windows, the feature is generally called Microsoft Defender Firewall. It is included with Windows and works alongside other security measures, such as Microsoft Defender Antivirus, but the firewall and antivirus have different jobs.

How the firewall works

A firewall checks network traffic against a set of rules. These rules can allow or block connections based on factors such as the application involved, the type of network, and whether the connection is incoming or outgoing.

  • Inbound traffic is data coming into your computer from another device or the internet. Blocking unexpected inbound connections helps prevent other devices from reaching services on your PC.
  • Outbound traffic is data leaving your computer. Windows Firewall also supports rules for controlling outbound connections, although its default configuration is generally designed to allow normal outgoing activity unless a rule says otherwise.

When an app needs to communicate across a network, Windows may ask whether to allow it. The choice can depend on the network profile in use, so it is worth checking that the app and network are recognised before granting access.

Network profiles: domain, private and public

Windows uses network profiles to apply different firewall settings in different situations:

  • Domain: Used when a device is connected to a network managed by an organisation, such as a workplace domain.
  • Private: Intended for trusted networks, such as a home network. Devices may be able to discover one another, depending on the settings and services enabled.
  • Public: Intended for untrusted networks, such as Wi-Fi in a café, hotel or airport. This profile applies stricter protections and is usually the safer choice for unfamiliar networks.

Windows may ask whether a newly detected network should be treated as public or private. Choose the profile that reflects how much you trust the network. A public network should not be marked private simply to make file sharing or device discovery easier.

Checking firewall status

To check the firewall in Windows 11, open Settings, select Privacy & security, then Windows Security. Choose Firewall & network protection to view the status of the available network profiles and open the related settings.

The same area can also be opened by searching for Windows Security from the Start menu. The wording and layout may vary slightly between Windows versions.

Allowing an app through the firewall

If a trusted app cannot connect, it may need permission to communicate through the firewall. Before changing anything, confirm that the app is legitimate and that the connection is genuinely required.

  1. Open Windows Security and select Firewall & network protection.
  2. Choose Allow an app through firewall.
  3. Select Change settings if prompted for administrator permission.
  4. Find the app and allow it on the appropriate network profile. If it is not listed, use the option to add another app only when you know which programme you are approving.

Allowing an app through the firewall creates an exception. Avoid granting access on every profile unless it is necessary. In particular, an app that needs access on a trusted home network may not need the same access on public Wi-Fi.

Creating or reviewing firewall rules

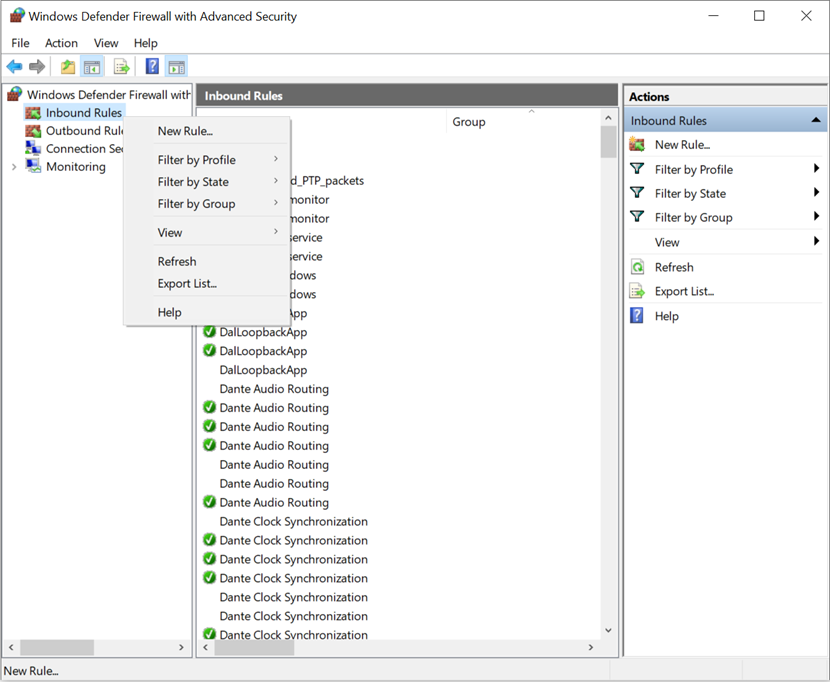
Windows includes Windows Defender Firewall with Advanced Security, which provides more detailed controls for inbound and outbound rules. It is available by searching for its name in the Start menu or through Windows administrative tools.

Advanced rules can be useful for managing specific applications, ports, protocols and network profiles. They can also be used by IT administrators to apply consistent policies across managed devices. However, changing rules without understanding their effect can disrupt apps or weaken security. If a computer is managed by an employer or school, check with the administrator before altering its firewall configuration.

Should you turn the firewall off?

In most cases, the firewall should remain switched on for every network profile. Turning it off removes an important layer of protection, particularly on public networks. If a connection problem appears to be caused by the firewall, it is usually safer to investigate the relevant app or rule than to disable the firewall altogether.

Do not run multiple firewalls that are not designed to work together. Some third-party security products manage the firewall themselves, and Windows may show a different status when another provider is active. Check the security software’s guidance before changing settings.

Good practice for staying protected

  • Keep Windows and your applications up to date.
  • Leave Microsoft Defender Firewall enabled unless a trusted administrator advises otherwise.
  • Use the public network profile for unfamiliar Wi-Fi networks.
  • Allow only trusted apps, and only on the profiles they need.
  • Review firewall alerts and settings rather than dismissing them automatically.
  • Use additional protections, such as strong passwords and multi-factor authentication, where available.

In summary

Windows Defender Firewall helps control network traffic to and from a Windows device. Its built-in protection is suitable for many home and business users when it is enabled and kept at its default settings. Understanding network profiles and app exceptions can help you resolve connection issues without opening more access than necessary.


8 Tips for Using Microsoft Defender Firewall Safely

  1. Keep Microsoft Defender Firewall turned on for all network profiles.
  2. Use private networks for trusted home or work connections.
  3. Treat public Wi‑Fi as a public network.
  4. Allow apps through the firewall only when necessary.
  5. Remove permissions for apps you no longer use.
  6. Avoid turning off the firewall to fix connection problems.
  7. Check firewall notifications before allowing access.
  8. Keep Windows updated to receive the latest security fixes.

Keep Microsoft Defender Firewall turned on for all network profiles.

Keep Microsoft Defender Firewall turned on for all network profiles to help protect your device from unauthorised network connections, wherever you’re connected. This is especially important on public Wi-Fi, such as in cafés, hotels or airports, where other users may be unfamiliar or untrusted. If an app or service has connection problems, check its firewall permissions rather than switching the firewall off.

Use private networks for trusted home or work connections.

Set a network to private only when it is one you trust, such as your home Wi-Fi or a secure workplace network. This profile can allow your computer to be discoverable by other devices and support features such as file and printer sharing. For unfamiliar connections, including public Wi-Fi in cafés or hotels, choose the public profile instead to keep your device less visible and apply stricter protection.

Treat public Wi‑Fi as a public network.

When connecting to public Wi-Fi in places such as cafés, hotels or airports, set the network profile to Public in Windows. This applies stricter sharing and discovery settings, helping limit how visible your device is to other people on the same network. Avoid switching to a Private profile just to make a connection work, and only allow apps through the firewall when you trust them and know they need network access.

Allow apps through the firewall only when necessary.

Allow apps through Windows Defender Firewall only when necessary, and only if you trust the app and understand why it needs network access. Each exception creates a route for communication with your device, so avoid granting access on every network profile by default. Choose only the profiles the app needs, and remove permissions you no longer use.

Remove permissions for apps you no longer use.

Review the apps allowed through Windows Defender Firewall from time to time and remove permissions for programmes you no longer use. An outdated or unnecessary exception may leave a route for network access that the app no longer needs. In Windows Security, open Firewall & network protection, select Allow an app through firewall, then review the list and remove any permissions that are no longer required. If your device is managed by work or school, check with your IT administrator before changing firewall settings.

Avoid turning off the firewall to fix connection problems.

Avoid turning off Windows Defender Firewall to fix connection problems, as this removes an important layer of protection and may leave your device exposed to unwanted network traffic. Instead, check whether the correct network profile is selected and review the firewall rules or app permissions for the programme experiencing difficulties. Only allow access for trusted apps, and seek help from your IT administrator if your device is managed by work or school.

Check firewall notifications before allowing access.

Before allowing an app through Windows Defender Firewall, read the notification carefully and check that you recognise both the app and why it needs network access. Pay attention to the network type: an app may be suitable for a trusted private network but not for public Wi-Fi. If the request is unexpected or you are unsure, deny access for now and verify the app with its developer or your IT administrator.

Keep Windows updated to receive the latest security fixes.

Keep Windows up to date so your device receives the latest security fixes and improvements. These updates can address vulnerabilities that attackers might exploit, helping Windows Defender Firewall work as part of a stronger overall security set-up. Enable automatic updates where possible, and restart your device when prompted to complete the installation.
The Importance of Windows Firewall in Securing Your System

When it comes to safeguarding your computer against online threats, one essential tool that should not be overlooked is the Windows Firewall. As a built-in feature of the Windows operating system, the firewall plays a crucial role in protecting your system from malicious attacks and unauthorised access.

Windows Firewall acts as a barrier between your computer and the vast network of potential threats lurking on the internet. It monitors incoming and outgoing network traffic, allowing only authorised data packets to pass through while blocking suspicious or harmful ones. By filtering traffic based on predefined rules and security settings, the firewall acts as a first line of defence against cyber threats.

One of the key benefits of using Windows Firewall is its ease of use and seamless integration with the Windows operating system. It requires minimal configuration and runs silently in the background, providing continuous protection without disrupting your workflow. Additionally, Windows Firewall receives regular updates from Microsoft to ensure that it can effectively combat new and emerging threats.

By enabling Windows Firewall, you can significantly reduce the risk of falling victim to malware infections, hacking attempts, and other cyber attacks. It helps secure your personal information, sensitive data, and system resources from being compromised by cybercriminals who are constantly probing for vulnerabilities.

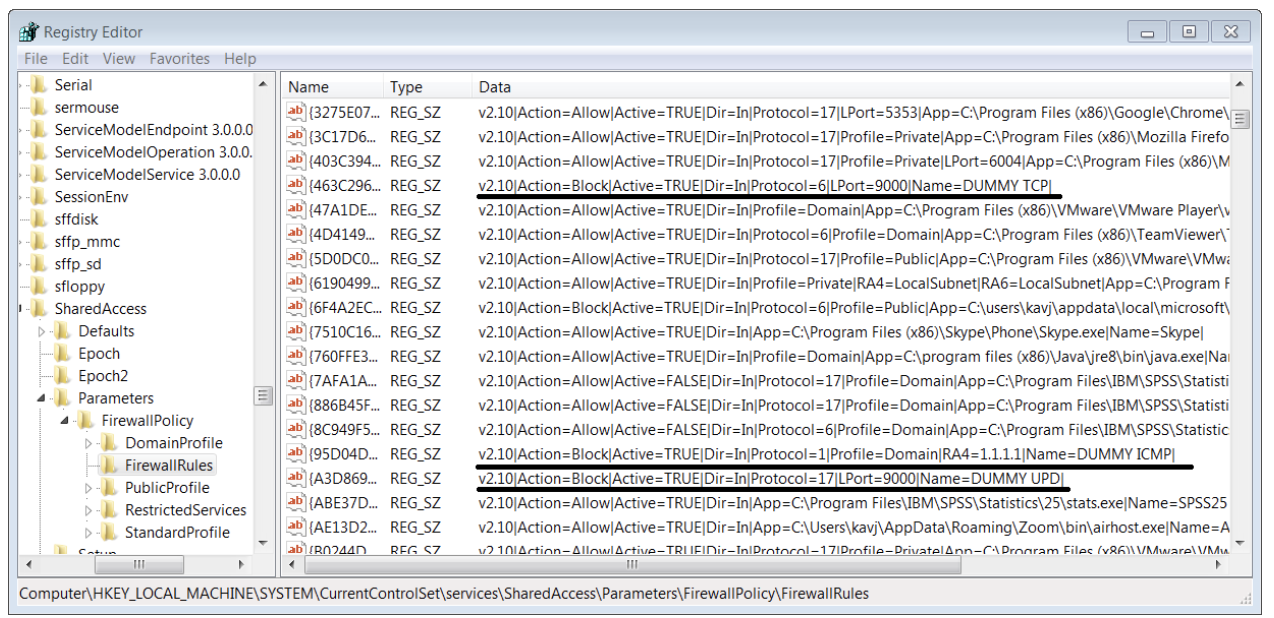
Furthermore, Windows Firewall allows you to customise settings based on your specific security needs. You can create rules to allow or block specific applications or services, configure exceptions for certain network connections, and monitor firewall activity through detailed logs. This level of flexibility empowers you to tailor the firewall protection to suit your individual requirements.

In today’s interconnected digital world where cybersecurity threats are ever-present, having a robust firewall like Windows Firewall is essential for maintaining a secure computing environment. By proactively defending against external threats and enforcing network security policies, you can enhance the overall resilience of your system and enjoy peace of mind knowing that your data is protected.

In conclusion, Windows Firewall serves as a fundamental component in securing your system against cyber threats. By leveraging its capabilities and features, you can fortify your defences against malicious actors seeking to exploit vulnerabilities in your network. Make sure to enable and configure Windows Firewall on your computer to bolster its security posture and safeguard your valuable digital assets.


6 Essential Tips for Enhancing Security with Windows Firewall

  1. Ensure Windows Firewall is turned on for network protection.
  2. Regularly update Windows Firewall to protect against new threats.
  3. Create specific inbound and outbound rules to control network traffic.
  4. Use advanced security settings in Windows Firewall for more granular control.
  5. Enable logging in Windows Firewall to monitor and analyse network activity.
  6. Consider using additional third-party firewall software for enhanced security.

Ensure Windows Firewall is turned on for network protection.

To enhance the security of your network, it is crucial to ensure that Windows Firewall is turned on. By activating Windows Firewall, you create a protective barrier that filters incoming and outgoing network traffic, safeguarding your system from potential threats and unauthorised access. This proactive measure helps to fortify your network defences and minimise the risk of cyber attacks, providing a vital layer of security for your digital assets. Remember to regularly review and update your firewall settings to adapt to evolving security challenges and maintain a robust defence against online threats.

Regularly update Windows Firewall to protect against new threats.

To enhance the effectiveness of Windows Firewall in safeguarding your system, it is crucial to regularly update the firewall to defend against new and evolving threats. By staying current with the latest security updates provided by Microsoft, you ensure that your firewall is equipped with the most up-to-date protections against emerging cyber threats. Updating Windows Firewall not only strengthens your system’s security posture but also helps to mitigate potential vulnerabilities that could be exploited by malicious actors. By prioritising regular updates for Windows Firewall, you proactively fortify your defences and maintain a robust shield against a constantly changing threat landscape.

Create specific inbound and outbound rules to control network traffic.

To enhance the effectiveness of Windows Firewall in securing your system, a valuable tip is to create specific inbound and outbound rules to control network traffic. By defining precise rules that dictate which connections are allowed or blocked, you can exert greater control over the flow of data to and from your computer. This targeted approach enables you to tailor the firewall’s protection to meet your unique security requirements, ensuring that only authorised traffic is permitted while unauthorised access attempts are promptly thwarted. By implementing customised rules for inbound and outbound traffic, you can strengthen the overall resilience of your system and minimise the risk of cyber threats infiltrating your network.

Use advanced security settings in Windows Firewall for more granular control.

To enhance the effectiveness of Windows Firewall in safeguarding your system, consider utilising advanced security settings to achieve more granular control over network traffic. By delving into the intricacies of these settings, you can customise firewall rules and configurations to align with your specific security requirements. This level of fine-tuning allows you to finely tune access permissions, create detailed exceptions, and monitor network activity with greater precision. By leveraging advanced security settings in Windows Firewall, you can bolster your defences against cyber threats and ensure that your system remains protected against potential vulnerabilities.

Enable logging in Windows Firewall to monitor and analyse network activity.

Enabling logging in Windows Firewall is a valuable tip to enhance your network security. By activating logging, you can track and analyse network activity, gaining insights into incoming and outgoing traffic. This feature allows you to monitor potential threats, identify suspicious behaviour, and troubleshoot connectivity issues effectively. With detailed logs provided by Windows Firewall, you can proactively manage your system’s security and make informed decisions to strengthen your defences against cyber threats.

Consider using additional third-party firewall software for enhanced security.

For enhanced security, it is advisable to consider supplementing the built-in Windows Firewall with additional third-party firewall software. While Windows Firewall provides fundamental protection, third-party firewall solutions offer advanced features and customisation options that can further strengthen your system’s defences. By utilising a comprehensive firewall solution from a reputable provider, you can benefit from enhanced threat detection capabilities, granular control over network traffic, and additional layers of security to safeguard your system against sophisticated cyber attacks. Implementing third-party firewall software alongside Windows Firewall can provide a robust security framework that significantly reduces the risk of breaches and enhances overall protection for your digital assets.

The Importance of Active Directory in Modern IT Environments

The Importance of Active Directory in Modern IT Environments

Active Directory is a crucial component in the realm of IT infrastructure for organisations worldwide. It serves as a centralised database that stores and manages information about network resources, making it easier to organise, manage, and secure a network.

One of the key advantages of Active Directory is its ability to provide a single sign-on experience for users within a network. This means that users only need one set of credentials to access various resources, simplifying the authentication process and enhancing security by reducing the risk of password fatigue or weak passwords.

Furthermore, Active Directory enables administrators to implement group policies that define user permissions and access rights. This granular control ensures that sensitive data remains secure and only accessible to authorised individuals, thereby reducing the risk of data breaches.

Another significant benefit of Active Directory is its support for scalability. As organisations grow and evolve, Active Directory can easily accommodate changes in user accounts, groups, and resources without compromising performance or security.

In addition to enhancing security and streamlining user management, Active Directory plays a vital role in facilitating collaboration and productivity within an organisation. By providing a unified directory service, it enables seamless communication and resource sharing among employees, fostering teamwork and efficiency.

In conclusion, Active Directory is an indispensable tool for modern IT environments. Its robust features not only enhance security and streamline user management but also promote collaboration and productivity within organisations. By leveraging the power of Active Directory, businesses can create a secure, efficient, and interconnected network environment that supports their growth and success.


Mastering Active Directory: A Comprehensive Guide to Configuration, Management, and Security

  1. What is Active Directory and how does it work?
  2. What are the benefits of using Active Directory in an organisation?
  3. How can I set up and configure Active Directory for my network?
  4. What are group policies in Active Directory, and how do they work?
  5. How do I manage user accounts and permissions in Active Directory?
  6. What security measures should I implement to protect my Active Directory environment?
  7. Can I integrate third-party applications with Active Directory, and if so, how?
  8. What are the common challenges faced when maintaining an Active Directory infrastructure?

What is Active Directory and how does it work?

Active Directory is a crucial component in modern IT infrastructure, serving as a centralised database that stores information about network resources such as computers, users, and groups. It works by providing a hierarchical structure that organises these resources into a logical framework, making it easier for administrators to manage and secure the network. Active Directory uses a domain-based model where each domain represents a security boundary within the network, allowing administrators to set permissions and access controls based on user roles and group memberships. Through its domain controllers, Active Directory authenticates and authorises users to access resources, ensuring secure and efficient communication within the network environment.

What are the benefits of using Active Directory in an organisation?

Implementing Active Directory in an organisation offers a multitude of benefits that enhance efficiency, security, and collaboration. One key advantage is the centralised management of user accounts and resources, simplifying administrative tasks and ensuring consistent access control. Active Directory’s support for group policies allows for granular control over user permissions, reducing the risk of data breaches and ensuring compliance with security standards. Additionally, the scalability of Active Directory enables seamless expansion as the organisation grows, maintaining performance and security. By providing a unified directory service, Active Directory promotes collaboration among employees, streamlines communication, and boosts overall productivity within the organisation.

How can I set up and configure Active Directory for my network?

Setting up and configuring Active Directory for your network is a fundamental step in establishing a secure and efficient IT environment. To begin, you need to install the Active Directory Domain Services role on a Windows Server. Once installed, you can use the Active Directory Domain Services Configuration Wizard to promote the server to a domain controller. During this process, you will need to specify the domain name, set a Directory Services Restore Mode password, and choose whether to install DNS on the same server. After promoting the server to a domain controller, you can start creating user accounts, groups, organisational units, and defining group policies to manage access and permissions within your network. Regular monitoring and maintenance of Active Directory are essential to ensure its optimal performance and security for your network infrastructure.

What are group policies in Active Directory, and how do they work?

Group policies in Active Directory are a powerful tool used to manage and enforce specific settings and configurations across a network of computers. Essentially, group policies define rules that dictate how users and computers interact with the network and what they can do. These policies can control various aspects such as security settings, desktop configurations, software installation, and more. When a user logs into a computer that is part of an Active Directory domain, the group policies assigned to that user or computer are applied, ensuring consistency and standardisation across the network. Group policies work by creating a hierarchical structure where policies at different levels can be inherited or overridden based on their priority, allowing administrators to customise settings based on organisational requirements.

How do I manage user accounts and permissions in Active Directory?

Managing user accounts and permissions in Active Directory is a fundamental task for IT administrators seeking to maintain a secure and organised network environment. To manage user accounts, administrators can create, modify, or delete user accounts through the Active Directory Users and Computers console. This tool allows for the assignment of specific permissions to users based on their roles within the organisation. By defining access rights and group memberships, administrators can control what resources users can interact with, ensuring data security and compliance with organisational policies. Regularly reviewing and updating user permissions is essential to maintaining a robust security posture and preventing unauthorised access to sensitive information within the Active Directory environment.

What security measures should I implement to protect my Active Directory environment?

When considering security measures to safeguard your Active Directory environment, it is crucial to implement a multi-layered approach that addresses various aspects of security. Firstly, enforcing strong password policies and implementing multi-factor authentication can significantly enhance the authentication process and prevent unauthorised access. Regularly updating and patching systems to address vulnerabilities is essential in mitigating potential security risks. Additionally, restricting user privileges based on the principle of least privilege can limit the impact of potential security breaches. Monitoring and auditing user activity within Active Directory can help detect suspicious behaviour and take proactive measures to prevent security incidents. Lastly, encrypting data both at rest and in transit adds an extra layer of protection to sensitive information stored within the Active Directory environment. By combining these security measures, organisations can bolster the resilience of their Active Directory infrastructure against cyber threats.

Can I integrate third-party applications with Active Directory, and if so, how?

Integrating third-party applications with Active Directory is a common requirement for many organisations seeking to streamline user access and authentication processes. Fortunately, Active Directory supports integration with a wide range of third-party applications through protocols such as LDAP (Lightweight Directory Access Protocol) and SAML (Security Assertion Markup Language). By configuring the third-party application to communicate with Active Directory using these standard protocols, businesses can enable seamless authentication and authorisation workflows, allowing users to access multiple applications with their existing Active Directory credentials. This integration not only enhances security by centralising user management but also simplifies user experience by providing a single sign-on solution across various platforms.

What are the common challenges faced when maintaining an Active Directory infrastructure?

Maintaining an Active Directory infrastructure poses several common challenges that organisations often encounter. One prevalent issue is ensuring the security of the Active Directory environment, as it holds sensitive information and serves as a gateway to various network resources. Managing user permissions effectively and preventing unauthorised access are constant concerns for administrators. Another challenge is maintaining the integrity of the directory data, including accurate user information, group memberships, and configuration settings. As organisations grow and evolve, keeping the Active Directory schema up-to-date and optimising performance to accommodate increasing workloads can also be daunting tasks. Addressing these challenges requires proactive monitoring, regular audits, effective delegation of administrative tasks, and a comprehensive understanding of best practices in Active Directory management.