How to Choose the Best Internet Security Provider

Choosing the best internet security provider is about more than picking the biggest name. The right option should protect the devices you use, suit the way you go online and offer support you can rely on. Features, prices and performance vary, so it is worth comparing what each provider includes before you subscribe.

What does an internet security provider do?

Internet security providers offer software and services designed to reduce online risks. Depending on the package, these may include protection against viruses, ransomware, phishing and harmful websites. Some providers also offer a firewall, parental controls, password management, identity monitoring or a virtual private network (VPN).

Security software can help spot and block threats, but it cannot prevent every risk. Keeping your devices and apps up to date, using unique passwords and being cautious with unexpected links remain important.

What to look for

  • Strong malware protection: Look for independent test results that assess how well the product detects and blocks threats.
  • Coverage for your devices: Check whether the subscription supports Windows, macOS, Android or iOS, and how many devices you can protect.
  • Useful features: Choose features that match your needs. A family may value parental controls, while someone who often uses public Wi-Fi may want a VPN.
  • Ease of use: Clear alerts and straightforward settings make it easier to manage your protection.
  • Performance: Security software should protect your devices without noticeably slowing them down.
  • Price and renewal terms: Compare the introductory price with the renewal cost. Check what is included and how cancellation works.
  • Customer support: Find out how to contact support and whether help is available when you need it.
  • Privacy practices: Read the provider’s privacy information to understand what data it collects and how it is used.

Providers worth comparing

Several established brands offer consumer security products. The best fit depends on your devices, budget and the features you actually need.

Bitdefender

Bitdefender offers security packages for individuals and families, with options that can include malware protection, web security and additional privacy tools. Compare the features in each plan, as the entry-level package may differ from higher tiers.

Norton

Norton provides a range of security subscriptions, some of which bundle features such as a VPN, password management or identity-related services. Check which features are available in the UK and whether they are included in the plan you are considering.

ESET

ESET is another provider to consider, particularly if you want a security product with configurable settings. Compare its device support and package features with your requirements before choosing.

Trend Micro

Trend Micro offers protection focused on areas such as malware and online threats. As with any provider, check independent test results and make sure the plan covers the operating systems and devices you use.

Malwarebytes

Malwarebytes offers products for detecting and blocking malicious software and other online threats. Review the current package details to see which protections are included and whether they meet your needs as a primary security solution.

These examples are not a definitive ranking. Products change over time, and independent testing can vary by test date, device and threat type. Check recent results from reputable testing organisations before making a decision.

Free security software or a paid subscription?

Free security tools may provide a useful baseline, while paid plans often add features such as protection for multiple devices, parental controls or a VPN. However, a longer feature list does not automatically make a product better. Consider whether you will use the extras and whether they are already available through your operating system, browser or another service.

Be cautious of unsolicited pop-ups claiming that your device is infected or urging you to call a support number. Use the provider’s official website or app to check your subscription and contact support.

How to make the final choice

  1. List the devices and operating systems you need to protect.
  2. Decide which features matter to you, such as parental controls or a VPN.
  3. Compare recent independent test results and product reviews.
  4. Check the full price, renewal terms and cancellation process.
  5. Download software only from the provider’s official website or an authorised app store.

So, which internet security provider is best?

There is no single provider that is best for everyone. A good choice is one that offers dependable protection for your devices, includes features you will use, is easy to manage and has clear pricing and privacy terms. Compare current plans and recent independent test results rather than choosing on brand name alone.


Top 5 Tips for Choosing the Best Internet Security Provider

  1. Choose a provider with strong, independently tested protection.
  2. Check that updates and customer support are reliable.
  3. Look for clear privacy policies and minimal data collection.
  4. Compare prices, renewal costs and device limits.
  5. Pick a plan with features suited to your devices and needs.

Choose a provider with strong, independently tested protection.

Choose an internet security provider with strong protection that has been independently tested by reputable organisations. These tests assess how effectively a product detects and blocks threats such as malware and phishing, giving you a clearer basis for comparison than marketing claims alone. Check recent results, as performance can change over time, and make sure the product supports your devices and operating systems.

Check that updates and customer support are reliable.

When choosing an internet security provider, check that its software receives regular, timely updates to respond to new threats and keep protection effective. Reliable customer support is equally important: look for clear contact options, helpful guidance and support hours that suit your needs. Recent user reviews can offer useful insight into how quickly the provider resolves problems.

Look for clear privacy policies and minimal data collection.

When choosing an internet security provider, look for a clear privacy policy that explains what information is collected, why it is needed and how long it is kept. A provider that collects only the data required to deliver its service can help limit unnecessary exposure of your personal information. Check whether data is shared with third parties, and look for straightforward options to manage or delete your information.

Compare prices, renewal costs and device limits.

Before choosing an internet security provider, compare more than the introductory price. Check the renewal cost, as a discounted first year may be followed by a higher subscription fee, and make sure you understand how to cancel or change your plan. Also review the device limit: a cheaper package may cover only one or two devices, while a household may need protection for several computers, phones and tablets. Comparing the total cost against the number of devices covered can help you find a plan that offers good value.

Pick a plan with features suited to your devices and needs.

Choose an internet security plan that matches the devices you use and the risks you want to manage. Check that it supports your operating systems and covers enough devices, then consider which extras are genuinely useful—such as parental controls for a family, a VPN for using public Wi-Fi or identity monitoring for added reassurance. There’s little benefit in paying for features you won’t use, so compare plans carefully and check what’s included in the price.
The Importance of Checkpoint Cybersecurity in Safeguarding Your Digital Assets

In today’s interconnected world, where businesses rely heavily on digital infrastructure to operate efficiently, cybersecurity has become a paramount concern. With the increasing frequency and sophistication of cyber threats, organisations must implement robust security measures to protect their sensitive data and systems. One such critical component of cybersecurity is Checkpoint Security.

What is Checkpoint Cybersecurity?

Checkpoint Security is a comprehensive approach to safeguarding networks, data, and endpoints from cyber threats. It involves the deployment of advanced security solutions that monitor, detect, and prevent malicious activities in real-time. Checkpoint Security solutions are designed to provide multi-layered defence mechanisms that cover various entry points and attack vectors within an organisation’s IT infrastructure.

The Key Components of Checkpoint Cybersecurity

Checkpoint Cybersecurity encompasses a range of technologies and practices aimed at fortifying an organisation’s security posture. Some key components include:

  • Firewalls: Checkpoint firewalls act as the first line of defence by monitoring incoming and outgoing network traffic and blocking potential threats.
  • Intrusion Prevention Systems (IPS): IPS solutions identify and block suspicious network traffic that may indicate an ongoing cyber attack.
  • Endpoint Security: Protecting individual devices such as laptops, desktops, and mobile devices from malware and other cyber threats.
  • Threat Intelligence: Utilising real-time threat intelligence feeds to stay informed about emerging cyber threats and vulnerabilities.

The Benefits of Implementing Checkpoint Cybersecurity

By incorporating Checkpoint Security measures into their cybersecurity strategy, organisations can enjoy several benefits:

  • Enhanced Protection: Checkpoint Security provides a robust defence against a wide range of cyber threats, reducing the risk of data breaches and system compromises.
  • Improved Compliance: Many regulatory standards require organisations to have adequate cybersecurity measures in place. Implementing Checkpoint Security can help meet compliance requirements.
  • Faster Incident Response: With real-time monitoring capabilities, Checkpoint Security enables quick detection and response to potential security incidents before they escalate.
  • Cost Savings: Investing in proactive cybersecurity measures like Checkpoint Security can ultimately save organisations money by preventing costly data breaches or downtime.

In Conclusion

In conclusion, Checkpoint Cybersecurity plays a vital role in protecting organisations from the ever-evolving landscape of cyber threats. By implementing robust security measures across networks, endpoints, and data centres, businesses can mitigate risks and safeguard their digital assets effectively. As cyber attacks continue to grow in complexity, investing in Checkpoint Security is essential for maintaining a secure and resilient IT environment.

Contact us today to learn more about how our Checkpoint Cybersecurity solutions can help fortify your organisation’s defences against cyber threats.


Essential Cybersecurity Tips: Safeguarding Your Systems with Checkpoint Strategies

  1. Regularly update your security software and systems.
  2. Use strong, unique passwords for all your accounts.
  3. Enable two-factor authentication whenever possible.
  4. Be cautious of suspicious emails and links, especially from unknown sources.
  5. Backup your important data regularly to prevent data loss in case of an attack.
  6. Educate yourself and your team about cybersecurity best practices.
  7. Limit access to sensitive information only to those who need it.
  8. Monitor network activity for any unusual behaviour that may indicate a breach.

Regularly update your security software and systems.

Regularly updating your security software and systems is a crucial tip in maintaining a strong defence against cyber threats. Software updates often contain patches for known vulnerabilities and security weaknesses, ensuring that your systems are equipped to withstand the latest attack techniques. By staying current with updates, you can enhance the overall resilience of your cybersecurity infrastructure and reduce the risk of exploitation by malicious actors. Remember, proactive maintenance through regular updates is key to keeping your digital assets secure in an ever-evolving threat landscape.

Use strong, unique passwords for all your accounts.

It is crucial to use strong, unique passwords for all your accounts as part of effective checkpoint cybersecurity practices. Strong passwords that are complex and not easily guessable can significantly enhance the security of your accounts and data. By using unique passwords for each account, you reduce the risk of a security breach affecting multiple accounts if one password is compromised. Implementing this simple yet essential tip can serve as a fundamental barrier against cyber threats and help safeguard your digital assets from unauthorised access.

Enable two-factor authentication whenever possible.

Enabling two-factor authentication whenever possible is a crucial tip in bolstering your checkpoint cybersecurity measures. By requiring a second form of verification in addition to passwords, such as a unique code sent to your mobile device, two-factor authentication adds an extra layer of security that significantly reduces the risk of unauthorised access to your accounts or systems. This simple yet effective security measure can thwart many common cyber threats, including phishing attacks and password breaches, enhancing the overall protection of your digital assets and ensuring a more secure online experience.

In the realm of Checkpoint cybersecurity, it is crucial to exercise caution when encountering suspicious emails and links, particularly those originating from unfamiliar sources. Cybercriminals often use phishing emails and malicious links as a means to infiltrate networks and compromise sensitive data. By remaining vigilant and refraining from clicking on dubious links or attachments, individuals can significantly reduce the risk of falling victim to cyber attacks. Prioritising cybersecurity awareness and adopting a cautious approach to email communications are fundamental steps in safeguarding against potential threats in the digital landscape.

Backup your important data regularly to prevent data loss in case of an attack.

Backing up your critical data regularly is a fundamental tip in Checkpoint Cybersecurity to mitigate the risk of data loss in the event of a cyber attack. By maintaining up-to-date backups of your important information, you can ensure that even if your systems are compromised, you have a secure copy of your data that can be restored quickly and efficiently. This proactive measure not only safeguards your valuable assets but also provides peace of mind knowing that your business can recover swiftly from any potential security incident.

Educate yourself and your team about cybersecurity best practices.

To enhance your organisation’s cybersecurity posture, it is crucial to educate yourself and your team about cybersecurity best practices. By staying informed about the latest cyber threats, security trends, and recommended protocols, you can empower your team to recognise potential risks and take proactive measures to mitigate them effectively. Regular training sessions and awareness programmes can help instil a culture of security consciousness within your organisation, making everyone a frontline defender against cyber attacks. Remember, knowledge is power when it comes to safeguarding your digital assets from malicious actors.

Limit access to sensitive information only to those who need it.

In the realm of Checkpoint cybersecurity, a fundamental tip to enhance data protection is to restrict access to sensitive information solely to individuals who require it for their roles. By implementing strict access controls and permissions, organisations can minimise the risk of unauthorised access and inadvertent data leaks. This proactive measure not only bolsters security but also ensures that critical data remains confidential and safeguarded from potential cyber threats. Limiting access to sensitive information to authorised personnel is a cornerstone of an effective cybersecurity strategy that prioritises data privacy and integrity.

Monitor network activity for any unusual behaviour that may indicate a breach.

Monitoring network activity for any unusual behaviour is a crucial tip in Checkpoint cybersecurity. By actively observing and analysing network traffic, organisations can detect potential security breaches at an early stage. Unusual patterns such as unexpected data transfers, unauthorized access attempts, or unusual spikes in network traffic could indicate malicious activity. Promptly identifying and responding to these anomalies can help prevent data breaches and mitigate the impact of cyber attacks, ensuring the integrity and security of the organisation’s digital assets.

The Importance of Windows Firewall in Securing Your System

When it comes to safeguarding your computer against online threats, one essential tool that should not be overlooked is the Windows Firewall. As a built-in feature of the Windows operating system, the firewall plays a crucial role in protecting your system from malicious attacks and unauthorised access.

Windows Firewall acts as a barrier between your computer and the vast network of potential threats lurking on the internet. It monitors incoming and outgoing network traffic, allowing only authorised data packets to pass through while blocking suspicious or harmful ones. By filtering traffic based on predefined rules and security settings, the firewall acts as a first line of defence against cyber threats.

One of the key benefits of using Windows Firewall is its ease of use and seamless integration with the Windows operating system. It requires minimal configuration and runs silently in the background, providing continuous protection without disrupting your workflow. Additionally, Windows Firewall receives regular updates from Microsoft to ensure that it can effectively combat new and emerging threats.

By enabling Windows Firewall, you can significantly reduce the risk of falling victim to malware infections, hacking attempts, and other cyber attacks. It helps secure your personal information, sensitive data, and system resources from being compromised by cybercriminals who are constantly probing for vulnerabilities.

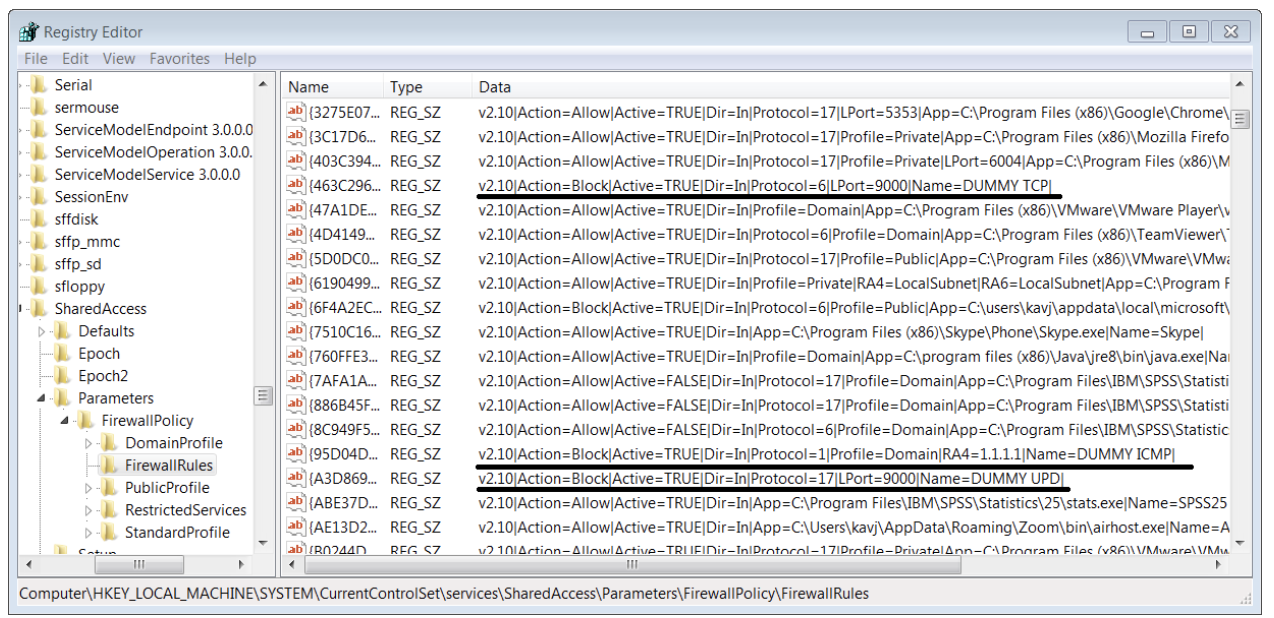
Furthermore, Windows Firewall allows you to customise settings based on your specific security needs. You can create rules to allow or block specific applications or services, configure exceptions for certain network connections, and monitor firewall activity through detailed logs. This level of flexibility empowers you to tailor the firewall protection to suit your individual requirements.

In today’s interconnected digital world where cybersecurity threats are ever-present, having a robust firewall like Windows Firewall is essential for maintaining a secure computing environment. By proactively defending against external threats and enforcing network security policies, you can enhance the overall resilience of your system and enjoy peace of mind knowing that your data is protected.

In conclusion, Windows Firewall serves as a fundamental component in securing your system against cyber threats. By leveraging its capabilities and features, you can fortify your defences against malicious actors seeking to exploit vulnerabilities in your network. Make sure to enable and configure Windows Firewall on your computer to bolster its security posture and safeguard your valuable digital assets.


6 Essential Tips for Enhancing Security with Windows Firewall

  1. Ensure Windows Firewall is turned on for network protection.
  2. Regularly update Windows Firewall to protect against new threats.
  3. Create specific inbound and outbound rules to control network traffic.
  4. Use advanced security settings in Windows Firewall for more granular control.
  5. Enable logging in Windows Firewall to monitor and analyse network activity.
  6. Consider using additional third-party firewall software for enhanced security.

Ensure Windows Firewall is turned on for network protection.

To enhance the security of your network, it is crucial to ensure that Windows Firewall is turned on. By activating Windows Firewall, you create a protective barrier that filters incoming and outgoing network traffic, safeguarding your system from potential threats and unauthorised access. This proactive measure helps to fortify your network defences and minimise the risk of cyber attacks, providing a vital layer of security for your digital assets. Remember to regularly review and update your firewall settings to adapt to evolving security challenges and maintain a robust defence against online threats.

Regularly update Windows Firewall to protect against new threats.

To enhance the effectiveness of Windows Firewall in safeguarding your system, it is crucial to regularly update the firewall to defend against new and evolving threats. By staying current with the latest security updates provided by Microsoft, you ensure that your firewall is equipped with the most up-to-date protections against emerging cyber threats. Updating Windows Firewall not only strengthens your system’s security posture but also helps to mitigate potential vulnerabilities that could be exploited by malicious actors. By prioritising regular updates for Windows Firewall, you proactively fortify your defences and maintain a robust shield against a constantly changing threat landscape.

Create specific inbound and outbound rules to control network traffic.

To enhance the effectiveness of Windows Firewall in securing your system, a valuable tip is to create specific inbound and outbound rules to control network traffic. By defining precise rules that dictate which connections are allowed or blocked, you can exert greater control over the flow of data to and from your computer. This targeted approach enables you to tailor the firewall’s protection to meet your unique security requirements, ensuring that only authorised traffic is permitted while unauthorised access attempts are promptly thwarted. By implementing customised rules for inbound and outbound traffic, you can strengthen the overall resilience of your system and minimise the risk of cyber threats infiltrating your network.

Use advanced security settings in Windows Firewall for more granular control.

To enhance the effectiveness of Windows Firewall in safeguarding your system, consider utilising advanced security settings to achieve more granular control over network traffic. By delving into the intricacies of these settings, you can customise firewall rules and configurations to align with your specific security requirements. This level of fine-tuning allows you to finely tune access permissions, create detailed exceptions, and monitor network activity with greater precision. By leveraging advanced security settings in Windows Firewall, you can bolster your defences against cyber threats and ensure that your system remains protected against potential vulnerabilities.

Enable logging in Windows Firewall to monitor and analyse network activity.

Enabling logging in Windows Firewall is a valuable tip to enhance your network security. By activating logging, you can track and analyse network activity, gaining insights into incoming and outgoing traffic. This feature allows you to monitor potential threats, identify suspicious behaviour, and troubleshoot connectivity issues effectively. With detailed logs provided by Windows Firewall, you can proactively manage your system’s security and make informed decisions to strengthen your defences against cyber threats.

Consider using additional third-party firewall software for enhanced security.

For enhanced security, it is advisable to consider supplementing the built-in Windows Firewall with additional third-party firewall software. While Windows Firewall provides fundamental protection, third-party firewall solutions offer advanced features and customisation options that can further strengthen your system’s defences. By utilising a comprehensive firewall solution from a reputable provider, you can benefit from enhanced threat detection capabilities, granular control over network traffic, and additional layers of security to safeguard your system against sophisticated cyber attacks. Implementing third-party firewall software alongside Windows Firewall can provide a robust security framework that significantly reduces the risk of breaches and enhances overall protection for your digital assets.

The Power of pfSense: Enhancing Network Security and Performance

pfSense is an open-source firewall and routing platform that offers a wealth of features to enhance network security and performance. Developed based on FreeBSD, pfSense provides a robust, reliable, and cost-effective solution for businesses and individuals looking to fortify their network infrastructure.

Key Features of pfSense

One of the standout features of pfSense is its versatility. Whether you need a simple firewall or a comprehensive security solution, pfSense can be tailored to meet your specific requirements. Some key features include:

  • Firewall Protection: pfSense offers stateful packet filtering to protect your network from unauthorised access and malicious threats.
  • VPN Capabilities: With support for various VPN protocols, including OpenVPN and IPsec, pfSense enables secure remote access and site-to-site connectivity.
  • Quality of Service (QoS): Ensure optimal performance for critical applications by prioritising network traffic with QoS settings.
  • Intrusion Detection and Prevention: Detect and block suspicious activities with built-in IDS/IPS functionality.
  • Multi-WAN Support: Balance traffic across multiple internet connections for improved reliability and bandwidth management.

The Benefits of Using pfSense

Businesses and individuals can reap numerous benefits from implementing pfSense in their network infrastructure:

  • Enhanced Security: With advanced firewall capabilities and intrusion detection features, pfSense helps safeguard sensitive data from cyber threats.
  • Better Performance: Optimise network performance with QoS settings that prioritise important traffic, ensuring smooth operation of critical applications.
  • Cost-Effectiveness: As an open-source solution, pfSense eliminates the need for expensive proprietary hardware or software licenses, making it a budget-friendly choice for organisations of all sizes.
  • User-Friendly Interface: The intuitive web-based interface makes it easy to configure and manage firewall rules, VPN connections, and other settings without the need for extensive technical expertise.

In Conclusion

pfSense stands out as a powerful tool for enhancing network security and performance. Whether you are looking to strengthen your firewall protection, establish secure VPN connections, or optimise bandwidth usage, pfSense offers a comprehensive solution that can be customised to suit your specific needs. By leveraging the capabilities of pfSense, businesses and individuals can create a robust network infrastructure that is both secure and efficient.


Optimising Network Security and Performance: 8 Essential Tips for pfSense Users

  1. Regularly update your pfSense installation to ensure you have the latest security patches and features.
  2. Utilize aliases in pfSense to simplify firewall rule management and make configurations more efficient.
  3. Implement VPNs on pfSense for secure remote access and encrypted communication over untrusted networks.
  4. Take advantage of package management in pfSense to extend its functionality with additional features and services.
  5. Use VLANs in pfSense to segregate network traffic, improve security, and optimize network performance.
  6. Monitor system logs in pfSense to troubleshoot issues, identify security threats, and ensure smooth operation of your firewall.
  7. Set up multi-WAN load balancing in pfSense for increased reliability, bandwidth optimization, and fault tolerance.
  8. Configure port forwarding rules in pfSense to allow external access to internal services while maintaining network security.

Regularly update your pfSense installation to ensure you have the latest security patches and features.

It is crucial to regularly update your pfSense installation to stay ahead of potential security vulnerabilities and benefit from the latest features. By keeping your pfSense system up to date, you ensure that it is equipped with the most recent security patches, bug fixes, and enhancements released by the developers. This proactive approach not only helps in fortifying your network against emerging threats but also ensures that your pfSense firewall operates at its optimal performance level. Remember, staying current with updates is a fundamental step in maintaining a secure and reliable network infrastructure with pfSense.

Utilize aliases in pfSense to simplify firewall rule management and make configurations more efficient.

By utilising aliases in pfSense, users can streamline firewall rule management and enhance the efficiency of configurations. Aliases allow for the grouping of multiple IP addresses, networks, or ports under a single name, simplifying the creation and maintenance of firewall rules. This feature not only reduces the complexity of rule sets but also makes it easier to update configurations as needed. By leveraging aliases in pfSense, administrators can save time and effort while ensuring that their firewall rules remain organised and easy to manage.

Implement VPNs on pfSense for secure remote access and encrypted communication over untrusted networks.

By implementing VPNs on pfSense, users can ensure secure remote access and encrypted communication over untrusted networks. This powerful feature enables individuals and businesses to establish a secure connection to their network from remote locations, safeguarding sensitive data and communications from potential threats. With pfSense’s robust VPN capabilities, such as support for various protocols like OpenVPN and IPsec, users can enjoy peace of mind knowing that their information is protected as it travels across untrusted networks. This proactive approach to network security on pfSense enhances privacy, confidentiality, and overall data protection for users accessing their network remotely.

Take advantage of package management in pfSense to extend its functionality with additional features and services.

By utilising package management in pfSense, users can significantly enhance the capabilities of their firewall and routing platform. By installing additional packages, such as IDS/IPS systems, caching servers, or traffic monitoring tools, users can extend the functionality of pfSense to better suit their specific needs. This flexibility allows for customisation and scalability, empowering users to tailor their network security and performance to meet evolving requirements effectively.

Use VLANs in pfSense to segregate network traffic, improve security, and optimize network performance.

Utilising VLANs in pfSense is a strategic approach to segregating network traffic, enhancing security measures, and optimising network performance. By creating distinct virtual LANs within the network infrastructure, administrators can effectively isolate different types of traffic, such as guest Wi-Fi, IoT devices, and critical business applications. This segregation not only bolsters security by preventing unauthorised access to sensitive data but also allows for more efficient bandwidth management and prioritisation of network resources. Implementing VLANs in pfSense empowers organisations to customise their network architecture to meet specific needs while maintaining a robust level of control and protection over their digital assets.

Monitor system logs in pfSense to troubleshoot issues, identify security threats, and ensure smooth operation of your firewall.

Monitoring system logs in pfSense is a crucial tip for maintaining the security and efficiency of your firewall. By regularly checking system logs, you can troubleshoot issues promptly, identify potential security threats, and ensure the smooth operation of your network. System logs provide valuable insights into the activities and events occurring within your pfSense environment, allowing you to proactively address any anomalies or suspicious behaviour. By staying vigilant and proactive in monitoring system logs, you can enhance the overall effectiveness of your firewall and mitigate potential risks effectively.

Set up multi-WAN load balancing in pfSense for increased reliability, bandwidth optimization, and fault tolerance.

Setting up multi-WAN load balancing in pfSense is a strategic tip that can significantly enhance network performance and reliability. By configuring this feature, businesses can distribute traffic across multiple internet connections, thereby optimising bandwidth utilisation and ensuring uninterrupted connectivity. This setup not only improves overall network efficiency but also provides fault tolerance, as any issues with one connection can be seamlessly mitigated by diverting traffic to alternative links. In essence, implementing multi-WAN load balancing in pfSense is a proactive approach towards achieving increased reliability and maximising the potential of network resources.

Configure port forwarding rules in pfSense to allow external access to internal services while maintaining network security.

Configuring port forwarding rules in pfSense is a crucial step to enable external access to internal services without compromising network security. By setting up specific rules that redirect incoming traffic from designated ports to internal servers or devices, organisations can ensure that external users can access necessary services while maintaining a secure perimeter. This approach allows for the seamless operation of applications such as web servers, VPNs, or remote desktop services, all while controlling and monitoring the flow of traffic to prevent unauthorised access and potential security breaches. With careful configuration of port forwarding rules in pfSense, businesses can strike a balance between accessibility and security, enhancing their network infrastructure’s functionality and protection.

Secure Your Online Presence with Bitdefender VPN: Protecting Your Privacy and Security

The Benefits of Using Bitdefender VPN for Enhanced Online Security

In today’s digital age, ensuring your online privacy and security is more important than ever. With cyber threats on the rise, it’s crucial to take proactive measures to safeguard your sensitive information and maintain anonymity while browsing the internet. One effective tool that can help you achieve this is Bitdefender VPN.

Bitdefender VPN is a virtual private network service offered by Bitdefender, a leading cybersecurity company known for its advanced antivirus solutions. By using Bitdefender VPN, you can encrypt your internet connection and route your online traffic through secure servers, providing you with several key benefits:

Enhanced Privacy

Bitdefender VPN creates a secure tunnel for your data transmission, preventing third parties such as hackers, ISPs, or government agencies from monitoring your online activities. This ensures that your personal information remains confidential and protected from prying eyes.

Improved Security

With encryption protocols in place, Bitdefender VPN adds an extra layer of security to your internet connection. This helps prevent cybercriminals from intercepting your data or launching attacks on your device while connected to public Wi-Fi networks or other unsecured connections.

Bypassing Geo-Restrictions

Bitdefender VPN allows you to mask your IP address and appear as if you are browsing from a different location. This feature enables you to access geo-restricted content or websites that may be blocked in your region, giving you greater freedom and flexibility online.

Anonymous Browsing

By using Bitdefender VPN, you can browse the web anonymously without revealing your real IP address. This helps protect your identity and online footprint, making it harder for advertisers or malicious entities to track your online behaviour and target you with unwanted ads or phishing attempts.

User-Friendly Interface

Bitdefender VPN offers an intuitive interface that makes it easy to connect to servers and customise settings according to your preferences. Whether you’re a novice user or a tech-savvy individual, Bitdefender VPN provides a seamless experience with minimal configuration required.

In conclusion, Bitdefender VPN is a valuable tool for anyone looking to enhance their online security and privacy. By encrypting your internet connection, protecting your data from cyber threats, and enabling anonymous browsing, Bitdefender VPN empowers you to navigate the digital world with confidence and peace of mind.


Understanding Bitdefender VPN: Key Questions Answered

  1. How do I use Bitdefender VPN on Android?
  2. What does Bitdefender VPN do on Iphone?
  3. Is Bitdefender VPN free?
  4. Can Bitdefender VPN be trusted?
  5. Should I enable Bitdefender VPN?
  6. Is Bitdefender a good VPN?
  7. Is Bitdefender a Russian company?

How do I use Bitdefender VPN on Android?

To use Bitdefender VPN on your Android device, follow these simple steps. First, download and install the Bitdefender VPN app from the Google Play Store. Once installed, open the app and log in using your Bitdefender Central account credentials. Next, select the desired server location from the list of available options or let the app choose the best server for you automatically. Finally, toggle the VPN switch to connect to the selected server and enjoy secure and private browsing on your Android device. With Bitdefender VPN, you can protect your online activities and data while maintaining anonymity wherever you go.

What does Bitdefender VPN do on Iphone?

Bitdefender VPN on iPhone provides users with a secure and private internet connection while using their mobile devices. By encrypting data traffic and routing it through secure servers, Bitdefender VPN helps protect users’ online activities from potential threats such as hackers or data snoopers. Additionally, Bitdefender VPN for iPhone allows users to bypass geo-restrictions, access region-locked content, and browse the web anonymously by masking their IP addresses. With an easy-to-use interface and strong encryption protocols, Bitdefender VPN on iPhone offers peace of mind to users seeking enhanced online security and privacy on their iOS devices.

Is Bitdefender VPN free?

One of the frequently asked questions about Bitdefender VPN is whether it is free to use. Bitdefender VPN does offer a free version with limitations on data usage and server locations. However, for users looking for unlimited access to servers worldwide and enhanced features such as faster connection speeds and priority support, Bitdefender also offers premium subscription plans at competitive prices. Whether you opt for the free version or choose to upgrade to a paid plan, Bitdefender VPN remains a reliable tool for enhancing your online security and privacy.

Can Bitdefender VPN be trusted?

When it comes to the trustworthiness of Bitdefender VPN, users can have confidence in its reliability and security features. Bitdefender is a well-established cybersecurity company with a strong reputation for providing top-notch protection against online threats. Their VPN service uses advanced encryption protocols to safeguard user data and ensure privacy while browsing the internet. With a commitment to transparency and user privacy, Bitdefender VPN has been independently audited and certified, giving users peace of mind that their online activities are protected by a trusted and reputable provider.

Should I enable Bitdefender VPN?

When considering whether to enable Bitdefender VPN, it’s important to weigh the benefits it offers in terms of online security and privacy. By activating Bitdefender VPN, you can encrypt your internet connection, enhance your privacy by masking your IP address, and protect your data from potential cyber threats. This added layer of security is particularly valuable when using public Wi-Fi networks or accessing geo-restricted content. Ultimately, enabling Bitdefender VPN can provide peace of mind and a safer online browsing experience, making it a worthwhile investment for those seeking to safeguard their digital presence.

Is Bitdefender a good VPN?

When evaluating the quality of Bitdefender VPN, it is important to consider its robust security features, user-friendly interface, and reputation as a trusted cybersecurity provider. Bitdefender VPN offers strong encryption protocols to safeguard your online activities and data privacy, making it a reliable choice for users concerned about cyber threats. Additionally, its intuitive interface makes it easy to use for individuals of all technical levels. With Bitdefender’s established track record in the cybersecurity industry, many users find peace of mind knowing they are using a VPN service from a reputable and experienced company like Bitdefender.

Is Bitdefender a Russian company?

Bitdefender is not a Russian company. It is a cybersecurity company headquartered in Bucharest, Romania. Founded in 2001, Bitdefender has established itself as a global leader in providing advanced security solutions to protect individuals and businesses against cyber threats. With a strong focus on innovation and customer satisfaction, Bitdefender has built a solid reputation for delivering high-quality products and services that prioritise online privacy and security.

The Importance of Cyber Security Services

The Importance of Cyber Security Services

In today’s digital age, where businesses rely heavily on technology to operate efficiently, the need for robust cyber security services has never been greater. Cyber threats continue to evolve and pose significant risks to organisations of all sizes. Investing in professional cyber security services is essential to safeguard sensitive data, protect against malicious attacks, and ensure business continuity.

One of the primary benefits of cyber security services is the proactive approach they offer in identifying and mitigating potential threats. Experienced professionals utilise advanced tools and techniques to monitor networks, detect vulnerabilities, and respond swiftly to incidents. By staying ahead of cyber criminals, businesses can prevent costly data breaches and minimise downtime.

Furthermore, cyber security services help organisations comply with regulatory requirements and industry standards. Many sectors have strict guidelines regarding data protection and privacy, such as GDPR in Europe or HIPAA in healthcare. By enlisting the expertise of cyber security professionals, businesses can ensure they meet these obligations and avoid hefty fines for non-compliance.

Another crucial aspect of cyber security services is education and training. Human error remains one of the leading causes of security breaches, often due to lack of awareness or understanding of best practices. Cyber security providers offer training programmes to educate employees on how to recognise phishing attempts, create secure passwords, and follow protocols to safeguard company information.

Ultimately, investing in cyber security services is an investment in the future resilience and reputation of your business. By partnering with experts who specialise in protecting digital assets, you can focus on growing your organisation without constantly worrying about cyber threats lurking around the corner.


Essential Cyber Security: Addressing Key Questions for Business Protection

  1. What is cyber security and why is it important?
  2. How can a cyber security service protect my business?
  3. What are the common types of cyber threats I should be aware of?
  4. How do I choose the right cyber security service provider?
  5. What measures can be taken to prevent data breaches?
  6. How often should my business conduct a security audit?
  7. What steps are involved in responding to a cyber attack?
  8. Can small businesses benefit from professional cyber security services?
  9. How does employee training contribute to overall cyber security?

What is cyber security and why is it important?

Cyber security is the practice of protecting digital systems, networks, and data from malicious attacks or unauthorised access. It encompasses a range of strategies, technologies, and processes designed to safeguard sensitive information and ensure the integrity of digital assets. In today’s interconnected world, where cyber threats are constantly evolving, cyber security plays a crucial role in maintaining the confidentiality, availability, and integrity of data. Without adequate cyber security measures in place, organisations are vulnerable to data breaches, financial losses, reputational damage, and legal consequences. By prioritising cyber security, businesses can mitigate risks, protect their valuable assets, and maintain trust with customers and stakeholders in an increasingly digitised environment.

How can a cyber security service protect my business?

Cyber security services play a vital role in safeguarding businesses against a myriad of digital threats. By employing advanced technologies and expert knowledge, these services can protect your business in several ways. Firstly, they conduct thorough assessments of your IT infrastructure to identify vulnerabilities and implement robust security measures to prevent cyber attacks. Additionally, cyber security services offer real-time monitoring of network activities, enabling prompt detection and response to suspicious behaviour or potential breaches. Moreover, they provide regular updates and patches to ensure that your systems are equipped with the latest defences against evolving threats. Overall, investing in a cyber security service can significantly enhance the resilience of your business and mitigate the risks posed by cyber adversaries.

What are the common types of cyber threats I should be aware of?

It is crucial for individuals and organisations to be aware of the common types of cyber threats that pose risks to their digital security. Some prevalent cyber threats include malware, which encompasses viruses, ransomware, and spyware designed to infiltrate systems and steal data. Phishing attacks are another common threat, where malicious actors use deceptive emails or messages to trick users into divulging sensitive information. Additionally, DDoS (Distributed Denial of Service) attacks can overwhelm networks, causing disruptions in services. Being informed about these and other cyber threats is essential in implementing effective security measures to mitigate risks and protect against potential breaches.

How do I choose the right cyber security service provider?

When considering how to select the most suitable cyber security service provider for your organisation, several key factors should be taken into account. Firstly, assess the provider’s experience and track record in the field. Look for a company with a proven history of successfully protecting businesses from cyber threats. Additionally, consider the range of services offered and ensure they align with your specific needs, whether it be network monitoring, threat detection, or incident response. It is also essential to evaluate the provider’s certifications and compliance with industry standards to guarantee they adhere to best practices. Lastly, look for a partner who offers excellent customer support and demonstrates a commitment to ongoing communication and collaboration throughout your engagement with them. By carefully evaluating these aspects, you can confidently choose a cyber security service provider that meets your requirements and safeguards your digital assets effectively.

What measures can be taken to prevent data breaches?

Data breaches are a significant concern in today’s digital landscape, but there are proactive measures that can be implemented to help prevent them. One key step is to regularly update and patch software systems to address known vulnerabilities that cyber criminals may exploit. Implementing strong access controls, such as multi-factor authentication and least privilege access, can limit the exposure of sensitive data. Encrypting data both at rest and in transit adds an additional layer of protection. Conducting regular security awareness training for employees to educate them on common threats like phishing emails and social engineering can also help prevent data breaches by reducing the human error factor. Lastly, having a robust incident response plan in place can enable swift detection and containment of breaches, minimising their impact on the organisation.

How often should my business conduct a security audit?

It is recommended that businesses conduct a security audit regularly to ensure the ongoing protection of their digital assets. The frequency of security audits may vary depending on factors such as the size of the business, industry regulations, and the evolving nature of cyber threats. Typically, businesses should consider conducting security audits at least annually or more frequently if there have been significant changes in the IT infrastructure, such as system upgrades or expansions. Regular security audits help identify vulnerabilities, assess risks, and implement necessary measures to strengthen the overall security posture of the business against potential cyber attacks.

What steps are involved in responding to a cyber attack?

When responding to a cyber attack, several critical steps are involved to mitigate the impact and restore security. The first step is to identify and contain the breach by isolating affected systems to prevent further spread of the attack. Next, it is crucial to assess the extent of the damage and analyse how the breach occurred. This analysis helps in understanding the attacker’s tactics and strengthens defences against future attacks. Following this, organisations must notify relevant stakeholders, including internal teams, regulatory bodies, and possibly law enforcement agencies, depending on the severity of the incident. Finally, a comprehensive recovery plan should be implemented to restore systems, data, and operations back to normalcy while continuously monitoring for any signs of reoccurrence. Swift and coordinated action during a cyber attack response is essential in minimising disruption and safeguarding sensitive information.

Can small businesses benefit from professional cyber security services?

Small businesses can greatly benefit from professional cyber security services. While larger corporations often have dedicated IT departments and resources to manage cyber threats, small businesses are equally vulnerable to attacks but may lack the expertise and tools to effectively protect their digital assets. By investing in cyber security services tailored to their needs, small businesses can enhance their defences against cyber threats, safeguard sensitive data, maintain customer trust, and ensure business continuity. Professional cyber security services provide proactive monitoring, threat detection, incident response, and compliance assistance that can help small businesses mitigate risks and focus on their core operations with peace of mind.

How does employee training contribute to overall cyber security?

Employee training plays a pivotal role in bolstering overall cyber security within an organisation. By educating employees on best practices, recognising common threats, and understanding their role in maintaining a secure environment, organisations can significantly reduce the risk of cyber attacks. Well-trained employees are more vigilant against phishing attempts, better equipped to create strong passwords, and more likely to follow established security protocols. This increased awareness and knowledge empower employees to act as the first line of defence against potential threats, ultimately strengthening the organisation’s cyber security posture and minimising vulnerabilities.

The Importance of Cybersecurity Compliance Services

In today’s digital age, where cyber threats are becoming increasingly sophisticated and prevalent, ensuring the security of your organisation’s data and IT infrastructure is paramount. Cybersecurity compliance services play a crucial role in helping businesses adhere to regulatory requirements and industry standards to protect sensitive information and mitigate risks.

What Are Cybersecurity Compliance Services?

Cybersecurity compliance services encompass a range of measures designed to ensure that an organisation’s security practices align with relevant laws, regulations, and standards. These services help businesses establish and maintain robust cybersecurity protocols to safeguard against data breaches, cyber attacks, and other malicious activities.

The Benefits of Cybersecurity Compliance Services

By investing in cybersecurity compliance services, organisations can enjoy a multitude of benefits, including:

  • Legal Compliance: Ensuring that your business meets all legal requirements related to data protection and cybersecurity regulations.
  • Risk Mitigation: Identifying potential vulnerabilities and implementing controls to reduce the risk of security incidents.
  • Enhanced Security: Implementing best practices for securing networks, systems, and data assets.
  • Reputation Protection: Demonstrating to customers, partners, and stakeholders that your organisation takes cybersecurity seriously.
  • Cost Savings: Avoiding costly fines, penalties, and remediation expenses associated with non-compliance.

Key Components of Cybersecurity Compliance Services

Cybersecurity compliance services typically include the following key components:

  • Risk Assessment: Identifying potential threats and vulnerabilities within the organisation’s IT infrastructure.
  • Policies and Procedures Development: Establishing clear guidelines for employees on how to handle sensitive information securely.
  • Security Audits: Conducting regular audits to assess the effectiveness of existing security controls.
  • Incident Response Planning: Developing protocols for responding to security incidents promptly and effectively.

The Future of Cybersecurity Compliance

As cyber threats continue to evolve, cybersecurity compliance services will play an increasingly vital role in helping businesses stay ahead of potential risks. By partnering with experienced cybersecurity professionals and leveraging advanced technologies, organisations can establish a strong security posture that protects their valuable assets from cyber attacks.

In conclusion, investing in cybersecurity compliance services is not just a regulatory obligation; it is a strategic imperative for any business looking to safeguard its reputation, mitigate risks, and secure its future in an increasingly digital world.


Essential Tips for Ensuring Cybersecurity Compliance: A Guide to Protecting Your Organisation

  1. Regularly review and update your cybersecurity policies and procedures.
  2. Ensure that your staff receive regular training on cybersecurity best practices.
  3. Implement strong access controls to protect sensitive data.
  4. Conduct regular security assessments and audits to identify vulnerabilities.
  5. Stay informed about the latest cybersecurity threats and trends.
  6. Encrypt sensitive data both at rest and in transit to enhance security.
  7. Maintain compliance with relevant regulations and standards in the industry.

Regularly review and update your cybersecurity policies and procedures.

It is essential for organisations to regularly review and update their cybersecurity policies and procedures to ensure they remain effective against evolving cyber threats. By staying proactive in assessing and refining security measures, businesses can better protect their valuable data and IT infrastructure. Regular reviews help identify any gaps or weaknesses in existing policies, allowing for timely adjustments to strengthen overall cybersecurity posture. Updating policies in line with the latest industry standards and best practices ensures that organisations are well-prepared to address emerging threats and maintain compliance with regulatory requirements.

Ensure that your staff receive regular training on cybersecurity best practices.

It is crucial to ensure that your staff receive regular training on cybersecurity best practices to strengthen your organisation’s security posture. By educating employees on the latest threats, phishing scams, password hygiene, and data handling procedures, you empower them to become proactive defenders against cyber attacks. Regular training sessions not only enhance awareness but also instil a culture of cybersecurity consciousness throughout the organisation, reducing the likelihood of human error leading to security breaches. Investing in continuous staff training is a proactive approach towards bolstering your cybersecurity defences and safeguarding sensitive information from potential threats.

Implement strong access controls to protect sensitive data.

Implementing strong access controls is a critical aspect of cybersecurity compliance services to safeguard sensitive data. By restricting access to authorised personnel only, organisations can prevent unauthorised users from compromising valuable information. Strong access controls involve implementing multi-factor authentication, role-based permissions, and regular monitoring of user activities to ensure that data remains secure and confidential. By enforcing stringent access controls, businesses can significantly reduce the risk of data breaches and maintain compliance with regulatory requirements, ultimately enhancing their overall cybersecurity posture.

Conduct regular security assessments and audits to identify vulnerabilities.

Conducting regular security assessments and audits is a critical tip in cybersecurity compliance services. By proactively evaluating your organisation’s IT infrastructure, you can identify vulnerabilities and potential weaknesses that may expose your data to cyber threats. These assessments help in understanding the effectiveness of existing security controls and implementing necessary measures to strengthen your defences. By staying vigilant and conducting frequent audits, you can stay one step ahead of cyber attackers and ensure that your cybersecurity practices remain robust and compliant with regulations.

Staying informed about the latest cybersecurity threats and trends is a crucial aspect of maintaining strong cybersecurity compliance services. By keeping abreast of evolving cyber threats and industry trends, organisations can proactively identify potential risks and adjust their security measures accordingly. Regularly monitoring cybersecurity news, attending industry conferences, and engaging with cybersecurity experts can provide valuable insights that help businesses stay one step ahead of cyber attackers. Being informed allows organisations to adapt their security strategies to address emerging threats effectively, ultimately enhancing their overall cybersecurity posture and ensuring compliance with relevant regulations.

Encrypt sensitive data both at rest and in transit to enhance security.

Encrypting sensitive data both at rest and in transit is a fundamental practice in cybersecurity compliance services. By applying encryption techniques to data stored on servers or devices and data transmitted between systems, organisations can significantly enhance their security posture. Encryption ensures that even if unauthorised individuals gain access to the data, they cannot decipher its contents without the encryption key. This proactive measure not only helps protect sensitive information from cyber threats but also demonstrates a commitment to maintaining the confidentiality and integrity of data, in line with regulatory requirements and industry best practices.

Maintain compliance with relevant regulations and standards in the industry.

It is crucial for businesses to maintain compliance with relevant regulations and standards in the industry when it comes to cybersecurity. By adhering to established guidelines and requirements, organisations can demonstrate their commitment to protecting sensitive data and ensuring the security of their IT infrastructure. Compliance with industry regulations not only helps mitigate risks associated with cyber threats but also enhances trust with customers, partners, and stakeholders. Regularly reviewing and updating security protocols in line with regulatory changes is essential to staying ahead of potential vulnerabilities and safeguarding against costly breaches.

Top Cybersecurity Threats

The Top Cybersecurity Threats Facing Businesses Today

In today’s digital age, businesses face an increasing number of cybersecurity threats that can compromise sensitive data, disrupt operations, and damage reputation. It is crucial for organisations to stay vigilant and proactive in defending against these threats. Here are some of the top cybersecurity threats that businesses need to be aware of:

Phishing Attacks

Phishing attacks involve sending deceptive emails or messages to trick individuals into revealing sensitive information such as login credentials or financial details. These attacks are becoming more sophisticated, making it challenging for users to distinguish legitimate communications from fraudulent ones.

Ransomware

Ransomware is a type of malware that encrypts files on a victim’s system and demands payment in exchange for decryption. Ransomware attacks can cause significant financial losses and operational disruptions, making them a serious threat to businesses of all sizes.

Data Breaches

Data breaches involve the unauthorised access or exposure of confidential information, such as customer data or intellectual property. Breaches can result from various factors, including weak security controls, insider threats, or vulnerabilities in software systems.

Insider Threats

Insider threats refer to risks posed by individuals within an organisation who misuse their access privileges to intentionally or unintentionally harm the company’s security posture. These threats can come from employees, contractors, or partners with insider knowledge of the organisation’s systems.

DDoS Attacks

Distributed Denial of Service (DDoS) attacks aim to overwhelm a target system with a flood of traffic, causing it to become inaccessible to legitimate users. DDoS attacks can disrupt online services, leading to downtime and financial losses for businesses.

Businesses must implement robust cybersecurity measures to mitigate these threats effectively. This includes conducting regular security assessments, educating employees on best practices, implementing multi-factor authentication, and keeping software systems up-to-date with security patches.

By staying informed about the latest cybersecurity trends and investing in proactive security measures, businesses can better protect themselves against evolving cyber threats and safeguard their valuable assets.


Understanding the Top 8 Frequently Asked Questions About Current Cybersecurity Threats

  1. What are the 3 major threats to cyber security today?
  2. What is 90% of cyber attacks?
  3. What are the 5 main threats to our cyber security?
  4. What are the 8 main cyber security threats?
  5. What are the top 5 major threats to cybersecurity?
  6. What is the #1 cybersecurity threat today?
  7. What are the biggest security threats right now?
  8. What are the 7 types of cyber security threats?

What are the 3 major threats to cyber security today?

In today’s digital landscape, the three major threats to cybersecurity that organisations face are phishing attacks, ransomware incidents, and data breaches. Phishing attacks involve deceptive tactics to trick individuals into disclosing sensitive information, while ransomware encrypts files and demands payment for decryption. Data breaches expose confidential data to unauthorised parties, leading to financial and reputational damage. These threats underscore the importance of robust cybersecurity measures to protect against evolving risks in the digital realm.

What is 90% of cyber attacks?

One frequently asked question regarding top cybersecurity threats is, “What constitutes 90% of cyber attacks?” It is widely acknowledged that a significant portion of cyber attacks, approximately 90%, are attributed to human error or negligence. This includes factors such as falling victim to phishing scams, using weak passwords, failing to update software promptly, or inadvertently disclosing sensitive information. Addressing these human-centric vulnerabilities through comprehensive training, robust security policies, and regular awareness campaigns is crucial in mitigating the majority of cyber threats faced by organisations today.

What are the 5 main threats to our cyber security?

In the realm of cybersecurity, it is crucial to understand the five main threats that pose significant risks to our digital safety. These threats include phishing attacks, which aim to deceive individuals into disclosing sensitive information; ransomware, a type of malware that encrypts files and demands payment for decryption; data breaches, where confidential information is exposed without authorisation; insider threats, which involve malicious or unintentional actions by individuals within an organisation; and Distributed Denial of Service (DDoS) attacks, designed to overwhelm systems with traffic. Awareness of these top cybersecurity threats is essential for businesses and individuals to enhance their defences and protect against potential cyber incidents.

What are the 8 main cyber security threats?

When it comes to cybersecurity, understanding the eight main cyber security threats is crucial for businesses and individuals alike. These threats encompass a range of risks, including phishing attacks, ransomware, data breaches, insider threats, DDoS attacks, malware infections, social engineering scams, and IoT vulnerabilities. Each threat poses unique challenges and requires specific preventive measures to mitigate potential damage. By staying informed about these top cyber security threats and implementing robust security practices, organisations can better protect their digital assets and reduce the risk of falling victim to malicious activities in today’s interconnected world.

What are the top 5 major threats to cybersecurity?

When it comes to cybersecurity, understanding the top 5 major threats is crucial for organisations to fortify their defences effectively. The landscape of cyber threats is ever-evolving, but some persistent dangers continue to pose significant risks. These include phishing attacks, where deceptive emails aim to trick individuals into divulging sensitive information; ransomware, a type of malware that encrypts files and demands payment for decryption; data breaches that expose confidential information; insider threats from individuals within the organisation misusing access privileges; and Distributed Denial of Service (DDoS) attacks that overwhelm systems with traffic. Staying informed about these prevalent threats allows businesses to implement targeted security measures and mitigate potential risks proactively.

What is the #1 cybersecurity threat today?

The question of what constitutes the number one cybersecurity threat today is a complex and dynamic issue, as the threat landscape continues to evolve rapidly. However, one prevalent and persistent threat that consistently ranks high on the list is phishing attacks. Phishing attacks involve deceptive tactics aimed at tricking individuals into divulging sensitive information, such as login credentials or financial details. These attacks are often sophisticated and can target individuals across various industries and sectors, highlighting the importance of robust cybersecurity measures and ongoing awareness training to mitigate the risks associated with phishing.

What are the biggest security threats right now?

Currently, the biggest security threats in the cybersecurity landscape encompass a range of sophisticated and evolving risks that organisations must contend with. From the pervasive threat of phishing attacks that target unsuspecting individuals to the insidious spread of ransomware that can cripple entire systems, businesses face a multitude of challenges in safeguarding their digital assets. Data breaches, whether due to external hackers or insider threats, continue to pose significant risks to sensitive information. Additionally, the persistent threat of Distributed Denial of Service (DDoS) attacks looms large, capable of disrupting online services and causing substantial financial harm. Staying vigilant and implementing robust security measures are essential in mitigating these top cybersecurity threats and fortifying defences against malicious actors.

What are the 7 types of cyber security threats?

In the realm of cybersecurity, understanding the various types of threats is essential for safeguarding digital assets. The seven primary types of cyber security threats include malware, phishing attacks, ransomware, insider threats, DDoS attacks, SQL injection, and zero-day exploits. Each threat poses unique risks to organisations and individuals, highlighting the importance of implementing robust security measures and staying vigilant against evolving cyber threats. By staying informed about these common threat vectors and adopting proactive security practices, businesses can enhance their resilience against potential cyber attacks.

Cybersecurity Compliance Consulting: A Practical Guide for UK Organisations

Cybersecurity compliance can be challenging to manage. Organisations must protect sensitive information, demonstrate that appropriate controls are in place and keep pace with changing legal and industry requirements. Cybersecurity compliance consulting helps make that work more structured, practical and proportionate to an organisation’s risks.

A consultant can assess existing security arrangements, identify gaps and help develop a clear plan for addressing them. The aim is not simply to prepare for an audit or achieve a certificate. It is to build security practices that support the organisation’s operations and stand up to scrutiny over time.

What is cybersecurity compliance consulting?

Cybersecurity compliance consulting is professional guidance on meeting relevant security standards, regulations and contractual obligations. The scope depends on the organisation’s sector, size, customers, systems and the information it handles.

Consultants may help an organisation understand which requirements apply, assess current controls and prepare evidence that shows how those controls work. They can also advise on policies, risk management, incident response, supplier security and staff awareness.

Compliance is not the same as security. Compliance focuses on meeting defined requirements, while security involves reducing the likelihood and impact of real-world threats. A strong programme connects the two: it meets applicable obligations while addressing the risks most relevant to the organisation.

Why compliance matters

Cybersecurity requirements can come from several sources, including legislation, industry standards, customer contracts and internal policies. Depending on the organisation, relevant considerations may include data protection duties, payment card requirements, sector-specific rules or recognised security frameworks.

Failing to manage these obligations can lead to regulatory action, contractual disputes, disruption and loss of customer confidence. Even where an organisation has no formal certification requirement, customers and business partners may expect it to demonstrate sound security practices.

A well-managed compliance programme can also provide practical benefits. It can clarify responsibilities, make risks easier to prioritise, improve incident readiness and give leadership a more reliable view of the organisation’s security posture.

What does a compliance consultant do?

The work should be tailored to the organisation rather than based on a generic checklist. Typical activities include:

  • Scoping requirements: identifying the laws, standards, contractual terms and customer expectations that apply.
  • Assessing current controls: reviewing policies, processes, technology and evidence against the relevant requirements.
  • Identifying gaps and risks: distinguishing urgent weaknesses from lower-priority improvements.
  • Developing a remediation plan: setting out actions, owners, dependencies and realistic timescales.
  • Improving documentation: helping create or update policies, procedures, risk registers and response plans.
  • Preparing for assessment: organising evidence and helping teams understand what an auditor or assessor may need to verify.
  • Supporting ongoing compliance: establishing processes for reviews, monitoring, staff training and continual improvement.

Consultants may also support technical work, such as reviewing access controls, vulnerability management, backup arrangements or security monitoring. The precise scope should be agreed in advance, including what is advisory and what requires implementation by the organisation or its technology providers.

A typical consulting process

Define the scope

The organisation and consultant agree which business units, systems, locations and information are in scope. Clear boundaries help prevent missed requirements and reduce unnecessary work.

Understand the business and its risks

The consultant gathers information about business operations, key services, data flows, suppliers and existing security arrangements. This context is essential: the same control may need to be applied differently in different organisations.

Review controls and evidence

Policies and technical settings are considered alongside evidence of how processes operate in practice. A written policy alone may not demonstrate that a control is consistently followed.

Prioritise improvements

Findings are translated into an action plan. Priorities should take account of the potential impact of a weakness, applicable deadlines, business constraints and the effort required to address it.

Implement and verify

Control improvements are put into practice, with responsibilities assigned to appropriate staff. Follow-up reviews help confirm that actions have been completed and are working as intended.

Maintain the programme

Compliance needs ongoing attention. Changes to systems, suppliers, business activities and requirements can affect the organisation’s obligations and risk profile. Regular reviews help keep controls relevant.

Choosing the right consultant

A useful consulting engagement depends on experience, independence and a good understanding of the organisation’s needs. When evaluating providers, consider asking:

  • Have they worked with organisations of a similar size or in a similar sector?
  • Can they explain the relevant requirements in clear, practical language?
  • Will the assessment be tailored to the organisation’s actual risks and systems?
  • What will the final deliverables include, and who will own each recommended action?
  • How will sensitive information gathered during the engagement be protected?
  • Can they support remediation or future reviews, if required?
  • Are any potential conflicts of interest disclosed?

Be cautious of promises of guaranteed compliance or certification. A consultant can guide and support an organisation, but accountability for its controls and decisions remains with the organisation. Certification or regulatory outcomes may also depend on independent assessors and the evidence available.

Common challenges to avoid

Organisations sometimes treat compliance as a one-off project, focus only on documentation or attempt to address every finding at once. These approaches can create significant effort without delivering lasting improvements.

It is generally more effective to assign clear ownership, connect recommendations to business risks and maintain evidence as part of normal operations. Staff involvement matters too: controls are more likely to work when people understand their purpose and know what is expected of them.

Another common challenge is overlooking third parties. Suppliers may have access to systems or information, so their security arrangements and contractual responsibilities should be considered as part of the wider programme.

Making compliance part of everyday security

Cybersecurity compliance consulting can help turn complex requirements into manageable actions. The most valuable outcome is not a collection of documents, but a clear understanding of the organisation’s obligations, risks and responsibilities.

By combining expert guidance with active leadership, practical controls and regular review, organisations can build a compliance programme that supports both assurance and resilience. Requirements vary, so organisations should seek advice suited to their circumstances and obtain legal guidance where interpretation of the law is required.


Essential Tips for Effective Cybersecurity Compliance Consulting

  1. Map applicable regulations before starting.
  2. Assess current controls against each requirement.
  3. Prioritise gaps by risk and impact.
  4. Keep evidence organised and up to date.
  5. Review compliance regularly as rules change.

Map applicable regulations before starting.

Before starting a cybersecurity compliance project, map the regulations, standards and contractual requirements that apply to your organisation. These may vary according to your sector, the information you handle, where you operate and the services you provide. A clear requirements map helps define the project’s scope, avoid duplicated effort and focus resources on the controls and evidence that matter. Review it regularly, as changes to your business or relevant requirements may affect your obligations.

Assess current controls against each requirement.

Assess your current controls against each applicable requirement to see where your organisation is meeting its obligations and where improvements are needed. Review not only written policies, but also how processes work in practice and what evidence demonstrates that controls are operating consistently. Recording gaps, risks and supporting evidence makes it easier to prioritise remediation and prepare for an audit or assessment.

Prioritise gaps by risk and impact.

Prioritise compliance gaps by considering the likelihood of exploitation and the potential impact on your organisation, customers and critical services. Address high-risk issues first, such as weaknesses that could expose sensitive data or disrupt essential systems, while scheduling lower-impact improvements appropriately. A risk-based approach helps direct time and resources where they will make the greatest difference, rather than treating every gap as equally urgent.

Keep evidence organised and up to date.

Keep evidence organised and up to date so you can show how your cybersecurity controls work in practice. Maintain a clear, securely stored record of items such as policies, risk assessments, training logs, access reviews, incident reports and supplier checks. Assign owners and review dates, and update documents whenever systems, processes or requirements change. This makes assessments easier, helps staff find reliable information quickly and can reveal gaps before they become compliance issues.

Review compliance regularly as rules change.

Review your compliance arrangements regularly, as cybersecurity rules, industry standards and contractual requirements can change. Schedule periodic reviews and reassess your controls whenever your systems, suppliers or business activities change. This helps identify gaps early and ensures your policies and procedures remain relevant, rather than relying on a one-off assessment.

Cloud-Based Cyber Security Solutions: A Practical Guide

As organisations move more of their operations online, protecting systems, data and users has become increasingly complex. Cloud-based cyber security solutions can help meet this challenge by providing security tools and services through cloud platforms. They can support organisations of different sizes, whether they operate entirely in the cloud or use a mix of cloud and on-premises systems.

What are cloud-based cyber security solutions?

Cloud-based cyber security solutions are security services that are hosted and managed, in whole or in part, in the cloud. Instead of relying solely on software installed on local servers or individual devices, an organisation accesses security capabilities through an internet connection or a cloud service provider.

These solutions cover a broad range of needs, including identity and access management, email protection, endpoint security, data loss prevention, threat detection, vulnerability management and security monitoring. Some are delivered as software, while others include managed services in which specialists help monitor and respond to threats.

Common types of cloud security services

  • Identity and access management: Controls who can access systems and data, and can apply measures such as multi-factor authentication and single sign-on.
  • Endpoint protection: Helps secure laptops, mobile devices and servers against malware and other threats, including devices used outside the office.
  • Email and collaboration security: Detects phishing, malicious attachments and suspicious links across email and workplace collaboration tools.
  • Cloud security posture management: Identifies misconfigurations and policy gaps across cloud environments.
  • Security information and event management: Collects and analyses security events from multiple sources to help teams identify unusual activity.
  • Data protection: Helps classify, encrypt and control access to sensitive information, and may alert teams to unauthorised sharing or transfer.
  • Backup and recovery: Supports the restoration of data and services after accidental deletion, hardware failure or a cyber incident.

Potential benefits

Scalability and flexibility

Cloud services can often be adjusted as an organisation’s needs change. New users, locations or workloads may be added without building the same level of on-site infrastructure. This can be useful for growing businesses and organisations with distributed teams.

Centralised visibility

Cloud-based tools can bring information from different systems into a central dashboard. This may help security teams spot patterns, investigate alerts and apply consistent policies across users and devices. The quality of this visibility depends on which systems are connected and how the tools are configured.

Access to current capabilities

Cloud providers typically manage the underlying service and may release updates without requiring an organisation to install every update manually. However, customers still need to understand which security tasks are handled by the provider and which remain their responsibility.

Support for remote and hybrid work

Cloud-delivered security controls can protect users who work from different locations, rather than relying only on a traditional office network. Access policies can take account of factors such as user identity, device health and the sensitivity of the resource being requested.

Potentially lower infrastructure overhead

Using a cloud service may reduce the need to purchase and maintain certain servers or appliances. It does not automatically make security less expensive: subscription fees, implementation, training, integration and ongoing management should all be included in the total cost assessment.

Challenges to consider

Cloud-based security is not a complete solution on its own. Organisations should consider several practical issues before choosing a service.

  • Shared responsibility: The provider secures aspects of its platform, but the organisation is usually responsible for areas such as user permissions, data classification and service configuration. Responsibilities vary by service and contract.
  • Configuration errors: Weak access rules, exposed storage or excessive permissions can create risk. Secure defaults and regular configuration reviews are important.
  • Data protection and compliance: Organisations should understand where data is stored, how it is processed, how long it is retained and whether the service supports their legal and regulatory obligations.
  • Integration and compatibility: A solution needs to work with existing systems, identity services and operational processes. Poor integration can leave gaps or generate excessive alerts.
  • Dependence on connectivity: Cloud services rely on network access. Organisations should plan for outages and ensure that critical processes have suitable continuity arrangements.
  • Alert overload: A security platform can produce more alerts than a team can investigate. Tuning, prioritisation and clear response procedures help make alerts actionable.
  • Provider and concentration risk: Relying heavily on one provider may make it harder to change services or recover from a provider-level disruption. Exit plans and backup arrangements should be considered.

How to choose a solution

Start by identifying the risks and business requirements the solution needs to address. A small organisation seeking better protection for email and user accounts may have different priorities from a large organisation managing multiple cloud platforms and complex compliance requirements.

  1. Assess the environment: List the systems, data, users and cloud services that need protection. Include existing security tools and known gaps.
  2. Define requirements: Set out essential features, reporting needs, integration requirements, service availability expectations and compliance considerations.
  3. Review security and privacy controls: Ask how the provider protects data, manages access, handles incidents, tests its service and communicates security changes.
  4. Check operational fit: Consider who will monitor alerts, investigate incidents and maintain configurations. A tool is only effective if responsibilities are clear.
  5. Evaluate costs and contracts: Review subscription pricing, usage limits, support, data retention, renewal terms and the process for exporting or deleting data when the contract ends.
  6. Test before wider deployment: A pilot can reveal integration issues, unexpected costs or workflow changes before the service is rolled out across the organisation.

Best practices for implementation

Begin with strong identity controls. Require multi-factor authentication for important accounts, remove unnecessary access and review permissions regularly. Where possible, use the principle of least privilege: users and services should have only the access they need to do their jobs.

Keep security configurations under review, and enable logging for important systems. Logs are most useful when they are retained appropriately, protected from tampering and connected to a clear process for investigation. Establish incident response procedures that explain who should act, how incidents should be escalated and how relevant data will be preserved.

Cloud services should also be included in backup and recovery planning. Confirm what is backed up, how often backups are made, how long they are retained and whether recovery has been tested. A backup that has never been restored in a test may not provide the assurance an organisation expects.

Finally, provide regular training for staff. Technical controls can reduce risk, but people still need to recognise suspicious messages, report unusual activity and understand how to handle sensitive information.

Conclusion

Cloud-based cyber security solutions can help organisations protect users, devices, applications and data across increasingly distributed environments. Their benefits include flexibility, centralised visibility and access to a broad range of security capabilities. Those benefits depend on choosing suitable services, configuring them correctly and maintaining clear responsibility for security tasks.

The strongest approach is not simply to adopt more tools. It is to understand the organisation’s risks, select solutions that address them, and combine technology with sound processes, skilled oversight and regular review.


Understanding Cloud-Based Cybersecurity: Common Questions and Solutions

  1. What types of cloud security solutions are available?
  2. What is cloud-based cybersecurity?
  3. What is an example of a cloud-based solution?
  4. What is an example of cloud security?
  5. What is cloud-based cyber security?
  6. What are the 3 categories of cloud security?

What types of cloud security solutions are available?

Cloud security solutions cover a range of needs, including identity and access management, multi-factor authentication, email and endpoint protection, data encryption and loss prevention, cloud configuration monitoring, vulnerability management, threat detection and security information and event management (SIEM). Organisations can also use cloud-based backup and disaster recovery services, or managed security services where specialists monitor systems and help respond to incidents. The right combination depends on the organisation’s cloud environment, the data it handles and its security requirements.

What is cloud-based cybersecurity?

Cloud-based cybersecurity is the protection of data, applications, users and systems using security tools and services delivered through the cloud. These may include identity and access controls, threat detection, email and endpoint protection, data encryption and backup. The cloud provider manages parts of the service, but organisations remain responsible for tasks such as setting permissions, configuring security policies and protecting their data. The precise division of responsibilities depends on the service and provider.

What is an example of a cloud-based solution?

An example of a cloud-based cyber security solution is a cloud email security service. It scans incoming and outgoing messages for phishing attempts, malicious links and infected attachments, with protection managed through an online platform rather than software installed on a local server. Administrators can review alerts and adjust security settings through a web browser.

What is an example of cloud security?

An example of cloud security is a cloud-based identity and access management service that requires multi-factor authentication before users can access company applications or data. It can also apply access rules based on factors such as a user’s role, device or location, helping reduce the risk of unauthorised access.

What is cloud-based cyber security?

Cloud-based cyber security is the protection of data, users, applications and systems using security services delivered through the cloud. These services can include identity and access management, threat detection, email and endpoint protection, data encryption and backup. They help organisations monitor and secure resources across different locations, while responsibility is typically shared between the cloud provider and the customer.

What are the 3 categories of cloud security?

There is no single universal set of three categories, but cloud security is often grouped into **infrastructure security**, **data security**, and **identity and access management**. Infrastructure security protects the cloud networks, servers and platforms; data security safeguards information through measures such as encryption, backups and access controls; and identity and access management ensures that only authorised people and services can use cloud resources. These areas overlap, and organisations should address all three as part of a wider security programme.