Global Compliance Software: A Guide for International Businesses

Operating across borders can open up new markets and opportunities, but it also brings a complex set of legal and regulatory responsibilities. Requirements may differ between countries, industries and even regions within the same country. Global compliance software helps organisations manage these obligations in a more structured and consistent way.

What is global compliance software?

Global compliance software is technology designed to help businesses identify, organise and monitor their compliance responsibilities across multiple jurisdictions. Depending on the product, it may support areas such as data protection, financial controls, employment practices, health and safety, environmental standards, trade regulations and industry-specific requirements.

Rather than replacing legal or compliance professionals, the software gives them tools to manage information, coordinate tasks and maintain evidence. Its features can range from a central register of obligations to automated workflows, audit records and risk dashboards.

Why does global compliance matter?

International businesses often face overlapping requirements. A company might need to follow local employment laws while also meeting group-wide policies, contractual commitments and regulations that apply to its sector. Keeping track of changes across different locations can be challenging, particularly when information is spread across spreadsheets, email and separate systems.

Weak compliance processes can lead to financial penalties, operational disruption, disputes and damage to an organisation’s reputation. They can also make it harder to demonstrate that appropriate controls are in place. A well-managed compliance programme helps businesses understand their responsibilities and respond to issues in a timely, documented way.

Common features

Capabilities vary, but global compliance platforms may include:

  • Regulatory and obligation registers: A structured record of relevant laws, standards, policies and other requirements.
  • Change monitoring: Tools to help teams track regulatory developments and assess whether internal processes need to change.
  • Risk assessments: Workflows for identifying, evaluating and prioritising compliance risks across business units or locations.
  • Task management: Assigned actions, deadlines, reminders and approval processes to support accountability.
  • Policy management: Document control, review cycles, version histories and employee acknowledgements.
  • Training records: Ways to assign learning, monitor completion and retain evidence of participation.
  • Incident and case management: Secure processes for recording concerns, investigations, actions and outcomes.
  • Audit support and reporting: Records and reports that help teams review controls and prepare evidence for internal or external audits.
  • Integration: Connections with systems such as identity management, human resources, finance, document storage and enterprise risk platforms.

Benefits for multinational organisations

A central platform can give authorised teams a more consistent view of compliance activity across the organisation. Local teams can manage jurisdiction-specific requirements, while group functions can monitor common risks, overdue actions and emerging issues.

Automation may reduce repetitive administration, such as sending reminders or routing approvals. Clear ownership and audit trails can also make it easier to understand who completed an action, when it was completed and what evidence supports it. These capabilities can improve coordination, although they do not guarantee compliance on their own.

Another potential benefit is better-informed decision-making. When compliance information is organised and current, leaders may be better placed to consider regulatory risk when entering a new market, launching a product or changing a business process.

Choosing the right software

The most suitable platform depends on an organisation’s size, sector, locations and existing processes. Before comparing products, businesses should define the problems they need to solve. For example, the priority may be tracking regulatory changes, managing policies, coordinating audits or improving visibility of obligations across subsidiaries.

Useful questions to ask vendors include:

  • Can the platform support the jurisdictions and regulatory areas relevant to the business?
  • How are legal and regulatory updates sourced, checked and communicated?
  • Can local teams adapt workflows without weakening central oversight?
  • What reporting, audit trails and evidence-management features are available?
  • How does the software protect sensitive information and control user access?
  • Can it integrate with the organisation’s existing systems?
  • What support, training and implementation services are included?
  • How are product changes, data retention and service continuity managed?

It is also important to assess usability. If the system is difficult to navigate, staff may avoid using it or maintain separate records elsewhere. A pilot involving both central and local teams can help test whether the platform fits real working practices.

Implementation: people and processes matter

Buying software is only one part of building an effective compliance programme. Organisations should first agree on responsibilities, approval routes and definitions of key terms. They should then decide which data to migrate, how to handle existing records and who will maintain the system over time.

Training should be tailored to different users. A compliance manager may need detailed reporting and administration skills, while other employees may only need to complete assigned tasks or acknowledge policies. Clear guidance can help staff understand how the platform supports their role and where to raise questions.

Businesses should also review the quality of the information entered into the system. Inaccurate obligation records, unclear ownership or outdated policies can undermine even the most capable software. Regular reviews help keep the platform relevant as the organisation and its regulatory environment change.

Limitations to keep in mind

Global compliance software cannot interpret every legal issue in context or replace qualified advice. Regulatory obligations may depend on a company’s activities, customers, data, contractual relationships and local circumstances. Organisations should confirm that information is relevant to their situation and involve legal or compliance specialists where appropriate.

Nor does a central dashboard prove that controls are working. Effective compliance still depends on suitable policies, informed people, practical procedures, management oversight and a willingness to address problems. Software can support these elements by making responsibilities and evidence easier to manage.

The future of global compliance software

Platforms are increasingly exploring automation, analytics and artificial intelligence to help organise large volumes of regulatory information and identify patterns. These tools may assist with research or prioritisation, but their outputs need appropriate review. Businesses should understand how automated recommendations are produced, what information they rely on and how errors can be corrected.

As organisations face changing expectations around data use, supply chains, sustainability and responsible technology, compliance systems are likely to become more connected with wider risk management. The aim is not simply to collect more data, but to help people identify relevant obligations and take timely, well-documented action.

Conclusion

Global compliance software can help international businesses bring obligations, tasks and evidence into a more manageable framework. The right solution can improve visibility, support consistent processes and make coordination across locations easier. Its value, however, depends on choosing a platform that fits the organisation, maintaining reliable information and combining technology with knowledgeable people and effective governance.


Global Compliance Software: FAQs on Leading Tools, Key Functions and Top Concerns for 2026

  1. What are the top 10 global compliance concerns for 2026?
  2. What is the best GRC tool?
  3. What does global compliance do?
  4. What is the best compliance software?

What are the top 10 global compliance concerns for 2026?

The top 10 global compliance concerns for 2026 will vary by industry and jurisdiction, but key priorities include: (1) data privacy and cross-border data transfers; (2) artificial intelligence governance and evolving AI regulations; (3) cyber security and incident-reporting obligations; (4) anti-money laundering and counter-terrorist financing; (5) international sanctions and export controls; (6) anti-bribery and corruption; (7) sustainability reporting and environmental claims; (8) supply chain due diligence, including human rights and forced labour risks; (9) employment law and whistleblower protection; and (10) international tax transparency and reporting. Global compliance software can help organisations track relevant regulatory changes, assign responsibilities and maintain evidence, but requirements must be assessed against each business’s activities and locations.

What is the best GRC tool?

There is no single “best” GRC (governance, risk and compliance) tool for every organisation. The right choice depends on factors such as your industry, size, locations, regulatory obligations, existing systems and budget. Compare platforms for the capabilities you need—such as risk assessments, compliance tracking, audit management, reporting and integrations—and consider usability, security, implementation support and scalability. A shortlist, followed by a demonstration or pilot with the teams who will use the software, can help you find the best fit for your organisation.

What does global compliance do?

Global compliance helps an organisation meet the laws, regulations, industry standards and internal policies that apply to its operations in different countries. Global compliance software supports this work by bringing obligations, policies, risks, tasks and evidence together in one place, helping teams track changes, assign responsibilities and monitor progress. It can improve oversight and record-keeping, but it does not replace legal advice or the need for effective processes and informed staff.

What is the best compliance software?

The best compliance software is the one that fits your organisation’s regulatory requirements, size, industry and day-to-day processes. Look for a platform that covers the jurisdictions and compliance areas relevant to your business, keeps records and audit trails, assigns actions clearly, and provides useful reporting. Security, integration with existing systems, ease of use, reliable regulatory updates and quality customer support also matter. Before choosing, define your priorities, compare providers and test shortlisted products with the teams who will use them. No software can guarantee compliance or replace expert legal advice, so consider how well the platform supports your people, policies and controls.

Cloud Computing Identity and Access Management

As organisations move applications, data and infrastructure to the cloud, controlling who can access each resource becomes increasingly important. Cloud computing identity and access management (IAM) provides the policies and tools needed to verify identities and grant appropriate access. Done well, IAM helps protect sensitive information while allowing people and services to work efficiently.

What is cloud IAM?

Identity and access management is the process of managing digital identities and deciding what they are permitted to do. In a cloud environment, IAM controls access to services such as virtual machines, databases, storage, applications and administrative settings.

An identity might represent a person, such as an employee or contractor, or a non-human entity, such as an application, server or automated process. IAM typically combines authentication—checking that an identity is genuine—with authorisation—deciding which actions that identity can perform.

Why IAM matters in the cloud

Cloud platforms make it possible to create and access resources quickly, sometimes across multiple regions, accounts or providers. This flexibility can also make access harder to oversee. Permissions may accumulate as people change roles, temporary accounts may remain active, and automated services may be given more access than they need.

Weak or poorly managed access can increase the risk of data exposure, account takeover and disruption to services. Strong IAM helps organisations reduce these risks, maintain clearer oversight and support regulatory and internal security requirements. It is also an important part of the shared responsibility model: cloud providers secure their underlying platforms, while customers are responsible for managing many aspects of access to their own cloud resources.

Core IAM components

  • Identities: User accounts and service identities that need access to cloud resources.
  • Authentication: The process of verifying an identity, using methods such as passwords, security keys, certificates or multi-factor authentication (MFA).
  • Authorisation: The rules that determine which resources an identity can access and what actions it can take.
  • Roles and policies: Sets of permissions assigned according to a user’s responsibilities or a service’s purpose.
  • Federation and single sign-on: Ways to connect cloud services to an organisation’s existing identity system, so users can sign in through a familiar, centrally managed process.
  • Logging and monitoring: Records of sign-ins and access changes that help teams investigate activity and identify unusual behaviour.

Principles for effective cloud access

Apply least privilege

Give each identity only the access needed to perform its tasks—and only for as long as it is needed. Avoid broad permissions for convenience. Where possible, use time-limited access for sensitive or administrative tasks.

Use MFA for important accounts

MFA adds another verification step beyond a password. It is particularly valuable for administrator accounts, remote access and systems containing sensitive information. Stronger methods, such as security keys or passkeys, can offer better protection against phishing than passwords alone.

Separate everyday and administrative accounts

People who manage cloud environments should use standard accounts for routine work and separate privileged accounts for administrative tasks. This reduces the impact of a compromised everyday account and makes privileged activity easier to monitor.

Manage non-human identities carefully

Applications and automated workloads often need credentials to communicate with cloud services. These credentials should be scoped to specific tasks, stored securely and rotated or replaced according to a defined process. Avoid embedding long-lived secrets in source code, scripts or configuration files. Where available, use managed identities or short-lived credentials.

Review access regularly

Access should change when people join, move roles or leave. Regular reviews can uncover unused accounts, excessive permissions and outdated access arrangements. Automated provisioning and de-provisioning can help, but changes should still be checked and monitored.

Common challenges

Cloud IAM can become complex when an organisation uses several cloud providers, identity systems and business applications. Different platforms may use different terminology and permission models. Misconfigured policies can also be difficult to spot, particularly when permissions are inherited or combined across multiple roles.

Another challenge is balancing security with usability. Excessive restrictions can slow legitimate work, while overly broad access creates unnecessary risk. Clear ownership, well-designed roles and a documented approval process help teams find a workable balance.

Building a stronger IAM programme

A practical starting point is to inventory cloud accounts, identities and privileged access. Next, identify critical systems and sensitive data, then review who can reach them and what they can do. Prioritise MFA, least privilege and the removal of unused accounts. Establish processes for access requests, approvals, role changes and periodic reviews.

Monitoring is essential as well. Collect and review authentication events, permission changes and other relevant audit records. Alerts can help highlight suspicious sign-ins or unexpected changes, while regular testing can reveal gaps in policies and procedures.

Conclusion

Cloud computing identity and access management is more than a set of permissions: it is an ongoing process for managing identities, controlling access and responding to change. By combining strong authentication, least privilege, careful management of service identities and regular reviews, organisations can make cloud access more secure and accountable without preventing people from doing their work.


Cloud Identity and Access Management (IAM): 7 Frequently Asked Questions

  1. Is IAM a good career?
  2. What is identity and access management in cloud computing?
  3. What are the 5 pillars of IAM?
  4. What are the benefits of IAM in the cloud?
  5. What is IAM role in cloud computing?
  6. What is consumer identity and access management in the cloud?
  7. What are the top 10 IAM tools?

Is IAM a good career?

Yes, identity and access management (IAM) can be a rewarding career, particularly as organisations rely on cloud services and need to protect access to systems and data. IAM roles range from administration and engineering to security architecture, governance and consultancy, offering opportunities to develop both technical and problem-solving skills. Knowledge of cloud platforms, authentication methods, access controls and security standards can be valuable, while clear communication is also important when working with users and teams across an organisation. As with any career, prospects depend on experience, interests and the needs of the job market, but IAM offers a range of routes for people interested in cybersecurity and cloud computing.

What is identity and access management in cloud computing?

Identity and access management (IAM) in cloud computing is the system of policies and tools used to verify who is accessing cloud resources and control what they are allowed to do. It manages identities such as employees, administrators and applications, using measures such as authentication, multi-factor authentication and role-based permissions. Effective cloud IAM helps ensure that each identity has only the access it needs, reducing the risk of unauthorised access to data and services.

What are the 5 pillars of IAM?

The five pillars of identity and access management (IAM) are commonly described as identity lifecycle management, authentication, authorisation, access governance and auditing. Together, they cover creating, updating and removing identities; verifying that users and services are who they claim to be; granting only the permissions they need; reviewing and managing those permissions over time; and recording access activity for monitoring and investigation. The terminology can vary between frameworks, but these principles help organisations manage cloud access securely throughout an identity’s lifecycle.

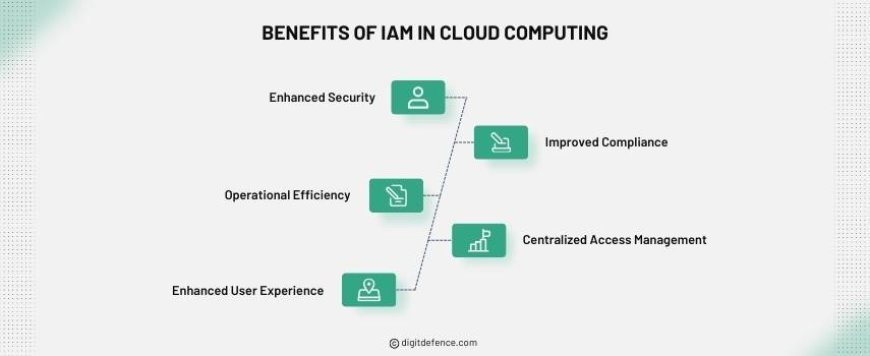
What are the benefits of IAM in the cloud?

Cloud IAM helps organisations protect cloud resources by ensuring users and services can access only what they need. It can reduce the risk of unauthorised access and data breaches through measures such as multi-factor authentication, role-based permissions and timely removal of outdated accounts. Centralised identity management also makes it easier to manage access across cloud services, support compliance requirements and review activity through audit logs. With well-designed IAM, organisations can strengthen security while making sign-in and access processes more consistent for staff.

What is IAM role in cloud computing?

An IAM role in cloud computing is a set of permissions that defines what an identity can do with specific cloud resources. Rather than being tied directly to one person, a role can be assigned temporarily to a user, application or service when access is needed. For example, a role might allow an application to read files from a particular storage area without granting access to other services. Using roles helps apply the principle of least privilege and makes it easier to manage access consistently.

What is consumer identity and access management in the cloud?

Consumer identity and access management (CIAM) in the cloud is the set of cloud-based tools and processes used to manage customer identities and their access to an organisation’s websites, apps and digital services. It enables customers to register, sign in and manage their accounts, while helping organisations protect personal information and control access. CIAM commonly includes features such as single sign-on, multi-factor authentication, consent management and integration with other services. As customer-facing systems can handle large numbers of users, a well-designed CIAM solution should balance security and privacy with a straightforward sign-in experience.

What are the top 10 IAM tools?

The top 10 IAM tools depend on your cloud platforms and requirements, but widely used options include Microsoft Entra ID, AWS Identity and Access Management (IAM), Google Cloud IAM, Okta, Ping Identity, IBM Security Verify, SailPoint, CyberArk, One Identity and Auth0. They cover different needs, from cloud permissions and single sign-on to identity governance, privileged access management and customer identity. Compare them based on compatibility with your environment, security features, ease of administration, integration options and cost.

Cyber Security Endpoint Protection: A Practical Guide

Every laptop, desktop, mobile phone and server connected to a business network can provide an entry point for cyber attackers. As organisations rely on more devices and support remote working, protecting these endpoints has become an essential part of cyber security.

Endpoint protection helps prevent, detect and respond to threats affecting devices. It is not a single product or setting, but a combination of technology, policies and good security practices designed to reduce risk across an organisation.

What is an endpoint?

An endpoint is a device that connects to a network and sends or receives data. Common examples include:

  • Desktop computers and laptops
  • Mobile phones and tablets
  • Servers and virtual machines
  • Internet of Things (IoT) devices
  • Devices used by staff working remotely

Each endpoint may store sensitive information or provide access to business systems. If a device is compromised, attackers may use it to steal data, install malware or move further into the network.

How endpoint protection works

Traditional antivirus software mainly looks for known malicious files and activity. Modern endpoint protection can offer broader capabilities, combining several methods to identify and manage threats, including:

  • Malware prevention: Detecting or blocking malicious software, including ransomware.
  • Behaviour monitoring: Identifying suspicious activity, even when a threat has not been seen before.
  • Device control: Managing the use of removable media, such as USB drives.
  • Host firewalls: Controlling network connections to and from individual devices.
  • Endpoint detection and response (EDR): Giving security teams tools to investigate activity and contain incidents on devices.
  • Centralised management: Applying security policies and reviewing alerts across an organisation from a central console.

Some organisations also use extended detection and response (XDR), which can bring together information from endpoints, email, cloud services and network systems to help identify connected threats.

Why endpoint protection matters

Endpoints are often targeted because people use them to open emails, visit websites, download files and access cloud services. A convincing phishing message or a vulnerable application can lead to a device being compromised.

Effective endpoint protection can help organisations to:

  • Reduce the likelihood of malware infections and unauthorised access
  • Spot unusual activity earlier
  • Limit the spread of an attack by isolating affected devices
  • Protect business and customer information
  • Support incident investigation and recovery
  • Meet security and compliance requirements where applicable

No endpoint product can guarantee that every attack will be prevented. Protection is strongest when endpoint controls form part of a wider security programme.

Building an effective endpoint protection strategy

Keep devices and software up to date

Security updates fix weaknesses that attackers may exploit. Establish a process for applying updates to operating systems, applications and security tools. Where possible, automate patching and monitor devices that are out of date or no longer supported.

Use strong access controls

Give users only the access they need to do their jobs. Avoid using administrator accounts for routine tasks, and use multi-factor authentication for important accounts and services. Strong access controls can limit the damage if a password or device is compromised.

Secure devices wherever they are used

Business devices may connect from offices, homes and public networks. Apply consistent security policies across locations, encrypt devices that store sensitive information and ensure that lost or stolen equipment can be disabled or wiped where appropriate.

Configure protection properly

Installing endpoint security software is only the beginning. Review its settings, enable relevant protective features and make sure alerts are directed to someone who can act on them. Test policy changes before applying them widely to avoid disrupting essential work.

Prepare to respond to incidents

Decide in advance how the organisation will handle a suspected compromise. Response procedures should cover how to isolate a device, preserve useful evidence, notify the right people and restore normal operations safely. Regular exercises can help teams understand their roles.

Train staff

People play an important role in endpoint security. Clear, practical training can help staff recognise suspicious messages, handle sensitive data safely and report unusual activity promptly. Make it easy for people to report a concern without fear of blame.

Choosing an endpoint protection solution

The right solution depends on an organisation’s size, devices, working practices and security resources. When evaluating products, consider:

  • Which operating systems and device types are supported
  • How policies and alerts are managed
  • Whether the solution offers investigation and response features
  • How it integrates with existing security tools
  • What information it collects and how that information is protected
  • How much time and expertise are needed to operate it
  • What support is available during an incident

A feature-rich platform is not automatically the best choice. The solution should match the organisation’s ability to configure, monitor and respond to it.

Measuring effectiveness

Organisations can review practical measures such as the proportion of devices covered by protection, how quickly security updates are applied, the number of devices with unresolved alerts and the time taken to investigate incidents. These measures can reveal gaps and help track improvement over time.

Conclusion

Endpoint protection is a fundamental part of cyber security because connected devices are both valuable business tools and potential targets. A combination of suitable technology, timely updates, sensible access controls, staff awareness and tested response procedures can make it harder for attackers to succeed and easier for an organisation to respond when something goes wrong.

For the best results, treat endpoint protection as an ongoing process. Review device coverage and security policies regularly, investigate alerts promptly and adapt controls as the organisation’s technology and risks change.


Endpoint Protection in Cyber Security: 8 Frequently Asked Questions

  1. What is endpoint protection in cyber security?
  2. How does endpoint protection work?
  3. Why is endpoint protection important for businesses?
  4. What is the difference between antivirus and endpoint protection?
  5. What is endpoint detection and response (EDR)?
  6. Which devices need endpoint protection?
  7. How can a business choose the right endpoint protection solution?
  8. How often should endpoint protection software and policies be updated?

What is endpoint protection in cyber security?

Endpoint protection in cyber security is the practice of securing devices that connect to an organisation’s network, such as laptops, desktop computers, servers and mobile phones. It uses tools and policies to help prevent, detect and respond to threats including malware, ransomware and unauthorised access. Depending on the solution, it may include antivirus, behaviour monitoring, device controls and centralised management, helping organisations protect data and limit the impact of security incidents.

How does endpoint protection work?

Endpoint protection works by securing devices such as laptops, desktops, servers and mobile phones against cyber threats. It combines tools such as malware detection, behaviour monitoring, firewalls and security policies to identify and block suspicious activity. Many solutions also send alerts to a central management system, where security teams can investigate threats and isolate affected devices to help prevent an attack from spreading.

Why is endpoint protection important for businesses?

Endpoint protection is important for businesses because every connected device—such as a laptop, mobile phone or server—can be a target for cyber attacks and a route into sensitive systems. Effective protection helps prevent and detect threats such as malware, ransomware and unauthorised access, while enabling teams to respond quickly if a device is compromised. It can also reduce the risk of data loss, business disruption and reputational damage. As part of a wider cyber security strategy, endpoint protection helps businesses safeguard their information and maintain more secure operations.

What is the difference between antivirus and endpoint protection?

Antivirus software primarily detects, blocks and removes malware, often by comparing files with known threat signatures and monitoring for suspicious behaviour. Endpoint protection is a broader approach that may include antivirus alongside tools such as firewalls, device and application controls, threat monitoring, and endpoint detection and response (EDR). In short, antivirus is one component of endpoint protection, which aims to secure and manage a wider range of devices and respond to threats across them.

What is endpoint detection and response (EDR)?

Endpoint detection and response (EDR) is a cyber security technology that continuously monitors activity on devices such as computers, laptops and servers to identify suspicious behaviour. Unlike traditional antivirus, which mainly blocks known threats, EDR can help detect unfamiliar attacks, investigate what happened and support a rapid response—for example, isolating a compromised device from the network. It gives security teams greater visibility of endpoint threats, but works best alongside measures such as regular updates, access controls and staff training.

Which devices need endpoint protection?

Endpoint protection should be installed on every device that connects to your organisation’s network or accesses its data. This includes desktops, laptops, servers, mobile phones and tablets, as well as virtual machines and, where supported, internet-connected devices such as printers. Include devices used by remote and hybrid workers, and make sure both company-owned and approved personal devices are covered by appropriate security policies.

How can a business choose the right endpoint protection solution?

A business should choose an endpoint protection solution based on its size, risk profile, budget and the devices it needs to secure, including laptops, mobiles and servers. Compare key features such as malware prevention, behaviour monitoring, central management and incident response, as well as compatibility with existing systems and the time and expertise needed to manage the product. Check the provider’s support, privacy practices and total cost, and consider trialling the solution with a small group of users before rolling it out across the organisation.

How often should endpoint protection software and policies be updated?

Endpoint protection software should be configured to receive updates automatically, with security and threat intelligence updates applied as soon as they become available. Operating systems and other applications should also be patched promptly, following a risk-based schedule. Review endpoint policies at least quarterly, and whenever there are significant changes to devices, working practices or security risks—or after an incident—to ensure they remain effective and appropriate.

Untangle Firewall: An Overview

Untangle firewall is a network security platform designed to help organisations control internet access, protect devices and manage traffic passing through their networks. It is best known for its modular approach: administrators can combine firewalling with additional security and monitoring tools to suit their requirements.

The product was historically known as Untangle NG Firewall. Following Untangle’s acquisition by Arista Networks, it has also been referred to as Arista NG Firewall. Product names, features and licensing can change, so check the provider’s current documentation before choosing or deploying it.

What Does Untangle Firewall Do?

At its core, a firewall monitors network traffic and applies rules to decide what should be allowed or blocked. Untangle extends this role with tools that can help administrators inspect traffic, manage users’ access to online services and respond to potential threats.

Depending on the edition and configuration, available capabilities may include:

  • Firewall rules: Control traffic by factors such as source, destination, service or network interface.
  • Intrusion prevention: Inspect traffic for patterns associated with known attacks.
  • Web filtering: Restrict access to websites by category or policy.
  • Application control: Identify or manage the use of selected applications and online services.
  • VPN access: Connect remote users or sites to a protected network, subject to the available configuration.
  • Reporting and monitoring: Review traffic and security events to support troubleshooting and policy decisions.

Not every capability is necessarily included in every version or subscription. Administrators should confirm which features are available and how they are licensed.

How Its Modular Design Works

Untangle’s interface has traditionally presented many security functions as separate applications or modules. This can make it easier to enable only the tools a network needs, rather than managing a single, fixed set of features.

That flexibility also calls for careful planning. Enabling several inspection and filtering tools may affect performance, particularly on a busy network or on hardware with limited resources. A sensible deployment starts with the organisation’s security requirements, expected traffic levels and available hardware.

Deployment Options

Untangle firewall has been available for deployment on dedicated appliances and compatible hardware, as well as in virtualised environments. The right option depends on the size and layout of the network, the organisation’s IT skills and its approach to maintenance.

Before installation, plan where the firewall will sit in the network, how internal and external connections will be configured, and how administrators will reach the management interface. It is also important to have a recovery plan in case a change disrupts access to the internet or business systems.

Potential Benefits

  • Centralised administration: Firewall and related security settings can be managed through a shared interface.
  • Configurable protection: Modular tools can help tailor policies to different users, devices or network needs.
  • Traffic visibility: Reports can help teams understand network use and investigate unusual activity.
  • Support for smaller IT teams: A combined platform may reduce the need to administer several separate products, depending on the organisation’s setup.

Points to Consider

A firewall is only one part of a broader security strategy. It cannot replace secure passwords, multi-factor authentication, timely software updates, endpoint protection, reliable backups or staff awareness. Nor does installing a firewall guarantee that a network is secure.

Organisations should also assess performance, update frequency, support arrangements, licensing costs and integration with existing systems. Security features need to be configured and maintained; default settings may not meet an organisation’s requirements. Regularly reviewing firewall rules and investigating alerts can help keep the deployment effective.

Is Untangle Firewall Right for Your Organisation?

Untangle firewall may be worth considering for organisations seeking a centrally managed platform that combines firewall controls with additional network security functions. Whether it is the right choice depends on the required features, the size of the network, available hardware, budget and the level of technical support needed.

Before committing, compare the current product offering with other firewall platforms, test it in a controlled environment where possible, and confirm that it meets your security and compliance requirements. A well-planned deployment, supported by ongoing monitoring and maintenance, is essential to getting value from any firewall solution.


Untangle Firewall FAQs: Features, Pricing, Setup and Suitability

  1. What is Untangle Firewall, and how does it work?
  2. What features does Untangle Firewall include?
  3. Is Untangle Firewall free to use?
  4. How do I install and configure Untangle Firewall?
  5. Is Untangle Firewall suitable for small businesses and home networks?

What is Untangle Firewall, and how does it work?

Untangle Firewall, now associated with Arista NG Firewall, is a network security platform that helps organisations control and monitor traffic between their network and the internet. It applies rules to allow or block connections and can provide additional tools—depending on the version and configuration—for tasks such as web filtering, intrusion prevention, application control and VPN access. Administrators manage these settings through a central interface, tailoring them to the organisation’s users, devices and security needs.

What features does Untangle Firewall include?

Untangle Firewall, also known as Arista NG Firewall, combines core firewall controls with a range of network security tools. Depending on the version and subscription, features may include intrusion prevention, web filtering, application control, VPN access, traffic monitoring and reporting. These tools help administrators manage network access, inspect traffic and investigate potential security events. Available features can vary, so check the current product documentation and licensing details before choosing a solution.

Is Untangle Firewall free to use?

Untangle Firewall may offer free or trial options, but the features available can depend on the product version, subscription and deployment type. Some advanced security tools or support services may require a paid licence. As plans and product names can change, check the current Arista NG Firewall pricing and licensing information before deploying it to confirm what is included.

How do I install and configure Untangle Firewall?

To install and configure Untangle Firewall, first check the current system requirements and download the appropriate installation image or prepare a supported appliance. Back up important settings, then install the software on the chosen device and connect its network interfaces to the internet and internal network as directed by the setup guide. Use the initial configuration wizard to set administrator credentials, network interfaces, IP settings and any required internet connection details. Once the firewall is online, configure and test rules, user access, VPN and any security or filtering features you need; then apply updates and review logs to confirm everything is working as intended. Exact steps can vary by product version and deployment, so follow the current official documentation and keep a recovery plan in case a configuration change interrupts access.

Is Untangle Firewall suitable for small businesses and home networks?

Yes, Untangle Firewall can be suitable for small businesses and home networks that need more control over traffic, web filtering, VPN access or security monitoring than a standard router provides. Its suitability depends on the features required, the hardware available and any licensing or support costs; setup and ongoing maintenance may also require some technical knowledge. For a simpler home network, a modern router’s built-in security features may be enough, while small businesses should assess their security and compliance needs before choosing a firewall.

SDN Security: Protecting the Software-Defined Network

Software-defined networking (SDN) changes how networks are managed. Rather than configuring every network device individually, SDN uses software to control and coordinate network behaviour. This can make networks more flexible and easier to manage, but it also introduces security considerations that organisations need to address.

Effective SDN security protects the network’s controllers, devices, applications and communications. It also helps ensure that network policies are applied consistently, even as infrastructure changes.

What is software-defined networking?

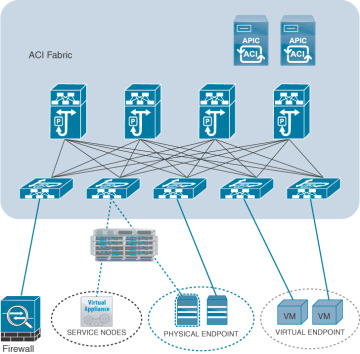
In a traditional network, control functions are distributed across routers and switches. SDN separates the network’s control plane, which decides how traffic should be handled, from its data plane, which forwards that traffic. A centralised or logically centralised SDN controller communicates with network devices and directs their behaviour.

Applications can interact with the controller through northbound interfaces, while the controller communicates with network devices through southbound interfaces. The exact architecture and protocols vary between SDN platforms, but the broad principle is the same: network behaviour is managed through software and policies.

Why does SDN security matter?

Centralised management can improve visibility and make it quicker to apply security policies across a network. For example, administrators may be able to isolate a compromised device or restrict access to a sensitive service without changing each switch manually.

However, the controller has significant influence over the network. If it is compromised, misconfigured or unavailable, an attacker or technical fault could affect many devices at once. SDN also relies on software, APIs and communication channels that may create new points of exposure. Security needs to be built into the architecture, rather than added only after deployment.

Common SDN security risks

  • Controller compromise: An attacker who gains access to the controller may be able to change network policies, redirect traffic or disrupt services.
  • Unauthorised access: Weak authentication, excessive privileges or poorly managed administrator accounts can expose controllers and management interfaces.
  • Insecure APIs: Vulnerabilities in northbound or southbound interfaces can allow unauthorised commands, data exposure or misuse of network functions.
  • Insecure communications: Traffic between controllers, applications and network devices could be intercepted or altered if it is not appropriately protected.
  • Misconfiguration: Incorrect policies can unintentionally allow traffic between systems that should be isolated, or block legitimate services.
  • Denial-of-service attacks: A flood of requests or network events may overwhelm a controller or the services it depends on.
  • Compromised applications or devices: Vulnerabilities in connected applications, switches, routers or virtual network functions can provide a route into the wider environment.
  • Limited visibility: Rapidly changing, virtualised networks can make it harder to identify unusual activity unless monitoring covers both the control and data planes.

Best practices for securing an SDN environment

Protect the controller

Treat SDN controllers as critical infrastructure. Place them in a restricted management environment, limit administrative access and apply security updates promptly. Use strong authentication, including multi-factor authentication where available, and assign permissions according to each user’s responsibilities. Avoid exposing management interfaces directly to untrusted networks.

Secure APIs and communications

Use authenticated and encrypted communication between controllers, applications and network devices wherever supported. Validate API inputs, manage credentials securely and disable interfaces or services that are not required. Review API permissions regularly, particularly when applications or integrations change.

Apply least privilege and separation of duties

Users, applications and devices should receive only the access they need. Separate administrative duties where practical, and use distinct accounts for routine tasks and privileged operations. This can limit the impact of a compromised account or an accidental change.

Segment the network

Use network segmentation to separate sensitive systems, management traffic and user workloads. Define clear rules for communication between segments and review them regularly. SDN can help automate segmentation, but the policies still need careful design and testing.

Monitor network activity

Collect and review logs from controllers, network devices and relevant applications. Monitor for unexpected policy changes, unusual administrative activity, abnormal traffic patterns and repeated authentication failures. Integrating SDN logs with security monitoring tools can help teams investigate events across the wider environment.

Test changes before deployment

Network policies can have far-reaching effects. Test changes in a controlled environment where possible, use staged roll-outs and keep a record of approved changes. Establish a clear process for reviewing, authorising and, if necessary, reversing policy updates.

Plan for resilience and recovery

Consider how the network will behave if a controller, link or supporting service becomes unavailable. Depending on the platform, resilience may involve controller redundancy, backups, recovery procedures and tested failover arrangements. Document how to restore service and practise the relevant procedures.

Assess the supply chain

SDN environments may depend on software from multiple suppliers, including controller platforms, applications and virtual network functions. Assess supplier security practices, keep an inventory of components and track relevant updates and vulnerabilities. Use trusted sources for software and verify that components are supported.

Building an SDN security strategy

There is no single configuration that suits every SDN deployment. A sound security strategy starts with an understanding of the network’s architecture, critical assets, data flows and operational requirements. From there, organisations can identify likely threats, set security objectives and decide how controls will be implemented and tested.

Security should be considered throughout the SDN lifecycle: during design, deployment, day-to-day operation and decommissioning. Regular reviews help ensure that policies remain appropriate as applications, users and network services change.

Conclusion

SDN can make networks more adaptable and improve the consistency of network management. Its centralised control and reliance on software also mean that controllers, APIs, communications and policies need strong protection. By applying least privilege, securing interfaces, monitoring activity, testing changes and planning for recovery, organisations can reduce risk and make SDN a more resilient part of their security architecture.


8 Essential Tips for Securing Software-Defined Networks (SDN)

  1. Secure the controller with strong authentication.
  2. Encrypt control-plane communications.
  3. Segment management and data networks.
  4. Apply least-privilege access controls.
  5. Keep SDN software and firmware patched.
  6. Monitor flows for unusual activity.
  7. Validate rules before deploying changes.
  8. Back up controller configurations regularly.

Secure the controller with strong authentication.

Secure the SDN controller with strong authentication to help prevent unauthorised access to a critical part of your network. Use unique accounts, strong passwords and multi-factor authentication where available, and avoid shared administrator credentials. Give each user only the permissions needed for their role, review access regularly and remove accounts promptly when they are no longer required. These measures can reduce the risk of an attacker taking control of network policies or disrupting services.

Encrypt control-plane communications.

Encrypt control-plane communications to protect instructions and status data exchanged between SDN controllers, network devices and applications. Encryption helps prevent attackers from intercepting or tampering with this traffic, which could otherwise expose sensitive information or lead to unauthorised network changes. Use secure, supported protocols, validate the identity of communicating endpoints and manage certificates and keys carefully, including renewing them before they expire.

Segment management and data networks.

Keep management traffic separate from the data network to reduce the risk of an attacker reaching SDN controllers and administrative interfaces through compromised user devices or services. Use dedicated network segments, restrict access to authorised systems and administrators, and apply firewall rules that allow only the connections required for management. Regularly review segmentation policies and monitor traffic between segments to spot unauthorised access or unexpected changes.

Apply least-privilege access controls.

Apply least-privilege access controls across your SDN environment by giving users, applications and devices only the permissions they need to perform their roles. Restrict access to controllers and management interfaces, use strong authentication and review privileges regularly, especially when responsibilities change. This limits the damage a compromised account or misconfigured application can cause and helps prevent unauthorised changes to network policies.

Keep SDN software and firmware patched.

Keep SDN software and firmware patched to protect controllers, switches, routers and related components from known vulnerabilities. Apply security updates promptly, following a controlled process that includes checking vendor guidance, testing changes where possible and keeping a recovery plan in place. Regular patching reduces the risk of attackers exploiting outdated systems to disrupt network services or gain unauthorised access.

Monitor flows for unusual activity.

Monitor network flows for unusual activity to help spot potential threats early. Establish a baseline of normal traffic between users, devices and services, then look for deviations such as unexpected connections, unusual data volumes, unfamiliar destinations or sudden changes in communication patterns. In an SDN environment, flow monitoring can provide valuable visibility across dynamically changing networks, helping security teams investigate suspicious behaviour and apply containment policies promptly. Tune alerts to reduce false positives, and review them regularly as network activity evolves.

Validate rules before deploying changes.

Validate SDN rules before deploying changes to ensure they work as intended and do not introduce security gaps or disrupt legitimate traffic. Test policies in a controlled environment where possible, check how they interact with existing rules, and obtain the appropriate approval before rolling them out. A staged deployment and a clear rollback plan can help limit the impact if an issue arises.

Back up controller configurations regularly.

Back up SDN controller configurations regularly so they can be restored if a controller fails, is compromised or a configuration change causes disruption. Store backups securely, restrict access and keep copies separate from the controller itself. Test the restoration process periodically, as a backup is only useful if it can be recovered successfully.

Untangle NG Firewall: An Overview

Untangle NG Firewall is a network security platform designed to help organisations monitor and protect the traffic passing through their networks. It combines traditional firewall controls with a collection of security and network-management tools, making it possible to manage several protections from one interface.

The product was developed by Untangle, which Arista Networks acquired in 2021. It is now commonly referred to as Arista NG Firewall. Product names, licensing and availability may change over time, so organisations considering it should check the current information from Arista before making a purchasing or migration decision.

How it works

NG Firewall is typically placed between an organisation’s internal network and its internet connection. Traffic passes through the appliance, where configured rules and security services can inspect it. The firewall can run on dedicated hardware or, depending on the version and deployment requirements, in a virtual environment.

A notable feature of the platform is its app-based design. Rather than presenting every capability as a separate product, it groups functions into applications that administrators can enable and configure to suit their network.

Key features

  • Firewall controls: Create rules to manage network traffic and restrict unwanted connections.
  • Intrusion prevention: Inspect traffic for activity associated with known attacks and suspicious behaviour.
  • Web filtering: Apply policies to web access, such as limiting access to selected categories or sites.
  • Malware protection: Use supported scanning tools to help identify threats in network traffic.
  • Virtual private networking: Provide secure remote access or connections between locations, subject to the available configuration and licence.
  • Reporting and monitoring: Review network activity and security events through dashboards and reports.
  • Traffic management: Apply bandwidth policies and manage how network resources are used.

Not every feature is necessarily included in every edition or subscription. Administrators should confirm which services are available, how they are licensed and what hardware or system resources they require.

Who might use it?

Untangle NG Firewall may suit small and medium-sized organisations that want a central point for managing internet access and network security. It can also be of interest to IT teams looking for a single interface for firewall rules, web policies, traffic visibility and related controls.

Suitability depends on the size and complexity of the network. Larger organisations may need to assess its high-availability options, central management capabilities, integration with existing security tools and performance under expected traffic loads. A trial or controlled pilot can help establish whether it meets operational requirements.

Benefits and considerations

The app-based approach can make it easier to enable the protections a network needs without deploying a separate appliance for every function. Centralised reporting may also help administrators understand what is happening on the network and investigate issues.

However, a firewall is only one part of a security programme. It needs careful configuration, regular updates and ongoing review. Administrators should also consider the impact of encrypted traffic inspection, privacy obligations, logging and data retention. As with any gateway security product, incorrect rules or an overloaded appliance can affect both protection and network performance.

Planning a deployment

Before installing NG Firewall, document the network layout, internet connection speed, number of users and the services that must remain accessible. Check the product’s current compatibility and sizing guidance, then plan how the appliance will fit into the network and how administrators will access it if a configuration change causes a problem.

After deployment, test key services, review alert and reporting settings, and establish a routine for updating the system and checking firewall rules. Keep a record of configuration changes and make sure there is a recovery plan, including backups where supported.

Conclusion

Untangle NG Firewall, now associated with the Arista NG Firewall name, brings firewalling and a range of network security tools together in a single platform. Its feature set and app-based design may be useful for organisations seeking consolidated network management. The best way to assess it is to compare its current capabilities, licensing, support and performance requirements with the needs of the network it is intended to protect.


7 Essential Tips for Securing Untangle NG Firewall

  1. Keep Untangle NG Firewall updated.
  2. Use strong, unique administrator passwords.
  3. Enable only the apps and features you need.
  4. Back up your configuration regularly.
  5. Review firewall rules and logs often.
  6. Test changes before applying them widely.
  7. Restrict admin access to trusted networks.

Keep Untangle NG Firewall updated.

Keep Untangle NG Firewall updated to ensure it has the latest security fixes, feature improvements and compatibility updates. Check for updates regularly, review the release notes before installing them, and schedule upgrades at a suitable time to minimise disruption. Before a major update, back up the configuration and confirm that you have a recovery plan in case anything goes wrong.

Use strong, unique administrator passwords.

Use a strong, unique password for every Untangle NG Firewall administrator account. A long passphrase made from several unrelated words can be easier to remember and harder to guess; avoid reusing passwords from other services or using predictable details. Store credentials securely in a reputable password manager, limit administrator access to people who need it, and enable multi-factor authentication if it is available in your setup. Regularly review accounts and remove access that is no longer required.

Enable only the apps and features you need.

Enable only the apps and features your network needs in Untangle NG Firewall. Each additional service can use system resources and may introduce settings that need monitoring, so a focused configuration can help maintain performance and make the firewall easier to manage. Review your requirements regularly and enable further features only when there is a clear need.

Back up your configuration regularly.

Back up your Untangle NG Firewall configuration regularly, especially after making significant changes to firewall rules, network settings or security applications. A recent backup can help you restore your setup more quickly if the appliance fails, an update causes problems or a configuration change interrupts network access. Store backup files securely, keep copies separate from the firewall itself, and check periodically that they’re available when needed.

Review firewall rules and logs often.

Review firewall rules and logs regularly to make sure your Untangle NG Firewall is protecting the network as intended. Remove outdated or overly broad rules, check that permitted traffic is still necessary, and investigate unusual activity or repeated blocked connections in the logs. Routine reviews can help uncover misconfigurations and potential threats before they cause wider problems.

Test changes before applying them widely.

Before rolling out a new rule or configuration across your network, test it on a small, controlled group of users or devices. This helps you spot blocked services, unexpected alerts or performance issues without disrupting everyone’s access. Once the change has been checked and any problems resolved, apply it more widely and continue monitoring the firewall’s logs and reports.

Restrict admin access to trusted networks.

Restricting administrator access to trusted networks helps reduce the risk of unauthorised changes to your Untangle NG Firewall. Configure management access so it is available only from designated internal networks, secure administrator accounts with strong, unique passwords and multi-factor authentication where supported, and avoid exposing the management interface directly to the internet. Review access rules regularly and remove any networks or accounts that are no longer needed.

NetworkMiner: A Practical Guide to Network Forensics

NetworkMiner is a network forensic analysis tool designed to help investigators examine traffic captured from a network. Rather than focusing primarily on displaying individual packets, it organises captured data into useful information about hosts, connections and transferred files. This can make it easier to investigate what happened during a network incident.

What is NetworkMiner?

Developed by Netresec, NetworkMiner is used to analyse packet capture files, commonly known as PCAP files. It can identify hosts and network sessions, and may extract artefacts such as files, images, certificates and credentials when they are present in supported traffic. The results depend on the protocols used, the quality of the capture and whether the relevant information is visible.

NetworkMiner is often described as a passive network forensic analysis tool. It examines traffic that has already been captured, rather than actively interacting with the systems being investigated. This makes it useful for reviewing a saved capture after a security alert or suspected intrusion.

What can NetworkMiner help with?

  • Host identification: View systems observed in the capture and details that may help distinguish them.
  • Session analysis: Review communications between hosts and the services involved.
  • File extraction: Recover files transferred in supported protocols, where the capture contains enough data.
  • Artefact review: Examine other available evidence, such as images, certificates or credentials exposed in unencrypted traffic.
  • Incident investigation: Build a clearer picture of network activity for security monitoring, troubleshooting or digital forensics.

How does it fit into an investigation?

A typical workflow begins with collecting network traffic using an authorised capture process. The resulting PCAP file can then be opened in NetworkMiner for an initial overview of hosts, sessions and potential artefacts. Investigators can use those findings to decide which traffic needs closer examination.

NetworkMiner can complement packet analysers such as Wireshark. Its host-centred presentation and artefact extraction can make certain investigative tasks quicker, while a packet analyser offers detailed control over individual packets and protocol fields. The tools serve related but different purposes, so using them together can be helpful.

Important limitations

NetworkMiner can only analyse information available in the capture. If traffic was missed, the capture began too late, or the relevant content is encrypted, the tool may not be able to recover the details an investigator is looking for. Modern encryption often prevents the contents of a connection from being read, although some connection metadata may still be visible.

Results also need to be interpreted carefully. An extracted artefact or identified host is evidence to investigate, not necessarily proof of malicious activity on its own. Good practice includes preserving the original capture, documenting how it was obtained, recording analysis steps and corroborating findings with other evidence.

Choosing a version

NetworkMiner is available in different editions, including a free Community Edition and a commercial Professional Edition. Features and licensing can change, so check the developer’s website for current details before choosing a version. Organisations should also review the licence terms and test the software with representative captures before relying on it in operational workflows.

Use it responsibly

Network captures can contain sensitive information, including personal data and confidential business communications. Only capture or analyse traffic when authorised, follow applicable privacy and data-protection requirements, and restrict access to capture files and extracted artefacts.

Conclusion

NetworkMiner is a useful option for turning packet captures into an organised view of network activity. Its ability to group information around hosts and identify recoverable artefacts can support incident response and forensic investigations. Like any analysis tool, it works best when used alongside sound evidence-handling practices and a clear understanding of what the capture can—and cannot—show.


8 Tips for Safe and Effective Network Analysis with NetworkMiner

  1. Use NetworkMiner to analyse PCAP files without altering the original capture.
  2. Capture only traffic you are authorised to inspect.
  3. Check the Hosts tab to identify systems and their network activity.
  4. Review the Files tab to recover files observed in the capture.
  5. Use the DNS tab to spot queried domains and potential anomalies.
  6. Treat extracted credentials as sensitive and store them securely.
  7. Compare findings with other tools before drawing conclusions.
  8. Keep captures and reports protected, as they may contain personal data.

Use NetworkMiner to analyse PCAP files without altering the original capture.

Use NetworkMiner to examine PCAP files while keeping the original capture intact. Analyse a working copy where possible, store the source file securely and record the steps taken during your investigation. This helps preserve the evidence for later review and makes your findings easier to verify.

Capture only traffic you are authorised to inspect.

Capture only traffic you are authorised to inspect. NetworkMiner can reveal sensitive details from network traffic, so only collect or analyse data when you have clear permission to do so. Follow your organisation’s policies and applicable privacy and data-protection requirements, and store capture files securely with access limited to authorised people.

Check the Hosts tab to identify systems and their network activity.

Check the Hosts tab in NetworkMiner to see which systems appear in the capture and review their associated network activity. This can help you quickly identify relevant devices, understand which hosts communicated and decide where to focus your investigation. Remember that the information shown depends on the traffic captured, so treat it as a starting point and verify important findings against the underlying evidence.

Review the Files tab to recover files observed in the capture.

Review the Files tab in NetworkMiner to see files identified in the network capture. Where the traffic contains enough data and the transfer uses a supported protocol, you may be able to recover files for further analysis. Check the file details and related session carefully, and remember that encrypted, incomplete or unsupported traffic may prevent recovery.

Use the DNS tab to spot queried domains and potential anomalies.

Use NetworkMiner’s DNS tab to review the domains queried in a capture and spot anything that looks out of place. Unfamiliar or misspelt domain names, unexpected top-level domains, or repeated queries to a single host may warrant closer investigation. Treat these as clues rather than proof of malicious activity, and check them against the surrounding traffic and other available evidence.

Treat extracted credentials as sensitive and store them securely.

Treat any credentials extracted with NetworkMiner as highly sensitive information. They may provide access to user accounts, systems or services, so avoid sharing them unnecessarily and never include them in reports or screenshots without appropriate redaction. Store them only in an approved, access-controlled location, protect them with encryption where possible, and follow your organisation’s retention and disposal policies. If a credential may have been exposed or compromised, notify the relevant security team and arrange for it to be changed.

Compare findings with other tools before drawing conclusions.

Compare NetworkMiner’s findings with evidence from other tools before drawing conclusions. Cross-check hosts, sessions and extracted artefacts against packet-level analysis in tools such as Wireshark, as well as relevant logs and endpoint data. This can help confirm that an observation is accurate, provide useful context and reduce the risk of treating an incomplete or misleading result as proof of malicious activity.

Keep captures and reports protected, as they may contain personal data.

Network captures and reports can contain personal data, credentials and details of private communications, so treat them as sensitive information. Store them in access-controlled locations, share them only with authorised people and use encryption where appropriate. Keep them only for as long as necessary, following your organisation’s retention and data-protection policies, and securely delete them when they are no longer needed.

Windows Defender Firewall: What It Does and How to Use It

Windows Defender Firewall is a security feature built into Windows that helps protect a computer from unwanted network traffic. It monitors connections and applies rules to decide which traffic is allowed through. By limiting unauthorised access, it can help reduce the risk of attacks and unwanted communication with your device.

In newer versions of Windows, the feature is generally called Microsoft Defender Firewall. It is included with Windows and works alongside other security measures, such as Microsoft Defender Antivirus, but the firewall and antivirus have different jobs.

How the firewall works

A firewall checks network traffic against a set of rules. These rules can allow or block connections based on factors such as the application involved, the type of network, and whether the connection is incoming or outgoing.

  • Inbound traffic is data coming into your computer from another device or the internet. Blocking unexpected inbound connections helps prevent other devices from reaching services on your PC.
  • Outbound traffic is data leaving your computer. Windows Firewall also supports rules for controlling outbound connections, although its default configuration is generally designed to allow normal outgoing activity unless a rule says otherwise.

When an app needs to communicate across a network, Windows may ask whether to allow it. The choice can depend on the network profile in use, so it is worth checking that the app and network are recognised before granting access.

Network profiles: domain, private and public

Windows uses network profiles to apply different firewall settings in different situations:

  • Domain: Used when a device is connected to a network managed by an organisation, such as a workplace domain.
  • Private: Intended for trusted networks, such as a home network. Devices may be able to discover one another, depending on the settings and services enabled.
  • Public: Intended for untrusted networks, such as Wi-Fi in a café, hotel or airport. This profile applies stricter protections and is usually the safer choice for unfamiliar networks.

Windows may ask whether a newly detected network should be treated as public or private. Choose the profile that reflects how much you trust the network. A public network should not be marked private simply to make file sharing or device discovery easier.

Checking firewall status

To check the firewall in Windows 11, open Settings, select Privacy & security, then Windows Security. Choose Firewall & network protection to view the status of the available network profiles and open the related settings.

The same area can also be opened by searching for Windows Security from the Start menu. The wording and layout may vary slightly between Windows versions.

Allowing an app through the firewall

If a trusted app cannot connect, it may need permission to communicate through the firewall. Before changing anything, confirm that the app is legitimate and that the connection is genuinely required.

  1. Open Windows Security and select Firewall & network protection.
  2. Choose Allow an app through firewall.
  3. Select Change settings if prompted for administrator permission.
  4. Find the app and allow it on the appropriate network profile. If it is not listed, use the option to add another app only when you know which programme you are approving.

Allowing an app through the firewall creates an exception. Avoid granting access on every profile unless it is necessary. In particular, an app that needs access on a trusted home network may not need the same access on public Wi-Fi.

Creating or reviewing firewall rules

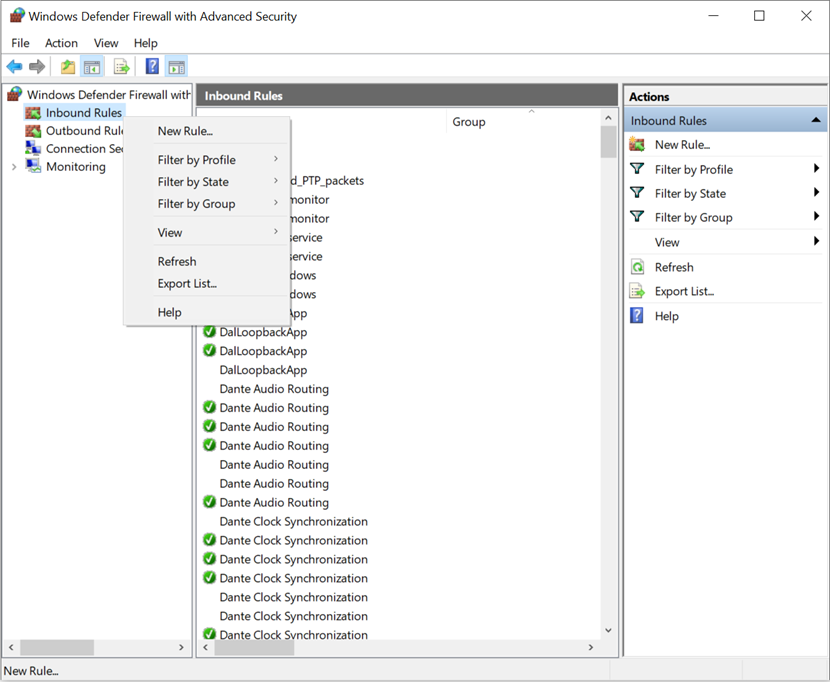
Windows includes Windows Defender Firewall with Advanced Security, which provides more detailed controls for inbound and outbound rules. It is available by searching for its name in the Start menu or through Windows administrative tools.

Advanced rules can be useful for managing specific applications, ports, protocols and network profiles. They can also be used by IT administrators to apply consistent policies across managed devices. However, changing rules without understanding their effect can disrupt apps or weaken security. If a computer is managed by an employer or school, check with the administrator before altering its firewall configuration.

Should you turn the firewall off?

In most cases, the firewall should remain switched on for every network profile. Turning it off removes an important layer of protection, particularly on public networks. If a connection problem appears to be caused by the firewall, it is usually safer to investigate the relevant app or rule than to disable the firewall altogether.

Do not run multiple firewalls that are not designed to work together. Some third-party security products manage the firewall themselves, and Windows may show a different status when another provider is active. Check the security software’s guidance before changing settings.

Good practice for staying protected

  • Keep Windows and your applications up to date.
  • Leave Microsoft Defender Firewall enabled unless a trusted administrator advises otherwise.
  • Use the public network profile for unfamiliar Wi-Fi networks.
  • Allow only trusted apps, and only on the profiles they need.
  • Review firewall alerts and settings rather than dismissing them automatically.
  • Use additional protections, such as strong passwords and multi-factor authentication, where available.

In summary

Windows Defender Firewall helps control network traffic to and from a Windows device. Its built-in protection is suitable for many home and business users when it is enabled and kept at its default settings. Understanding network profiles and app exceptions can help you resolve connection issues without opening more access than necessary.


8 Tips for Using Microsoft Defender Firewall Safely

  1. Keep Microsoft Defender Firewall turned on for all network profiles.
  2. Use private networks for trusted home or work connections.
  3. Treat public Wi‑Fi as a public network.
  4. Allow apps through the firewall only when necessary.
  5. Remove permissions for apps you no longer use.
  6. Avoid turning off the firewall to fix connection problems.
  7. Check firewall notifications before allowing access.
  8. Keep Windows updated to receive the latest security fixes.

Keep Microsoft Defender Firewall turned on for all network profiles.

Keep Microsoft Defender Firewall turned on for all network profiles to help protect your device from unauthorised network connections, wherever you’re connected. This is especially important on public Wi-Fi, such as in cafés, hotels or airports, where other users may be unfamiliar or untrusted. If an app or service has connection problems, check its firewall permissions rather than switching the firewall off.

Use private networks for trusted home or work connections.

Set a network to private only when it is one you trust, such as your home Wi-Fi or a secure workplace network. This profile can allow your computer to be discoverable by other devices and support features such as file and printer sharing. For unfamiliar connections, including public Wi-Fi in cafés or hotels, choose the public profile instead to keep your device less visible and apply stricter protection.

Treat public Wi‑Fi as a public network.

When connecting to public Wi-Fi in places such as cafés, hotels or airports, set the network profile to Public in Windows. This applies stricter sharing and discovery settings, helping limit how visible your device is to other people on the same network. Avoid switching to a Private profile just to make a connection work, and only allow apps through the firewall when you trust them and know they need network access.

Allow apps through the firewall only when necessary.

Allow apps through Windows Defender Firewall only when necessary, and only if you trust the app and understand why it needs network access. Each exception creates a route for communication with your device, so avoid granting access on every network profile by default. Choose only the profiles the app needs, and remove permissions you no longer use.

Remove permissions for apps you no longer use.

Review the apps allowed through Windows Defender Firewall from time to time and remove permissions for programmes you no longer use. An outdated or unnecessary exception may leave a route for network access that the app no longer needs. In Windows Security, open Firewall & network protection, select Allow an app through firewall, then review the list and remove any permissions that are no longer required. If your device is managed by work or school, check with your IT administrator before changing firewall settings.

Avoid turning off the firewall to fix connection problems.

Avoid turning off Windows Defender Firewall to fix connection problems, as this removes an important layer of protection and may leave your device exposed to unwanted network traffic. Instead, check whether the correct network profile is selected and review the firewall rules or app permissions for the programme experiencing difficulties. Only allow access for trusted apps, and seek help from your IT administrator if your device is managed by work or school.

Check firewall notifications before allowing access.

Before allowing an app through Windows Defender Firewall, read the notification carefully and check that you recognise both the app and why it needs network access. Pay attention to the network type: an app may be suitable for a trusted private network but not for public Wi-Fi. If the request is unexpected or you are unsure, deny access for now and verify the app with its developer or your IT administrator.

Keep Windows updated to receive the latest security fixes.

Keep Windows up to date so your device receives the latest security fixes and improvements. These updates can address vulnerabilities that attackers might exploit, helping Windows Defender Firewall work as part of a stronger overall security set-up. Enable automatic updates where possible, and restart your device when prompted to complete the installation.