Enhancing Data Protection: The Ultimate Information Security Solution Guide

The Importance of Information Security Solutions

The Importance of Information Security Solutions

In today’s digital age, where data breaches and cyber-attacks are becoming increasingly common, the need for robust information security solutions has never been more critical. Businesses of all sizes and industries are facing constant threats to their sensitive information, making it essential to invest in comprehensive security measures.

Information security solutions encompass a range of technologies, processes, and practices designed to protect data from unauthorised access, disclosure, disruption, modification or destruction. These solutions play a vital role in safeguarding confidential information, maintaining the integrity of systems, and ensuring business continuity.

Key Components of Information Security Solutions:

  • Firewalls: Firewalls act as a barrier between a trusted internal network and untrusted external networks, monitoring and controlling incoming and outgoing network traffic based on predetermined security rules.
  • Encryption: Encryption converts data into a code to prevent unauthorised access. It ensures that even if data is intercepted, it remains unreadable without the decryption key.
  • Antivirus Software: Antivirus software detects and removes malicious software such as viruses, worms, and trojans from computer systems to prevent damage and data loss.
  • Intrusion Detection Systems (IDS): IDS monitor network traffic for suspicious activity or policy violations. They alert IT administrators when potential threats are detected.
  • Access Control Systems: Access control systems regulate who can access certain resources within an organisation. This includes user authentication mechanisms like passwords, biometrics, and multi-factor authentication.

The Benefits of Implementing Information Security Solutions:

By investing in information security solutions, businesses can enjoy a myriad of benefits:

  • Data Protection: Protect sensitive data from unauthorised access or theft.
  • Compliance: Ensure compliance with industry regulations and standards regarding data protection.
  • Business Continuity: Minimise downtime due to cyber incidents by safeguarding critical systems and information.
  • Credibility: Build trust with customers by demonstrating a commitment to protecting their data.
  • Cost Savings: Avoid financial losses associated with data breaches by proactively securing systems.

In conclusion, information security solutions are indispensable in today’s digital landscape. By implementing robust security measures tailored to their specific needs, businesses can mitigate risks, protect valuable assets, and maintain a competitive edge in an increasingly connected world.


8 Key Benefits of Implementing an Information Security Solution

  1. Protect sensitive data from unauthorised access
  2. Prevent costly data breaches and cyber-attacks
  3. Ensure compliance with industry regulations and standards
  4. Maintain business continuity by safeguarding critical systems
  5. Enhance customer trust and credibility
  6. Mitigate financial losses associated with security incidents
  7. Improve overall system performance and reliability
  8. Stay ahead of evolving cybersecurity threats


Challenges and Drawbacks of Implementing Information Security Solutions

  1. Costly implementation and maintenance of security solutions can strain a company’s budget.
  2. Complexity of security measures may require specialised knowledge and training for effective deployment.
  3. Over-reliance on technology-based solutions can lead to a false sense of security, overlooking human error and social engineering tactics.
  4. Integration challenges may arise when trying to implement multiple security solutions across different systems and platforms.
  5. Security solutions can sometimes cause performance issues or slow down system processes, impacting productivity.
  6. Constantly evolving threats mean that security solutions need regular updates and upgrades to remain effective, adding to the workload of IT teams.
  7. Intrusive security measures such as strict access controls can hinder user convenience and workflow efficiency.

Protect sensitive data from unauthorised access

One of the key advantages of implementing information security solutions is the ability to protect sensitive data from unauthorised access. By utilising encryption, access control systems, and other security measures, organisations can safeguard confidential information such as customer records, financial data, and intellectual property from cyber threats. This proactive approach not only helps prevent data breaches and theft but also instils trust among stakeholders by demonstrating a commitment to maintaining the privacy and integrity of sensitive data.

Prevent costly data breaches and cyber-attacks

One of the key advantages of implementing information security solutions is the ability to prevent costly data breaches and cyber-attacks. By proactively securing sensitive data and systems, businesses can significantly reduce the risk of falling victim to malicious activities that could result in financial losses, reputational damage, and legal implications. Investing in robust security measures not only protects valuable assets but also ensures business continuity by mitigating the disruptive impact of cyber incidents. Prioritising information security is essential in safeguarding against potential threats and maintaining the trust of customers and stakeholders in an increasingly digital environment.

Ensure compliance with industry regulations and standards

Ensuring compliance with industry regulations and standards is a crucial benefit of information security solutions. By implementing robust security measures that align with regulatory requirements, businesses can demonstrate their commitment to data protection and privacy. Compliance not only helps in avoiding costly fines and legal consequences but also builds trust with customers and stakeholders. Adhering to industry standards ensures that sensitive information is handled responsibly, fostering a culture of transparency and accountability within the organisation.

Maintain business continuity by safeguarding critical systems

The implementation of information security solutions plays a crucial role in maintaining business continuity by safeguarding critical systems. By ensuring the integrity and availability of essential IT infrastructure, businesses can mitigate the risk of downtime caused by cyber incidents such as data breaches or system failures. This proactive approach not only protects valuable assets and sensitive information but also helps organisations to operate smoothly and efficiently, even in the face of potential threats. The ability to keep critical systems secure and operational is paramount for sustaining business operations and meeting customer expectations in today’s digital landscape.

Enhance customer trust and credibility

Incorporating information security solutions can significantly enhance customer trust and credibility for businesses. By demonstrating a commitment to safeguarding sensitive data through robust security measures, organisations instil confidence in their customers that their information is being handled responsibly and securely. This proactive approach not only helps build trust with existing customers but also attracts new ones who prioritise data protection and privacy. Ultimately, investing in information security solutions not only protects the business from potential breaches but also reinforces its reputation as a trustworthy and reliable entity in the eyes of its clientele.

Mitigate financial losses associated with security incidents

Implementing robust information security solutions can significantly mitigate financial losses associated with security incidents. By proactively safeguarding sensitive data and critical systems, businesses can reduce the risk of costly breaches, cyber-attacks, or data theft. Investing in technologies such as firewalls, encryption, and intrusion detection systems not only protects valuable assets but also helps avoid the substantial financial repercussions that often accompany security breaches. Effective information security measures can save organisations from the devastating impact of monetary losses, legal liabilities, reputational damage, and operational disruptions caused by security incidents.

Improve overall system performance and reliability

Implementing information security solutions can significantly enhance overall system performance and reliability. By implementing measures such as firewalls, intrusion detection systems, and regular security updates, organisations can reduce the risk of cyber threats that may compromise system integrity. This proactive approach not only safeguards sensitive data but also ensures that systems operate smoothly without interruptions caused by malicious activities. Improved system performance leads to enhanced efficiency and productivity, allowing businesses to focus on their core operations with confidence in the reliability of their IT infrastructure.

Stay ahead of evolving cybersecurity threats

In today’s rapidly evolving digital landscape, one of the key advantages of implementing information security solutions is the ability to stay ahead of constantly changing cybersecurity threats. By proactively investing in advanced security measures such as threat detection systems, regular vulnerability assessments, and employee training programmes, organisations can effectively identify and mitigate emerging risks before they escalate into full-fledged cyber-attacks. This proactive approach not only enhances the overall resilience of the IT infrastructure but also ensures that businesses are well-prepared to tackle new and sophisticated threats in real-time, safeguarding sensitive data and maintaining operational continuity.

Costly implementation and maintenance of security solutions can strain a company’s budget.

The implementation and maintenance of information security solutions can present a significant challenge for companies due to the associated costs. Investing in robust security measures often requires a substantial financial commitment, which can strain a company’s budget, particularly for small and medium-sized enterprises. From purchasing hardware and software to training staff and conducting regular updates, the expenses involved in maintaining effective security solutions can quickly add up. Balancing the need for comprehensive protection with budgetary constraints is a delicate task that many organisations face, highlighting the conundrum of managing the financial implications of safeguarding sensitive information in today’s cyber-threat landscape.

Complexity of security measures may require specialised knowledge and training for effective deployment.

The complexity of security measures within information security solutions can present a significant challenge, as their effective deployment often necessitates specialised knowledge and training. Managing intricate technologies such as firewalls, encryption protocols, and intrusion detection systems requires a deep understanding of cybersecurity principles and best practices. Without the appropriate expertise, organisations may struggle to configure these tools optimally, leaving their systems vulnerable to potential threats. Investing in ongoing training and upskilling for IT professionals is crucial to ensure that security measures are implemented correctly and maintained effectively to safeguard valuable data assets.

Over-reliance on technology-based solutions can lead to a false sense of security, overlooking human error and social engineering tactics.

An inherent con of information security solutions lies in the potential for organisations to develop an over-reliance on technology-based measures, inadvertently fostering a false sense of security. By placing excessive trust in automated systems and tools, businesses may overlook the critical factors of human error and social engineering tactics. Despite the sophistication of technological defences, the weakest link often remains human behaviour, making employees susceptible to manipulation and exploitation by cybercriminals. This oversight highlights the importance of integrating comprehensive training programmes and awareness initiatives alongside technological solutions to fortify overall information security posture effectively.

Integration challenges may arise when trying to implement multiple security solutions across different systems and platforms.

Integrating multiple security solutions across diverse systems and platforms can present a significant challenge in the realm of information security. The complexity arises from ensuring seamless communication and compatibility between various tools, each designed to address specific threats or vulnerabilities. Coordinating the deployment of these solutions while maintaining system functionality and performance can be a daunting task for organisations. Misconfigurations or conflicts during integration may lead to gaps in security coverage, leaving potential vulnerabilities exposed. Overcoming these integration challenges requires meticulous planning, expertise, and ongoing maintenance to ensure a cohesive and effective security posture across the entire IT infrastructure.

Security solutions can sometimes cause performance issues or slow down system processes, impacting productivity.

Security solutions, while essential for safeguarding sensitive information, can inadvertently introduce performance issues that hinder system processes and productivity. The additional layers of security protocols, encryption processes, and monitoring mechanisms implemented by these solutions can sometimes lead to delays in data processing and system responsiveness. This slowdown in performance may frustrate users, disrupt workflow efficiency, and potentially impact overall productivity within an organisation. Striking a balance between robust security measures and maintaining optimal system performance is crucial to ensure that information security solutions do not impede daily operations.

Constantly evolving threats mean that security solutions need regular updates and upgrades to remain effective, adding to the workload of IT teams.

In the realm of information security solutions, a significant drawback arises from the ever-evolving nature of cyber threats. The continuous emergence of new and sophisticated attack methods necessitates regular updates and upgrades to security measures in order to effectively combat these evolving risks. This ongoing need for maintenance adds a considerable workload to IT teams, requiring them to stay vigilant, proactive, and dedicated to keeping security systems up-to-date and resilient against the latest threats. Balancing the demands of day-to-day operations with the imperative task of maintaining robust security measures can place a strain on IT resources and personnel, highlighting a challenging aspect of managing information security in today’s dynamic threat landscape.

Intrusive security measures such as strict access controls can hinder user convenience and workflow efficiency.

Intrusive security measures, such as implementing strict access controls, can present a significant con in information security solutions by potentially impeding user convenience and workflow efficiency. While these measures are essential for safeguarding sensitive data and preventing unauthorised access, overly restrictive access controls may create barriers for users, leading to frustration and hindering productivity. Balancing robust security protocols with user-friendly practices is crucial to ensure that information remains protected without compromising the usability and efficiency of daily operations within an organisation.

The Benefits of SailPoint Single Sign-On for Enhanced Security and User Experience

In today’s digital age, where multiple applications and systems are integral to daily business operations, managing user access efficiently and securely is paramount. This is where SailPoint Single Sign-On (SSO) comes into play, offering a comprehensive solution that simplifies access management while bolstering security measures.

Streamlined User Experience

SailPoint SSO enables users to access multiple applications and systems with just one set of login credentials. This eliminates the need to remember numerous passwords, leading to a more streamlined and user-friendly experience. With SSO, users can seamlessly navigate between different platforms without the hassle of repeated logins, ultimately boosting productivity.

Enhanced Security Measures

Security breaches and data leaks are significant concerns for organisations of all sizes. SailPoint SSO enhances security by centralising user authentication processes. By consolidating access control into a single system, SSO reduces the risk of password-related vulnerabilities and unauthorised access. Additionally, administrators can implement multi-factor authentication and other advanced security measures to fortify the authentication process further.

Improved Compliance Management

Compliance with industry regulations such as GDPR, HIPAA, or PCI-DSS is non-negotiable for many businesses. SailPoint SSO simplifies compliance management by providing detailed audit trails and reporting capabilities. Organisations can easily track user activities across various applications, ensuring adherence to regulatory requirements and internal policies.

Cost-Efficiency and Scalability

Implementing SailPoint SSO can lead to cost savings in the long run. By reducing password-related helpdesk requests and minimising the risk of security incidents, organisations can lower operational costs associated with access management. Furthermore, as businesses grow and evolve, SailPoint SSO offers scalability to accommodate changing user needs without compromising security or efficiency.

Conclusion

SailPoint Single Sign-On is a powerful solution that not only enhances user experience but also strengthens security measures within an organisation. By streamlining access management processes, improving compliance management, and offering cost-efficient scalability, SailPoint SSO empowers businesses to navigate the complexities of modern IT environments with confidence.

Embrace the future of secure access management with SailPoint Single Sign-On.


Top 7 Tips for Optimising SailPoint Single Sign-On Security and Efficiency

  1. Ensure proper configuration of user authentication methods.
  2. Regularly review and update access policies and permissions.
  3. Implement multi-factor authentication for added security.
  4. Monitor user activities and access logs for any suspicious behaviour.
  5. Integrate SailPoint with other identity management systems for seamless operations.
  6. Provide adequate training to users on how to use Single Sign-On effectively.
  7. Perform regular audits to ensure compliance with security standards.

Ensure proper configuration of user authentication methods.

To maximise the effectiveness of SailPoint Single Sign-On, it is crucial to ensure the proper configuration of user authentication methods. By carefully setting up authentication protocols such as multi-factor authentication, biometric verification, or one-time passwords, organisations can significantly enhance the security of their access management processes. Properly configured user authentication methods not only strengthen the overall security posture but also provide users with a seamless and secure login experience across various applications and systems.

Regularly review and update access policies and permissions.

To ensure the effectiveness of SailPoint Single Sign-On, it is crucial to regularly review and update access policies and permissions. By conducting routine audits of user access rights, organisations can identify and address any discrepancies or potential security risks promptly. Updating access policies in line with changing business requirements and employee roles helps maintain a secure and efficient authentication process. This proactive approach not only enhances data protection but also ensures that users have the appropriate level of access to perform their roles effectively within the system.

Implement multi-factor authentication for added security.

Enhance the security of your SailPoint Single Sign-On implementation by incorporating multi-factor authentication. By requiring users to provide multiple forms of verification before accessing applications and systems, such as a password combined with a unique code sent to their mobile device, you significantly reduce the risk of unauthorised access and data breaches. Multi-factor authentication adds an extra layer of protection to sensitive information, ensuring that only authorised individuals can gain entry, thereby bolstering the overall security posture of your organisation.

Monitor user activities and access logs for any suspicious behaviour.

Monitoring user activities and access logs for any suspicious behaviour is a crucial tip when utilising SailPoint Single Sign-On. By keeping a close eye on user interactions within the system and regularly reviewing access logs, organisations can quickly identify any anomalies or potential security threats. Detecting unusual patterns or unauthorised access attempts early on allows for prompt intervention, mitigating the risk of data breaches and ensuring the integrity of the IT environment. Proactive monitoring not only enhances security but also demonstrates a commitment to maintaining a robust defence against cyber threats in today’s digital landscape.

Integrate SailPoint with other identity management systems for seamless operations.

To maximise the efficiency and effectiveness of SailPoint Single Sign-On, it is highly recommended to integrate SailPoint with other identity management systems. By seamlessly connecting SailPoint with existing identity management solutions, organisations can achieve a unified and cohesive approach to access management. This integration facilitates streamlined operations, enhances user experience, and strengthens security measures by leveraging the combined capabilities of different systems. Ultimately, integrating SailPoint with other identity management systems paves the way for a seamless and comprehensive access management strategy that optimises productivity and fortifies data protection across the organisation.

Provide adequate training to users on how to use Single Sign-On effectively.

To maximise the benefits of SailPoint Single Sign-On, it is crucial to provide users with adequate training on how to utilise the system effectively. By offering comprehensive training sessions, organisations can ensure that users understand the functionality of SSO, how to navigate between applications seamlessly, and best practices for maintaining security. Empowering users with the knowledge and skills to leverage SailPoint SSO not only enhances their user experience but also contributes to a more secure and efficient access management environment overall.

Perform regular audits to ensure compliance with security standards.

Performing regular audits is a crucial aspect of maintaining compliance with security standards when utilising SailPoint Single Sign-On. These audits help organisations to assess the effectiveness of their access management policies, identify any potential vulnerabilities or non-compliance issues, and take proactive measures to address them. By conducting frequent audits, businesses can ensure that their SailPoint SSO implementation remains robust, secure, and aligned with industry best practices, ultimately enhancing overall security posture and reducing the risk of data breaches.

The Power of Enablon GRC: Streamlining Governance, Risk, and Compliance

In today’s complex business landscape, organisations face a myriad of challenges when it comes to managing governance, risk, and compliance (GRC) requirements. Ensuring regulatory compliance, mitigating risks, and maintaining operational efficiency are crucial for sustainable business success. This is where Enablon GRC comes into play as a comprehensive solution to streamline and enhance GRC processes.

What is Enablon GRC?

Enablon GRC is a leading software platform that empowers organisations to effectively manage their GRC initiatives in a unified manner. By integrating governance, risk management, and compliance functions into a single platform, Enablon GRC enables businesses to centralise their processes, data, and reporting for improved visibility and control.

The Benefits of Enablon GRC

Enablon GRC offers a wide range of benefits that help organisations optimise their GRC activities:

  • Centralised Data Management: By consolidating all GRC-related information in one place, Enablon GRC eliminates data silos and provides a holistic view of risks and compliance status.
  • Risk Mitigation: The platform facilitates proactive risk identification and assessment, enabling organisations to implement mitigation strategies effectively.
  • Compliance Automation: With automated workflows and monitoring capabilities, Enablon GRC simplifies compliance management processes and ensures adherence to regulations.
  • Reporting and Analytics: Enablon GRC offers robust reporting tools that enable stakeholders to generate customised reports on key performance indicators (KPIs) and trends for informed decision-making.
  • Audit Trail Transparency: The platform maintains an audit trail of all activities within the system, enhancing accountability and transparency across the organisation.

Use Cases of Enablon GRC

Organisations across various industries can leverage Enablon GRC to address specific GRC challenges:

  • Financial Services: Financial institutions can use Enablon GRC to ensure regulatory compliance with stringent industry standards such as Basel III or GDPR.
  • Healthcare: Healthcare providers can utilise the platform to manage data privacy regulations like HIPAA while enhancing patient safety through effective risk management.
  • Manufacturing: Manufacturing companies can streamline environmental health and safety (EHS) compliance efforts with Enablon GRC’s EHS management capabilities.

The Future of Enablon GRC

As regulatory requirements continue to evolve and businesses face increasing scrutiny over their operations, the role of Enablon GRC will become even more critical. The platform’s adaptability and scalability make it well-positioned to meet the changing needs of organisations seeking robust GRC solutions in an ever-changing business environment.

In conclusion, Enablon GRC stands as a powerful tool for organisations looking to enhance their governance, risk management, and compliance practices. By leveraging its capabilities, businesses can navigate the complexities of the modern regulatory landscape with confidence and efficiency.


Understanding Enablon GRC: Key Features, Benefits, and Customisation for Governance, Risk, and Compliance

  1. What is Enablon GRC and what does it stand for?
  2. How can Enablon GRC help streamline governance, risk, and compliance processes?
  3. What are the key benefits of implementing Enablon GRC in an organisation?
  4. Is Enablon GRC suitable for businesses in regulated industries such as finance and healthcare?
  5. Can Enablon GRC be customised to meet specific GRC requirements of different organisations?

What is Enablon GRC and what does it stand for?

Enablon GRC is a sophisticated software platform designed to streamline governance, risk management, and compliance processes within organisations. The acronym “GRC” stands for Governance, Risk, and Compliance, representing the core functions that Enablon GRC integrates and enhances. By centralising data, automating workflows, and providing robust reporting capabilities, Enablon GRC empowers businesses to effectively manage regulatory compliance, mitigate risks, and maintain operational efficiency. This comprehensive solution offers a holistic approach to GRC management, enabling organisations to achieve greater visibility and control over their governance practices, risk exposure, and compliance adherence.

How can Enablon GRC help streamline governance, risk, and compliance processes?

Enablon GRC offers a comprehensive solution to streamline governance, risk, and compliance processes by centralising and integrating key functions into a single platform. Through its centralised data management capabilities, Enablon GRC eliminates silos and provides a unified view of risks and compliance status across the organisation. The platform facilitates proactive risk identification and assessment, enabling businesses to implement effective mitigation strategies. With automation features for compliance workflows and monitoring, Enablon GRC simplifies compliance management tasks, ensuring adherence to regulations. Its robust reporting tools enable stakeholders to generate customised reports on key performance indicators and trends, empowering informed decision-making. Overall, Enablon GRC enhances transparency, efficiency, and control over GRC activities, helping organisations navigate complex regulatory landscapes with ease.

What are the key benefits of implementing Enablon GRC in an organisation?

Implementing Enablon GRC in an organisation offers a multitude of key benefits that can significantly enhance governance, risk management, and compliance processes. Some of the primary advantages include centralised data management, enabling a unified view of risks and compliance status; proactive risk mitigation through effective identification and assessment; streamlined compliance management with automation capabilities; robust reporting and analytics for informed decision-making based on KPIs and trends; as well as enhanced transparency and accountability through comprehensive audit trail maintenance. Overall, the implementation of Enablon GRC empowers organisations to optimise their GRC initiatives, improve operational efficiency, and ensure adherence to regulatory requirements with greater ease and effectiveness.

Is Enablon GRC suitable for businesses in regulated industries such as finance and healthcare?

Businesses operating in regulated industries, such as finance and healthcare, often wonder if Enablon GRC is a suitable solution for their specific needs. The answer is a resounding yes. Enablon GRC offers tailored functionalities that cater to the stringent regulatory requirements of these sectors. From managing financial regulations like Basel III in the finance industry to ensuring compliance with data privacy laws such as HIPAA in healthcare, Enablon GRC provides the necessary tools and capabilities to streamline governance, risk management, and compliance processes effectively. Its centralised data management, automated workflows, and robust reporting features make it an ideal choice for businesses seeking to navigate the complex regulatory landscape with confidence and efficiency.

Can Enablon GRC be customised to meet specific GRC requirements of different organisations?

One of the frequently asked questions about Enablon GRC is whether it can be customised to meet the specific GRC requirements of different organisations. The answer is a resounding yes. Enablon GRC is designed with flexibility and scalability in mind, allowing organisations to tailor the platform to align with their unique governance, risk, and compliance needs. Through customisation options such as configurable workflows, data fields, reporting templates, and user permissions, Enablon GRC empowers businesses to adapt the system to reflect their specific GRC frameworks and regulatory obligations. This flexibility ensures that organisations can effectively address their individual compliance challenges and achieve optimal alignment with their strategic objectives.

Identity Access Management in SAP

The Importance of Identity Access Management in SAP

In today’s digital landscape, data security is paramount for organisations across all industries. As businesses rely on enterprise resource planning (ERP) systems like SAP to manage their operations efficiently, the need for robust identity access management (IAM) within these platforms has become increasingly crucial.

What is Identity Access Management?

Identity Access Management refers to the processes and technologies used to manage and control user access to critical information within an organisation. In the context of SAP, IAM involves defining and managing user roles, permissions, and privileges within the system to ensure that only authorised individuals have access to specific data and functionalities.

The Role of IAM in SAP Security

Effective IAM in SAP helps prevent unauthorised access to sensitive data, mitigates the risk of data breaches, and ensures compliance with regulatory requirements such as GDPR and SOX. By implementing IAM controls, organisations can enforce segregation of duties, least privilege principles, and multi-factor authentication to enhance security within their SAP environment.

Benefits of Implementing IAM in SAP

  • Enhanced Security: IAM reduces the risk of insider threats and external cyberattacks by controlling user access based on predefined policies.
  • Compliance: Organisations can demonstrate compliance with industry regulations by implementing IAM controls that govern user permissions and activities.
  • Operational Efficiency: By streamlining user provisioning and deprovisioning processes, IAM helps improve operational efficiency and reduce administrative overhead.
  • Auditing and Monitoring: IAM enables organisations to track user activities, generate audit trails, and monitor system access for suspicious behaviour.
  • Risk Mitigation: Proactive identification of potential risks through IAM allows organisations to address vulnerabilities before they are exploited.

In Conclusion

In conclusion, Identity Access Management plays a vital role in safeguarding sensitive information within SAP environments. Organisations that prioritise IAM implementation benefit from improved security posture, regulatory compliance, operational efficiency, and risk mitigation. By investing in robust IAM solutions tailored to their SAP systems, businesses can proactively protect their data assets and maintain trust with stakeholders.


9 Essential Tips for Effective Identity Access Management in SAP

  1. Implement role-based access control to restrict user permissions.
  2. Regularly review and update user access rights to ensure security.
  3. Enforce strong password policies for user accounts.
  4. Enable multi-factor authentication for an added layer of security.
  5. Monitor and log user activities to detect any suspicious behaviour.
  6. Provide training to users on best practices for identity access management.
  7. Integrate identity access management with other security solutions for comprehensive protection.
  8. Establish clear procedures for granting and revoking access privileges.
  9. Regularly audit user access to maintain compliance and security.

Implement role-based access control to restrict user permissions.

To enhance security and streamline user access within SAP systems, it is recommended to implement role-based access control. By assigning specific roles to users based on their job functions and responsibilities, organisations can restrict permissions to only the necessary data and functionalities required to perform their tasks. This approach helps enforce the principle of least privilege, reducing the risk of unauthorised access to sensitive information and mitigating potential security threats. Role-based access control in SAP not only enhances data protection but also simplifies user management processes by ensuring that users have appropriate access levels aligned with their roles within the organisation.

Regularly review and update user access rights to ensure security.

Regularly reviewing and updating user access rights in SAP is a fundamental practice in maintaining robust security measures within the system. By conducting periodic audits of user permissions and roles, organisations can identify and address any discrepancies or potential security risks promptly. Ensuring that users have only the necessary access rights based on their roles not only enhances data security but also helps in complying with regulatory requirements. Proactive management of user access rights in SAP contributes to a more secure environment, minimises the risk of unauthorised activities, and strengthens overall cybersecurity posture.

Enforce strong password policies for user accounts.

Enforcing strong password policies for user accounts is a fundamental aspect of effective Identity Access Management in SAP. By requiring users to create complex passwords that include a combination of letters, numbers, and special characters, organisations can significantly enhance the security of their SAP environment. Strong passwords help prevent unauthorised access to sensitive data and reduce the risk of password-related security breaches. Additionally, regular password changes and restrictions on password reuse further strengthen the overall security posture of the system, ensuring that only authorised users with secure credentials can access critical information within SAP.

Enable multi-factor authentication for an added layer of security.

Enabling multi-factor authentication in SAP is a highly recommended practice to enhance security measures within the system. By requiring users to provide multiple forms of verification before accessing sensitive data or functionalities, such as a password combined with a unique code sent to their mobile device, organisations can significantly reduce the risk of unauthorised access and potential data breaches. This additional layer of security adds an extra barrier for malicious actors trying to compromise user accounts, reinforcing the overall integrity of the identity access management framework in SAP.

Monitor and log user activities to detect any suspicious behaviour.

Monitoring and logging user activities within SAP is a crucial tip in Identity Access Management. By tracking and recording user interactions, organisations can proactively identify any suspicious behaviour or unauthorised access attempts. This practice not only helps in detecting potential security threats but also enables swift response and mitigation of risks. By maintaining detailed logs of user activities, businesses can enhance their overall security posture, strengthen compliance efforts, and ensure the integrity of their SAP environment.

Provide training to users on best practices for identity access management.

To enhance the effectiveness of identity access management in SAP, it is essential to provide comprehensive training to users on best practices. Educating users about the importance of maintaining secure access credentials, following proper authentication protocols, and understanding their roles and responsibilities within the system can significantly reduce the risk of security breaches. By promoting a culture of awareness and accountability through training sessions, organisations can empower their employees to actively contribute to maintaining a secure IAM environment in SAP.

Integrate identity access management with other security solutions for comprehensive protection.

To enhance the security of your SAP environment, it is advisable to integrate identity access management with other security solutions. By combining IAM with technologies such as threat detection, encryption, and endpoint protection, organisations can establish a layered defence strategy that offers comprehensive protection against a wide range of cyber threats. This integrated approach not only strengthens access controls within SAP but also helps in detecting and responding to security incidents more effectively. By leveraging the synergy between IAM and other security solutions, businesses can fortify their defences and safeguard their critical data assets from evolving cybersecurity risks.

Establish clear procedures for granting and revoking access privileges.

Establishing clear procedures for granting and revoking access privileges is a fundamental aspect of effective Identity Access Management in SAP. By defining transparent processes for assigning user permissions and removing access rights when necessary, organisations can ensure that only authorised individuals have the appropriate level of system access. This practice not only enhances security by preventing unauthorised usage but also streamlines administrative tasks, improves compliance with regulations, and minimises the risk of insider threats. Clear procedures for managing access privileges in SAP contribute to a more secure and efficient IT environment overall.

Regularly audit user access to maintain compliance and security.

Regularly auditing user access within SAP is a fundamental practice to uphold compliance standards and enhance security measures. By conducting routine audits, organisations can ensure that user permissions align with business requirements and regulatory mandates. Identifying and addressing any discrepancies or unauthorised access promptly not only mitigates the risk of data breaches but also fosters a culture of accountability and transparency. Through consistent monitoring and auditing of user access, businesses can proactively safeguard their SAP environment, maintain compliance with industry regulations, and bolster overall cybersecurity resilience.

Article: Mobile Identity and Access Management

The Importance of Mobile Identity and Access Management

Mobile devices have become an integral part of our daily lives, enabling us to stay connected and productive on the go. However, with this convenience comes the challenge of securing access to sensitive data and applications. This is where Mobile Identity and Access Management (IAM) plays a crucial role.

What is Mobile IAM?

Mobile IAM refers to the processes and technologies used to manage and secure access to resources on mobile devices. It encompasses authentication, authorisation, and other security measures to ensure that only authorised users can access data and applications from their mobile devices.

The Benefits of Mobile IAM

Implementing a robust Mobile IAM solution offers several benefits:

  • Enhanced Security: By implementing multi-factor authentication, device profiling, and encryption, Mobile IAM enhances the security of mobile access to corporate resources.
  • User Experience: A seamless user experience is essential for user adoption. Mobile IAM solutions provide convenient yet secure access to applications and data from any location.
  • Compliance: With regulations such as GDPR and HIPAA governing data privacy and security, mobile IAM helps organisations achieve compliance by enforcing access controls and audit trails.
  • Remote Management: IT administrators can remotely manage user access rights, permissions, and policies on mobile devices, ensuring consistent security across the organisation.

Challenges in Mobile IAM

While Mobile IAM offers numerous benefits, organisations may face challenges in its implementation:

  • User Acceptance: Balancing security with usability is crucial. Complex authentication processes may hinder user acceptance of Mobile IAM solutions.
  • Device Diversity: Managing access across a diverse range of mobile devices with varying operating systems can be challenging for IT teams.
  • Data Protection: Securing data stored on or accessed by mobile devices requires robust encryption mechanisms to prevent data breaches.

The Future of Mobile IAM

As the use of mobile devices continues to grow in the workplace, the importance of effective Mobile IAM will only increase. Future trends in Mobile IAM include biometric authentication, context-aware access controls based on user behaviour, and integration with cloud-based identity services for enhanced security.


Understanding Mobile Identity and Access Management: Key FAQs and Best Practices

  1. What is mobile identity and access management (IAM)?
  2. Why is mobile IAM important for businesses?
  3. How does mobile IAM enhance security on mobile devices?
  4. What are the common challenges in implementing mobile IAM?
  5. What are the best practices for securing mobile identity and access management?

What is mobile identity and access management (IAM)?

Mobile identity and access management (IAM) refers to the set of processes and technologies that govern how users are authenticated and authorised to access resources on mobile devices. It involves establishing secure protocols for verifying the identities of users, managing their permissions to access specific data or applications, and enforcing security policies to protect sensitive information. Mobile IAM plays a vital role in ensuring that only authorised individuals can securely access corporate resources from their mobile devices while maintaining a balance between user convenience and robust security measures.

Why is mobile IAM important for businesses?

Mobile Identity and Access Management (IAM) is crucial for businesses due to the proliferation of mobile devices in the workplace. With employees accessing corporate data and applications from various locations and devices, ensuring secure and controlled access is paramount. Mobile IAM provides a robust framework for authentication, authorisation, and data protection, safeguarding sensitive information against unauthorised access or breaches. By implementing mobile IAM solutions, businesses can enhance security, streamline user access management, achieve regulatory compliance, and mitigate the risks associated with mobile device usage in the corporate environment. Ultimately, mobile IAM empowers businesses to embrace the productivity benefits of mobile technology while maintaining a strong security posture.

How does mobile IAM enhance security on mobile devices?

Mobile Identity and Access Management (IAM) enhances security on mobile devices through a range of advanced measures. By implementing multi-factor authentication, mobile IAM ensures that only authorised users can access sensitive data and applications, adding an extra layer of security beyond traditional password protection. Additionally, device profiling capabilities enable organisations to identify and verify devices accessing their networks, reducing the risk of unauthorised access. Encryption mechanisms employed by mobile IAM solutions safeguard data in transit and at rest, protecting it from potential breaches. Overall, mobile IAM plays a critical role in bolstering security on mobile devices by combining authentication, authorisation, and encryption to create a robust defence against cyber threats.

What are the common challenges in implementing mobile IAM?

Implementing mobile Identity and Access Management (IAM) poses several common challenges for organisations. One major challenge is ensuring a balance between security and user experience. Complex authentication processes can lead to user frustration and resistance to adopting secure practices. Additionally, managing access across a diverse range of mobile devices with different operating systems can be complex for IT teams. Data protection is another critical challenge, as securing data stored on or accessed by mobile devices requires robust encryption mechanisms to prevent potential data breaches. Overcoming these challenges requires a strategic approach that prioritises both security and usability in mobile IAM implementation.

What are the best practices for securing mobile identity and access management?

When it comes to securing mobile identity and access management, following best practices is essential to safeguard sensitive data and applications on mobile devices. Some key recommendations include implementing multi-factor authentication to add an extra layer of security, enforcing strong password policies, regularly updating mobile device operating systems and applications to patch vulnerabilities, encrypting data both at rest and in transit, leveraging biometric authentication where possible for added security, conducting regular security audits and assessments, and providing comprehensive user training on mobile security practices. By adhering to these best practices, organisations can enhance the overall security posture of their mobile identity and access management systems.

The Importance of SailPoint Segregation of Duties

The Importance of SailPoint Segregation of Duties

In the realm of identity and access management (IAM), maintaining proper segregation of duties is crucial for ensuring the security and integrity of an organisation’s data and systems. SailPoint, a leading IAM solution provider, offers robust capabilities for managing user access and enforcing segregation of duties policies.

What is Segregation of Duties (SoD)?

Segregation of Duties refers to the practice of dividing tasks and privileges among different individuals or roles within an organisation to prevent conflicts of interest and reduce the risk of fraud or errors. By enforcing SoD policies, organisations can ensure that no single user has excessive access that could lead to misuse or security breaches.

The Role of SailPoint in SoD Compliance

SailPoint’s IdentityNow platform provides powerful tools for defining, monitoring, and enforcing segregation of duties policies across an organisation’s IT environment. With SailPoint, administrators can easily configure rules that govern which combinations of access rights are considered incompatible and should not be assigned to the same user.

By leveraging SailPoint’s automated workflows and access certification processes, organisations can streamline the identification and remediation of SoD violations. This proactive approach helps prevent potential risks before they escalate into serious security incidents.

Benefits of SailPoint SoD Controls

  • Risk Mitigation: By implementing SailPoint’s SoD controls, organisations can reduce the likelihood of unauthorised activities that could compromise sensitive data or systems.
  • Compliance Adherence: SailPoint helps organisations align with regulatory requirements by ensuring that users do not possess conflicting access rights that violate compliance standards.
  • Operational Efficiency: Automated SoD checks in SailPoint streamline access reviews and approvals, saving time and resources while maintaining a secure environment.
  • Audit Readiness: With detailed audit logs and reporting capabilities, SailPoint enables organisations to demonstrate compliance with SoD policies during audits or assessments.

Conclusion

In conclusion, effective segregation of duties is a fundamental principle in IAM that safeguards against internal threats and promotes a culture of accountability within an organisation. By utilising SailPoint’s advanced capabilities for managing SoD controls, businesses can enhance their security posture, achieve regulatory compliance, and operate more efficiently in today’s complex IT landscape.


Essential Tips for Effective Segregation of Duties Management in SailPoint

  1. Clearly define roles and responsibilities within the organisation.
  2. Identify critical business processes and associated access rights.
  3. Implement automated tools to detect and remediate segregation of duties violations.
  4. Regularly review and update segregation of duties policies based on changes in the organization.
  5. Provide training to employees on the importance of segregation of duties.

Clearly define roles and responsibilities within the organisation.

To enhance SailPoint segregation of duties effectiveness, it is essential to clearly define roles and responsibilities within the organisation. By establishing distinct job functions and associated access privileges, organisations can ensure that users are granted only the necessary permissions to perform their duties effectively. This clarity not only helps in preventing conflicts of interest but also streamlines the process of assigning and monitoring access rights, ultimately contributing to a more secure and compliant IAM environment.

Identify critical business processes and associated access rights.

To enhance SailPoint segregation of duties, it is essential to identify critical business processes and their corresponding access rights. By understanding the key operations that drive the organisation and the specific access privileges required to execute them, businesses can establish clear guidelines for assigning access permissions. This proactive approach ensures that users only have the necessary access to perform their job functions, reducing the risk of unauthorised activities and maintaining a secure environment. By aligning access rights with critical business processes, organisations can strengthen their overall security posture and compliance efforts within the SailPoint environment.

Implement automated tools to detect and remediate segregation of duties violations.

To enhance the effectiveness of SailPoint segregation of duties practices, it is recommended to implement automated tools that can swiftly detect and remediate violations. By leveraging these tools within the SailPoint platform, organisations can proactively identify instances where users possess conflicting access rights and take immediate action to rectify such violations. Automation not only accelerates the detection process but also streamlines the remediation workflow, ensuring that SoD issues are addressed promptly to maintain a secure and compliant IT environment.

Regularly review and update segregation of duties policies based on changes in the organization.

It is essential to regularly review and update segregation of duties policies in SailPoint to align with changes within the organisation. As roles, responsibilities, and access requirements evolve over time, ensuring that SoD policies remain up-to-date is crucial for maintaining a secure and compliant environment. By conducting periodic assessments and adjusting policies based on organisational changes, businesses can proactively mitigate risks associated with conflicting access rights and uphold the integrity of their IAM framework.

Provide training to employees on the importance of segregation of duties.

It is essential to provide comprehensive training to employees on the significance of segregation of duties within the SailPoint system. By educating staff members about the importance of maintaining clear boundaries between different roles and responsibilities, organisations can enhance their overall security posture and reduce the risk of internal fraud or errors. Training sessions can help employees understand how adherence to segregation of duties policies contributes to a more secure and compliant work environment, fostering a culture of accountability and integrity across the organisation.

Article: Identity Access Management Software Tools

The Importance of Identity Access Management Software Tools

Identity Access Management (IAM) software tools play a crucial role in modern cybersecurity strategies. As organisations increasingly rely on digital systems and cloud services, managing access to sensitive data and resources has become more complex and challenging. IAM tools offer a comprehensive solution to control and secure user identities and their access rights within an organisation.

Enhanced Security

One of the primary benefits of IAM software tools is enhanced security. By implementing robust authentication mechanisms, such as multi-factor authentication and single sign-on, organisations can significantly reduce the risk of unauthorised access to critical systems and data. IAM tools also enable administrators to enforce security policies, monitor user activities, and detect suspicious behaviour in real-time.

Efficient Access Management

IAM software tools streamline access management processes by centralising user identity information and access controls. This centralised approach simplifies the onboarding and offboarding of employees, contractors, and partners, ensuring that individuals have the appropriate level of access based on their roles and responsibilities. Automated provisioning and deprovisioning capabilities help reduce human errors and ensure compliance with regulatory requirements.

Compliance and Auditability

For organisations operating in regulated industries, IAM software tools are essential for maintaining compliance with data protection laws and industry standards. These tools provide detailed audit logs, reporting functionalities, and policy enforcement mechanisms that support compliance efforts. By tracking user access permissions and activities, organisations can demonstrate accountability and transparency to regulatory authorities.

Scalability and Flexibility

Modern IAM software tools are designed to scale alongside the growth of an organisation. Whether expanding geographically or adopting new technologies, IAM solutions offer flexibility to adapt to changing business requirements. Cloud-based IAM platforms provide scalability without compromising security, allowing organisations to efficiently manage identities across diverse environments.

Conclusion

In conclusion, identity access management software tools are indispensable for safeguarding digital assets, ensuring operational efficiency, and meeting compliance obligations. Organisations that invest in robust IAM solutions not only strengthen their cybersecurity posture but also enhance user experience by providing seamless access to resources. As cyber threats continue to evolve, implementing comprehensive IAM strategies is paramount for protecting sensitive information and maintaining trust with stakeholders.


8 Essential Tips for Optimising Identity Access Management Software Tools

  1. Ensure that the IAM software tools support multi-factor authentication for enhanced security.
  2. Regularly review and update user access permissions to prevent unauthorized access.
  3. Integrate IAM tools with existing systems for seamless user management across platforms.
  4. Implement role-based access control to assign appropriate levels of access to users based on their roles.
  5. Monitor user activity and set up alerts for any suspicious behaviour to detect potential security threats.
  6. Provide regular training to users on best practices for managing their identities and access rights.
  7. Regularly audit user permissions and remove unnecessary access rights to reduce security risks.
  8. Backup IAM configurations regularly to ensure quick recovery in case of system failures or data loss.

Ensure that the IAM software tools support multi-factor authentication for enhanced security.

To maximise security measures within your organisation, it is crucial to ensure that the Identity Access Management (IAM) software tools you utilise support multi-factor authentication. By implementing multi-factor authentication, which requires users to verify their identity through multiple methods such as passwords, biometrics, or security tokens, you add an extra layer of protection against unauthorised access. This additional security measure significantly enhances the overall security posture of your systems and data, mitigating the risks associated with potential cyber threats.

Regularly review and update user access permissions to prevent unauthorized access.

Regularly reviewing and updating user access permissions is a fundamental practice in identity access management software tools to prevent unauthorised access. By conducting routine audits of user permissions, organisations can ensure that individuals only have access to the resources necessary for their roles. This proactive approach not only reduces the risk of security breaches but also enhances overall data protection measures. By staying vigilant and promptly adjusting access permissions as needed, organisations can minimise vulnerabilities and maintain a secure environment for their digital assets.

Integrate IAM tools with existing systems for seamless user management across platforms.

Integrating Identity Access Management (IAM) tools with existing systems is a valuable tip to ensure seamless user management across platforms. By integrating IAM tools with existing systems, organisations can centralise user identity information and access controls, enabling consistent management of user permissions and access rights across different platforms and applications. This integration streamlines user onboarding processes, enhances security by enforcing uniform access policies, and simplifies the overall administration of user identities within the organisation. Ultimately, integrating IAM tools with existing systems promotes efficiency, reduces complexity, and strengthens the overall security posture of the organisation.

Implement role-based access control to assign appropriate levels of access to users based on their roles.

Implementing role-based access control (RBAC) is a fundamental tip when utilising identity access management software tools. By assigning access permissions based on users’ roles within an organisation, RBAC ensures that individuals have the appropriate level of access to resources and data needed to perform their job functions effectively. This approach not only enhances security by limiting unnecessary privileges but also simplifies access management processes, streamlining user provisioning and reducing the risk of unauthorised access. With RBAC, organisations can enforce least privilege principles, mitigate insider threats, and maintain compliance with regulatory requirements by aligning access rights with job responsibilities.

Monitor user activity and set up alerts for any suspicious behaviour to detect potential security threats.

Monitoring user activity and setting up alerts for any suspicious behaviour are essential practices when utilising identity access management software tools. By closely monitoring user interactions and access patterns, organisations can proactively detect potential security threats before they escalate. Setting up alerts for unusual activities or deviations from established norms enables quick identification of malicious behaviour, helping to prevent data breaches and unauthorised access to sensitive information. This proactive approach enhances overall security posture and ensures a timely response to any potential security incidents within the IT environment.

Provide regular training to users on best practices for managing their identities and access rights.

Providing regular training to users on best practices for managing their identities and access rights is a crucial tip when utilising identity access management software tools. By educating users on the importance of safeguarding their credentials, understanding access permissions, and following security protocols, organisations can empower their employees to contribute to a more secure digital environment. Regular training sessions help reinforce awareness of potential risks and encourage proactive behaviour in maintaining the integrity of user identities within the system. This proactive approach not only enhances security posture but also fosters a culture of responsibility and accountability among users, ultimately contributing to a more robust IAM strategy.

Regularly audit user permissions and remove unnecessary access rights to reduce security risks.

Regularly auditing user permissions and eliminating unnecessary access rights is a fundamental practice in enhancing security within an organisation’s digital ecosystem. By conducting routine audits, administrators can identify and rectify any instances of over-privileged accounts or dormant user access, thereby reducing the potential attack surface and mitigating security risks. This proactive approach not only strengthens the overall security posture but also ensures that users have the appropriate level of access needed to perform their roles effectively, aligning with the principle of least privilege.

Backup IAM configurations regularly to ensure quick recovery in case of system failures or data loss.

Regularly backing up IAM configurations is a critical practice to ensure swift recovery in the event of system failures or data loss. By maintaining up-to-date backups of IAM configurations, organisations can minimise downtime and mitigate the impact of unexpected incidents. These backups serve as a safeguard against potential risks, allowing administrators to restore access controls and user identities promptly. Prioritising regular backups not only enhances the resilience of IAM systems but also demonstrates a proactive approach to maintaining the integrity and availability of critical identity management resources.

The Importance of Mobile Identity Access Management

In today’s digital age, where mobile devices have become an integral part of both personal and professional life, the need for robust security measures is more critical than ever. Mobile Identity Access Management (IAM) plays a crucial role in ensuring secure access to sensitive data and applications on mobile devices.

Mobile IAM involves the processes and technologies used to manage and secure user identities on mobile devices. It encompasses authentication, authorisation, and other security measures to control access to resources based on user identity.

Benefits of Mobile IAM

Implementing Mobile IAM offers several benefits:

  • Enhanced Security: By enforcing strict authentication methods and access controls, Mobile IAM helps prevent unauthorised access to sensitive information.
  • Improved User Experience: Users can securely access applications and data from anywhere, at any time, without compromising security.
  • Compliance: Mobile IAM solutions help organisations comply with data protection regulations by ensuring that only authorised users have access to sensitive data.
  • Centralised Management: Administrators can centrally manage user identities, access policies, and permissions for all mobile devices within the organisation.

Challenges of Mobile IAM

While Mobile IAM offers significant benefits, there are challenges that organisations may face when implementing these solutions:

  • User Adoption: Ensuring that users understand and comply with security protocols can be a challenge, especially in fast-paced environments where convenience often trumps security.
  • Integration Complexity: Integrating Mobile IAM solutions with existing IT infrastructure can be complex and require careful planning to ensure seamless operation.
  • Data Privacy Concerns: Managing user identities on mobile devices raises concerns about data privacy and the potential risks associated with storing sensitive information on these devices.

Best Practices for Implementing Mobile IAM

To overcome these challenges and maximise the benefits of Mobile IAM, organisations should consider the following best practices:

  • Multifactor Authentication: Implementing multifactor authentication methods adds an extra layer of security beyond passwords.
  • User Education: Providing comprehensive training and awareness programmes to educate users about the importance of secure mobile practices.
  • Regular Auditing: Conducting regular audits of user access rights and permissions to identify any potential vulnerabilities or unauthorised activities.
  • Data Encryption: Encrypting sensitive data stored on mobile devices helps protect it from unauthorised access in case of loss or theft.

In conclusion, Mobile Identity Access Management is essential for maintaining a secure mobile environment in today’s interconnected world. By implementing best practices and addressing potential challenges proactively, organisations can ensure that their sensitive data remains protected while enabling seamless access for authorised users.

This article is intended for informational purposes only. For specific guidance on implementing Mobile IAM solutions, consult with IT security professionals or specialists in the field.


Understanding Mobile Identity Access Management: Importance, Security, Components, Privacy, and Compliance

  1. What is Mobile Identity Access Management (IAM) and why is it important?
  2. How does Mobile IAM enhance security on mobile devices?
  3. What are the key components of Mobile IAM?
  4. How can organisations ensure user privacy while implementing Mobile IAM?
  5. Are there any compliance regulations that govern Mobile Identity Access Management?

What is Mobile Identity Access Management (IAM) and why is it important?

Mobile Identity Access Management (IAM) refers to the processes and technologies used to manage and secure user identities on mobile devices. It involves authentication, authorisation, and other security measures to control access to resources based on user identity. Mobile IAM is crucial in today’s digital landscape as it ensures secure access to sensitive data and applications on mobile devices. By enforcing strict authentication methods, access controls, and centralised management of user identities, Mobile IAM enhances security, improves user experience, aids in regulatory compliance, and mitigates the risks associated with unauthorised access to confidential information. In essence, Mobile IAM plays a vital role in safeguarding data integrity and protecting organisations from potential security threats in the mobile environment.

How does Mobile IAM enhance security on mobile devices?

Mobile Identity Access Management (IAM) enhances security on mobile devices by implementing robust authentication mechanisms and access controls. With Mobile IAM in place, users are required to go through secure authentication processes, such as biometric verification or multifactor authentication, before accessing sensitive data or applications. This ensures that only authorised individuals can gain access to critical resources, reducing the risk of unauthorised access and data breaches. Additionally, Mobile IAM allows for centralised management of user identities and access policies, enabling administrators to enforce consistent security measures across all mobile devices within an organisation. By integrating Mobile IAM solutions, organisations can significantly strengthen the security posture of their mobile environment and protect valuable information from potential threats.

What are the key components of Mobile IAM?

When considering Mobile Identity Access Management (IAM), it is essential to understand the key components that make up this crucial security framework. The primary components of Mobile IAM typically include authentication mechanisms, authorisation protocols, user provisioning processes, and identity federation capabilities. Authentication methods such as biometric recognition, PINs, or two-factor authentication play a vital role in verifying user identities. Authorisation protocols define what resources users can access based on their authenticated identity. User provisioning ensures that users have the appropriate access rights and permissions assigned to them. Identity federation enables seamless and secure access to multiple applications across different platforms. These key components work together to establish a robust Mobile IAM system that safeguards sensitive data and ensures secure access on mobile devices.

How can organisations ensure user privacy while implementing Mobile IAM?

Ensuring user privacy is a paramount concern for organisations when implementing Mobile Identity Access Management (IAM). To safeguard user privacy, organisations should adopt privacy-by-design principles, ensuring that data protection measures are integrated into the IAM system from the outset. Implementing strong encryption protocols for sensitive user data stored on mobile devices and during transmission can mitigate the risk of unauthorised access. Additionally, providing clear and transparent information to users about the data collected, how it is used, and their rights regarding their personal information is crucial for building trust and maintaining compliance with data protection regulations such as GDPR. Regularly reviewing and updating privacy policies in alignment with evolving privacy laws and best practices can help organisations stay proactive in protecting user privacy within their Mobile IAM framework.

Are there any compliance regulations that govern Mobile Identity Access Management?

Ensuring compliance with regulations is a crucial aspect of Mobile Identity Access Management (IAM). Several compliance regulations govern the implementation of IAM solutions on mobile devices to safeguard sensitive data and ensure secure access. Common regulations include the General Data Protection Regulation (GDPR), the Health Insurance Portability and Accountability Act (HIPAA), and the Payment Card Industry Data Security Standard (PCI DSS). These regulations outline specific requirements for protecting user identities, securing data access, and maintaining privacy standards on mobile platforms. Organisations must adhere to these regulations to mitigate risks, protect user information, and avoid potential legal consequences related to non-compliance in Mobile IAM practices.

The Importance of Lieberman Privileged Access Management in Enhancing Cybersecurity

In today’s digital landscape, the protection of sensitive data and critical systems is paramount for organisations across all industries. With the increasing sophistication of cyber threats, it has become essential for businesses to implement robust security measures to safeguard their assets. One such crucial component of cybersecurity is Lieberman Privileged Access Management (PAM).

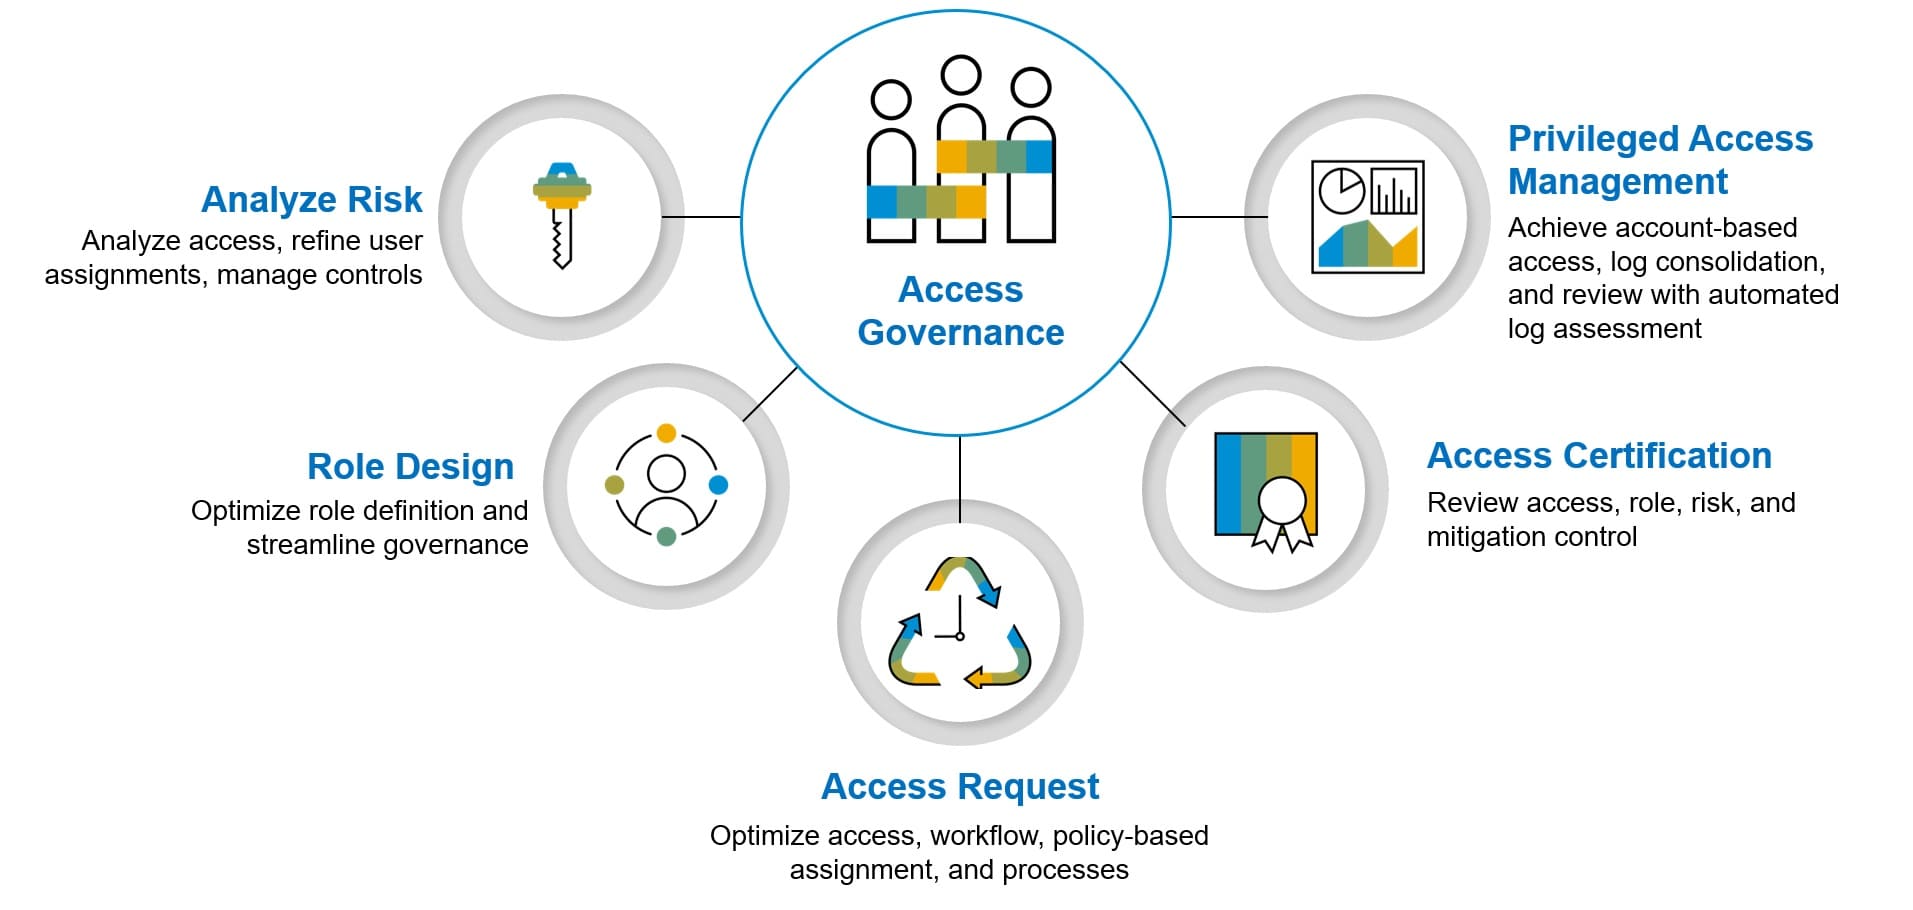
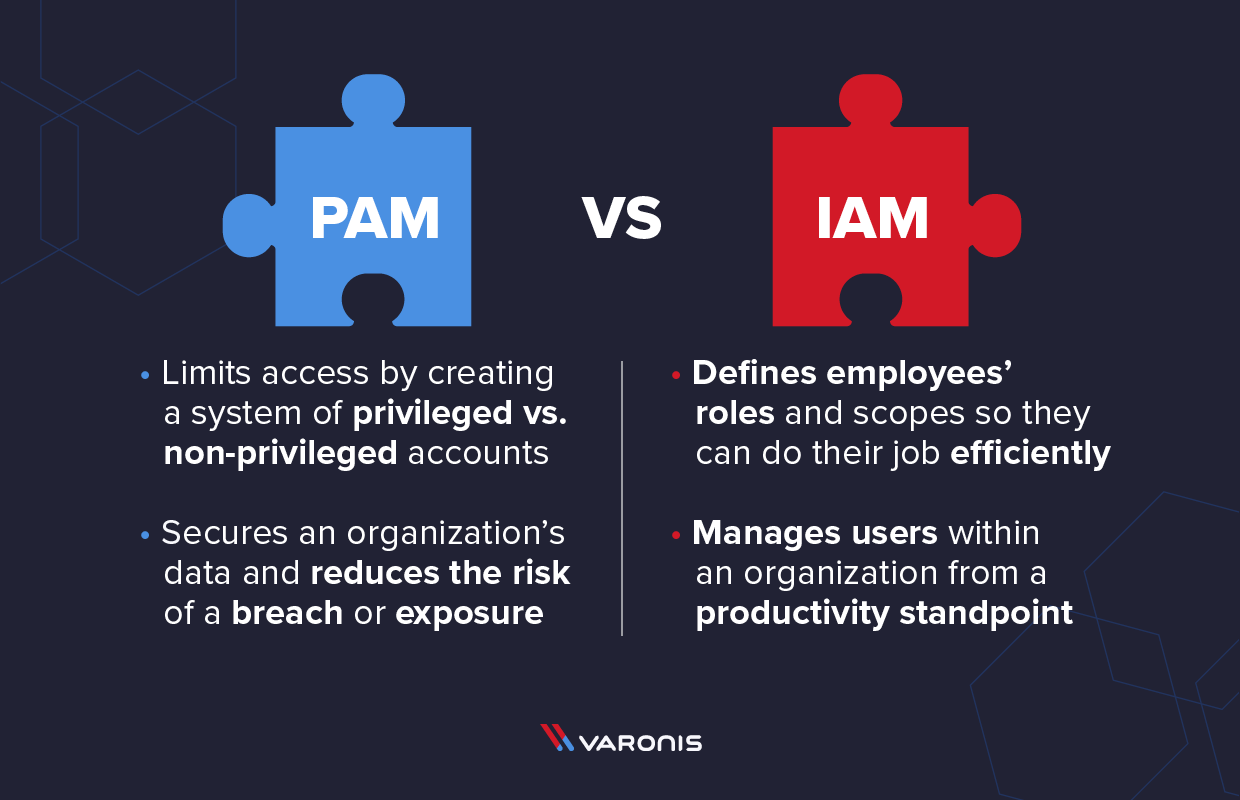
Lieberman PAM is a comprehensive solution designed to manage and secure privileged accounts within an organisation. Privileged accounts, such as administrator and service accounts, have elevated access rights that, if compromised, can pose significant risks to an organisation’s security posture. By implementing Lieberman PAM, businesses can effectively control and monitor access to these critical accounts, reducing the likelihood of unauthorised access and potential data breaches.

One of the key features of Lieberman PAM is its ability to enforce least privilege principles. This means that users are only granted the minimum level of access required to perform their tasks, reducing the risk of insider threats or accidental misuse of privileges. By limiting access rights based on job roles and responsibilities, organisations can enhance their overall security posture and mitigate the impact of security incidents.

Furthermore, Lieberman PAM offers robust auditing and reporting capabilities that provide organisations with visibility into privileged account activities. By monitoring user actions in real-time and generating detailed audit logs, businesses can detect suspicious behaviour promptly and take proactive measures to prevent potential security breaches.

Another significant benefit of Lieberman PAM is its support for compliance requirements. Many regulatory standards, such as GDPR and PCI DSS, mandate strict controls over privileged access to ensure data protection and privacy. By implementing Lieberman PAM, organisations can demonstrate compliance with these regulations through comprehensive access controls and audit trails.

In conclusion, Lieberman Privileged Access Management plays a vital role in enhancing cybersecurity by securing privileged accounts, enforcing least privilege principles, providing auditing capabilities, and ensuring compliance with regulatory standards. Organisations that prioritise the protection of their critical assets can benefit significantly from implementing Lieberman PAM as part of their comprehensive cybersecurity strategy.


7 Essential Tips for Optimising Lieberman Privileged Access Management

  1. Implement least privilege access to restrict users’ access to only what is necessary for their roles
  2. Regularly review and update user permissions to ensure they align with current responsibilities
  3. Enable multi-factor authentication for an added layer of security
  4. Monitor and log all privileged user activities for auditing purposes
  5. Educate employees on the importance of safeguarding privileged credentials
  6. Utilise session recording to track and monitor privileged sessions in real-time
  7. Integrate Lieberman privileged access management with existing security tools for enhanced protection

Implement least privilege access to restrict users’ access to only what is necessary for their roles

Implementing least privilege access is a fundamental principle in Lieberman Privileged Access Management that helps organisations enhance their cybersecurity posture. By restricting users’ access to only what is necessary for their roles, businesses can minimise the risk of unauthorised activities and potential security breaches. This proactive approach ensures that users have the minimum level of access required to perform their tasks effectively, reducing the likelihood of insider threats or accidental misuse of privileges. Through the implementation of least privilege access controls, organisations can strengthen their security defences and mitigate the impact of security incidents, ultimately safeguarding their critical assets and data.

Regularly review and update user permissions to ensure they align with current responsibilities

Regularly reviewing and updating user permissions within Lieberman Privileged Access Management is a crucial practice to maintain a secure and efficient access control system. By aligning user permissions with current job roles and responsibilities, organisations can minimise the risk of unauthorised access and potential security breaches. This proactive approach ensures that users have the necessary access privileges to perform their tasks effectively while preventing unnecessary exposure to sensitive data or systems. Regular reviews also help in identifying and revoking access rights for users who have changed roles or left the organisation, further enhancing the overall security posture.

Enable multi-factor authentication for an added layer of security

Enabling multi-factor authentication for Lieberman Privileged Access Management adds an extra layer of security to safeguard privileged accounts effectively. By requiring users to provide multiple forms of verification before accessing critical systems, such as a password and a unique code sent to their mobile device, organisations can significantly enhance their security posture. This additional security measure helps prevent unauthorised access even if passwords are compromised, reducing the risk of cyber threats and ensuring the integrity of privileged account management.

Monitor and log all privileged user activities for auditing purposes

Monitoring and logging all privileged user activities for auditing purposes is a crucial tip when utilising Lieberman Privileged Access Management. By tracking and recording every action taken by privileged users, organisations can establish a comprehensive trail of accountability and oversight. This practice not only enhances security by detecting any suspicious or unauthorised activities promptly but also ensures compliance with regulatory requirements. Through detailed audit logs, businesses can gain valuable insights into how privileged accounts are being used, enabling them to identify potential security risks and take proactive measures to safeguard their critical assets effectively.

Educate employees on the importance of safeguarding privileged credentials

It is crucial to educate employees on the significance of safeguarding privileged credentials when utilising Lieberman Privileged Access Management. By raising awareness about the importance of protecting these sensitive account details, organisations can empower their staff to recognise and mitigate potential security risks. Educating employees on best practices for managing and securing privileged credentials not only enhances overall cybersecurity but also cultivates a culture of accountability and responsibility within the workforce. This proactive approach can significantly strengthen the organisation’s security posture and minimise the likelihood of unauthorised access to critical systems and data.

Utilise session recording to track and monitor privileged sessions in real-time

By utilising session recording within Lieberman Privileged Access Management, organisations can effectively track and monitor privileged sessions in real-time. This feature provides a valuable insight into user activities, allowing for the immediate detection of any suspicious behaviour or unauthorised access attempts. By maintaining a detailed record of privileged sessions, businesses can enhance their security posture by proactively identifying and addressing potential threats before they escalate. Real-time session recording in Lieberman PAM offers a proactive approach to privileged access management, enabling organisations to strengthen their cybersecurity defences and safeguard their critical assets effectively.

Integrate Lieberman privileged access management with existing security tools for enhanced protection

Integrating Lieberman privileged access management with existing security tools is a valuable tip to enhance protection and strengthen overall cybersecurity measures within an organisation. By seamlessly integrating Lieberman PAM with other security solutions, such as SIEM platforms or endpoint protection systems, businesses can create a unified security ecosystem that offers comprehensive visibility and control over privileged accounts. This integration enables real-time threat detection, automated response mechanisms, and streamlined incident management processes, ultimately fortifying the organisation’s defence against cyber threats and ensuring the integrity of sensitive data and critical systems.