Cybersecurity as a Service Companies: What They Offer and How to Choose One

Cybersecurity as a service companies help organisations protect their systems, data and users through outsourced or subscription-based security services. Instead of building every capability in-house, a business can work with a specialist provider for support with areas such as threat monitoring, incident response, vulnerability management and security advice.

These services can be useful for organisations that lack the time, expertise or resources to manage every aspect of cybersecurity themselves. However, providers differ considerably in their services, expertise and approach. Understanding what they offer—and what your organisation needs—is essential before choosing one.

What is cybersecurity as a service?

Cybersecurity as a service (often shortened to CaaS) is a model in which an external provider delivers security capabilities on an ongoing basis. Services may be delivered remotely, through cloud-based tools, by security specialists, or through a combination of these approaches.

The term covers a broad range of offerings. Some companies focus on a single area, such as penetration testing or security awareness training. Others provide a wider managed security service, combining technology, monitoring and expert support.

Common services offered

  • Managed detection and response: Monitoring systems for suspicious activity and helping investigate and respond to potential threats.
  • Security operations centre services: Providing access to analysts and monitoring capabilities that may be difficult to maintain internally.
  • Vulnerability management: Identifying and prioritising weaknesses in systems, applications and configurations.
  • Penetration testing: Assessing the security of systems by testing them for exploitable weaknesses within an agreed scope.
  • Cloud security: Reviewing and helping protect cloud environments, accounts, workloads and configurations.
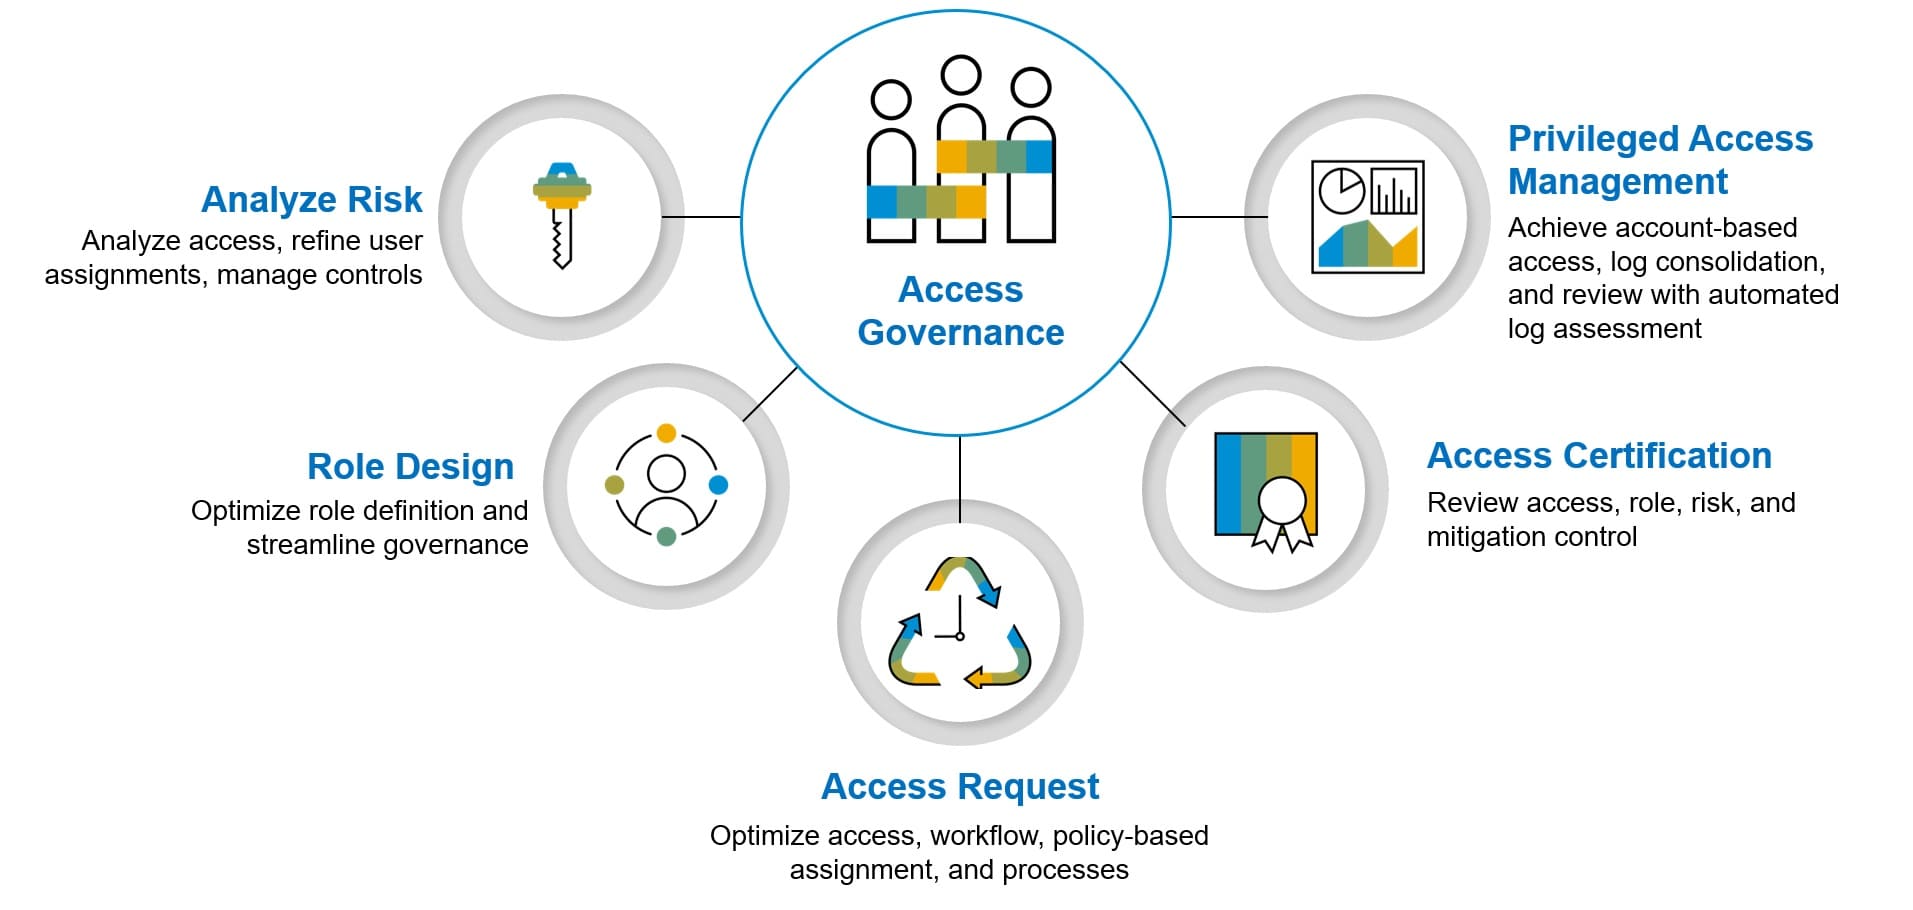
  • Identity and access management: Supporting controls such as multi-factor authentication, privileged access management and access reviews.
  • Incident response: Providing guidance or hands-on support when a security incident occurs.
  • Security awareness training: Helping employees recognise common threats, including phishing and social engineering.
  • Compliance support: Assisting with security controls, documentation and assessments linked to relevant standards or regulations.

The exact scope varies by provider. A service described as “24/7 monitoring”, for example, may not include round-the-clock investigation or response unless this is clearly stated in the contract.

Why organisations use cybersecurity service providers

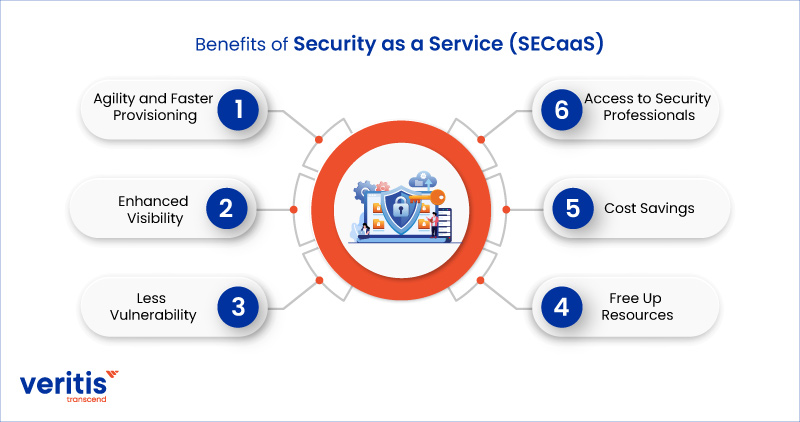
One of the main reasons to use a provider is access to specialist skills. Recruiting and retaining experienced security professionals can be challenging, particularly for smaller organisations. A service provider may offer access to a broader team and a range of security tools.

Outsourcing can also make security costs more predictable. Rather than investing in every tool and capability upfront, an organisation may pay a regular fee for an agreed service. This does not automatically make outsourcing cheaper, so the full cost—including implementation, additional services and contract changes—should be assessed.

External support can help an organisation improve its ability to detect and respond to threats. It can also allow internal IT teams to focus on other priorities. However, outsourcing does not transfer all responsibility for security. The organisation still needs to set priorities, manage access, understand its risks and oversee the provider’s work.

How to choose a cybersecurity as a service company

Start with your needs and risks

Identify the systems and information that matter most, the risks the organisation needs to address, and any existing gaps in security. A clear scope makes it easier to compare providers and avoid paying for services that do not meet your needs.

Check the service boundaries

Ask what is included, what is excluded and what happens when a potential incident is detected. Confirm monitoring hours, escalation routes, response times, reporting frequency and who is authorised to take action. Make sure these details are documented rather than relying on broad descriptions in marketing material.

Assess expertise and fit

Look at the provider’s experience with organisations of a similar size, sector and technical environment. Ask who will deliver the service, how issues are escalated and whether the team has relevant qualifications or recognised assurance. References and practical examples can help, while still respecting client confidentiality.

Understand data handling and access

A provider may need access to sensitive systems, logs or personal data. Find out where information is stored, who can access it, how it is protected and how long it is retained. Review the provider’s approach to subcontractors, data breaches and secure deletion at the end of the relationship.

Review reporting and performance measures

Useful reporting should explain findings in a way that supports decisions, not simply list alerts. Agree how the provider will measure performance, communicate risk and track remediation. Reports should help the organisation understand what needs attention and whether agreed actions have been completed.

Check contracts and exit arrangements

Review service levels, fees, renewal terms and provisions for changing or ending the service. Confirm how data, configurations and documentation will be returned or securely removed if the contract ends. A well-defined exit plan helps prevent unnecessary disruption and supplier dependence.

Potential challenges to consider

Cybersecurity as a service is not a substitute for good internal governance. Poorly defined responsibilities can create gaps, particularly during an incident. Organisations should know who makes decisions, who contacts relevant stakeholders and who is responsible for recovery.

There can also be integration challenges. A provider’s tools and processes need to work with existing systems, cloud platforms and internal procedures. Before signing, discuss implementation requirements and any changes needed to achieve effective coverage.

Finally, no provider can guarantee that an organisation will never experience a cyber incident. The aim is to reduce risk, improve visibility and strengthen the ability to respond and recover—not to promise complete protection.

Making the partnership work

A successful relationship depends on regular communication and clear ownership. Share accurate information about systems and changes, review findings promptly, and make sure recommended fixes are assigned to the right people. Schedule periodic reviews to check whether the service still matches the organisation’s needs.

Cybersecurity as a service companies can provide valuable expertise and ongoing support, particularly where internal resources are limited. The best choice is not necessarily the provider with the longest list of services. It is the one that understands the organisation’s risks, defines its responsibilities clearly and can demonstrate how its work will improve security in practice.


Essential Tips for Choosing a Cybersecurity as a Service Provider in the UK

  1. Check the provider’s security certifications and track record.
  2. Confirm exactly which services and systems are covered.
  3. Ask how quickly incidents are detected and handled.
  4. Review data storage locations and privacy safeguards.
  5. Check staff vetting, training and access controls.
  6. Agree clear service levels and reporting schedules.
  7. Test incident response plans together regularly.
  8. Understand fees, contract terms and exit options.
  9. Ensure the provider supports your regulatory obligations.

Check the provider’s security certifications and track record.

Check a provider’s security certifications and track record before signing a contract. Look for relevant, independently verified certifications, and confirm that they apply to the services you plan to use. Ask for evidence of experience with organisations similar to yours, along with references or case studies where available. Certifications can indicate that a provider follows recognised security practices, but they are not a guarantee of performance, so consider them alongside service quality, incident-handling processes and client feedback.

Confirm exactly which services and systems are covered.

Before engaging a cybersecurity as a service provider, confirm exactly which services and systems are covered. Check whether the agreement includes monitoring, investigation, incident response and reporting, and list the specific networks, devices, cloud platforms and applications in scope. Clarify any exclusions, coverage hours and additional charges so there are no gaps or surprises when support is needed.

Ask how quickly incidents are detected and handled.

Ask prospective cybersecurity as a service providers how quickly they can detect, investigate and respond to an incident. Clarify whether monitoring is continuous, what triggers an escalation and how quickly your team will be contacted. Check that response times are set out in the service agreement, including who is responsible for taking action. Fast, clearly defined processes can help limit disruption, but response times should be realistic and matched to the level of service you need.

Review data storage locations and privacy safeguards.

Review where a cybersecurity as a service provider stores and processes your data, including security logs, personal information and backups. Check which countries the data may be held in, who can access it, how it is protected and how long it is retained. Ask about encryption, access controls, subcontractors and procedures for reporting a data breach, and confirm that the provider’s safeguards meet your organisation’s privacy and regulatory requirements.

Check staff vetting, training and access controls.

Before choosing a cybersecurity as a service company, check how it vets and trains its staff, and how it controls their access to your systems and data. Ask whether background checks are carried out, how often security training is refreshed, and whether access is limited to the people who need it for their role. Strong controls—such as multi-factor authentication, privileged access management and regular access reviews—help reduce the risk of misuse or compromise.

Agree clear service levels and reporting schedules.

Agree clear service levels and reporting schedules before work begins. Specify expected response and resolution times, monitoring hours, escalation procedures and who to contact if an incident occurs. Set out how often the provider will report, what each report should include and how urgent issues will be communicated. Clear expectations make performance easier to assess and help ensure important risks are raised promptly.

Test incident response plans together regularly.

Test incident response plans regularly with your cybersecurity service provider to make sure everyone knows their role when an incident occurs. Run exercises based on realistic scenarios, such as a ransomware attack or compromised account, and practise how you will communicate, escalate the issue and coordinate containment and recovery. Review what went well and what needs improvement, then update the plan and contact details accordingly.

Understand fees, contract terms and exit options.

Before choosing a cybersecurity as a service provider, make sure you understand the full cost, including set-up fees, extra services and charges for changing the scope. Check the contract carefully for service levels, renewal dates, price increases and cancellation terms. It is also important to agree what happens if you leave: how your data and documentation will be returned or securely deleted, and how access to your systems will be removed. Clear terms and a practical exit plan can help you avoid unexpected costs and reduce disruption if you switch providers.

Ensure the provider supports your regulatory obligations.

Choose a cybersecurity as a service provider that understands the regulatory obligations relevant to your organisation and can help you meet them. Ask how its services support requirements for areas such as data protection, access controls, incident reporting and record-keeping, and request clear evidence of its processes and certifications where applicable. Confirm which responsibilities remain with your organisation, as outsourcing security does not transfer legal accountability.
Cyber Security Solutions for Small Businesses

Cyber security is not just a concern for large organisations. Small businesses hold valuable information, rely on digital services and often work with suppliers and customers who expect their data to be protected. A cyber incident can disrupt day-to-day operations, damage customer trust and lead to unexpected costs.

The good news is that effective protection does not have to mean a large security team or a complex technology stack. A practical set of measures, applied consistently, can reduce common risks and help a small business recover more quickly if something goes wrong.

Start with the risks that matter most

Before buying new tools, identify what the business needs to protect. This could include customer and employee information, financial records, email accounts, payment systems, business applications and the devices used to access them.

Make a simple list of your key systems and consider what would happen if each became unavailable, was accessed without permission or had its data stolen. This helps you prioritise spending and focus on realistic risks rather than trying to defend against every possible threat at once.

Use multi-factor authentication

Passwords can be stolen, guessed or reused across multiple services. Multi-factor authentication (MFA) adds another check when someone signs in, such as an approval on a mobile device or a security key. Enable MFA on business email, cloud services, remote access, financial platforms and administrator accounts wherever it is available.

Use unique, strong passwords for each account and consider a reputable password manager to help staff store them securely. Avoid shared accounts where possible: individual accounts make it easier to manage access and understand who has done what.

Keep devices and software up to date

Software updates often fix security weaknesses. Turn on automatic updates for operating systems, web browsers, business applications and mobile devices, and make sure updates are installed promptly. Replace software and equipment that no longer receive security updates, or limit their access until they can be replaced.

Keep an inventory of business devices and software so that nothing is overlooked. This should include laptops, phones, tablets, network equipment and any personal devices authorised for work use.

Protect computers and mobile devices

Use supported security software on business devices and ensure its protection is active and up to date. Modern operating systems include useful built-in security features, but these still need to be configured and monitored.

Set devices to lock automatically when unattended, encrypt them where possible and use a standard, non-administrator account for everyday work. Restrict administrator privileges to people who genuinely need them. If a device is lost or stolen, the business should be able to disable access to its accounts and, where appropriate, remotely erase business data.

Secure email and reduce phishing risk

Phishing messages try to persuade people to reveal information, open harmful attachments or make payments to the wrong account. Staff should be encouraged to pause before responding to unexpected requests, particularly those involving passwords, sensitive data or urgent payments.

Provide a simple way to report suspicious messages, and make sure staff know how to verify changes to supplier bank details or unusual payment instructions using a trusted contact method. Email security settings can also help protect against spoofed messages. Your email provider or IT support company can advise on appropriate domain protections.

Back up important information

Backups can help the business recover from accidental deletion, equipment failure, ransomware or other incidents. Decide which data and systems are essential, how often they should be backed up and how quickly they need to be restored.

Keep backups separate from the systems they protect, and restrict who can alter or delete them. Test the recovery process regularly: a backup is only useful if the business can restore the information when needed. Document where backups are stored and who is responsible for checking them.

Manage access carefully

Give employees access only to the information and systems required for their role. Review permissions periodically, especially for administrator accounts and systems containing sensitive data. Remove access promptly when someone leaves or changes role, and update shared credentials when necessary.

Where possible, use separate accounts for routine tasks and administration. This reduces the risk that a mistake or compromised account will have broad access across the business.

Secure your Wi-Fi and network

Change default passwords on routers and other network equipment, install firmware updates and use modern Wi-Fi security settings. If visitors need internet access, provide a separate guest network rather than sharing the network used for business devices.

Remote access should be protected with MFA and kept to a minimum. Avoid exposing internal systems directly to the internet unless there is a clear business need and suitable protection in place.

Prepare for an incident

No security measure can guarantee that an incident will never happen. A short incident response plan can help everyone act quickly and consistently. Include who to contact, how to isolate affected devices, how to access backups and how to communicate with staff, customers, suppliers and relevant authorities.

Keep important contact details available offline in case email or shared files are unavailable. Review the plan at least once a year and after significant changes to the business.

Check suppliers and cloud services

Small businesses often rely on external providers for email, accounting, payments, hosting and IT support. Understand what each provider is responsible for securing and what remains your responsibility. Use MFA, review access permissions and choose providers that can explain how they protect and back up your information.

Before sharing personal or commercially sensitive data, consider whether the supplier needs it and how it will be handled. Keep a record of important suppliers and know how to contact them if a service is affected.

Build security into everyday work

Staff awareness is an important part of cyber security. Give employees clear, practical guidance on passwords, phishing, data handling, device security and reporting concerns. Training should be ongoing and relevant to the work people actually do, rather than a one-off exercise.

Make it easy to report mistakes or suspicious activity without blame. Early reporting can help limit the impact of an incident.

Consider recognised guidance

UK small businesses can use guidance from the National Cyber Security Centre (NCSC) to review and improve their security practices. Cyber Essentials is a UK government-backed scheme that sets out baseline technical controls and may be useful when demonstrating security measures to customers or partners. Check the current scheme requirements to see whether certification is appropriate for your organisation.

Businesses handling personal data should also understand their responsibilities under UK data protection law. The Information Commissioner’s Office (ICO) provides guidance, but organisations should seek appropriate professional advice where their obligations are unclear.

A manageable first step

Begin with the basics: turn on MFA, update devices, protect and test backups, review who has access to key systems, and teach staff how to report suspicious activity. Assign responsibility for each task and set dates for regular reviews.

Cyber security is an ongoing process, not a one-time purchase. By taking practical steps and improving them over time, a small business can reduce its exposure to common threats and be better prepared to respond if an incident occurs.


Top 6 FAQs on Cyber Security Solutions for Small Businesses

  1. How do I set up security for my small business?
  2. What is the best cyber security method for small to medium businesses?
  3. How much does cybersecurity cost for a small business?
  4. What do small businesses need in cyber security?
  5. What are the solutions of cyber security?
  6. What are the solutions for cyber security for business?

How do I set up security for my small business?

Start by identifying the information, devices and services your business relies on, then put a few essential safeguards in place: use multi-factor authentication and unique passwords, install software updates promptly, protect devices with reputable security tools, limit staff access to what they need and back up important data regularly. Train your team to spot suspicious emails and report concerns, and make a simple plan for responding to an incident. Review these measures regularly, and seek advice from a trusted IT or cyber security provider if you need help tailoring them to your business.

What is the best cyber security method for small to medium businesses?

There is no single best cyber security method for every small or medium-sized business. A strong starting point is a layered approach: use multi-factor authentication, keep devices and software updated, protect and regularly test backups, restrict access to sensitive systems, and train staff to recognise and report suspicious activity. Prioritise measures based on the information and services your business depends on, and review them regularly as your risks change.

How much does cybersecurity cost for a small business?

The cost of cyber security for a small business depends on its size, the information it handles and the level of protection it needs. Basic measures—such as multi-factor authentication, software updates, secure backups and staff training—may be available at little or no extra cost, while paid security software, managed IT support, monitoring or formal certification can add to the budget. Start by addressing the most important risks, check what security features are already included in your existing services, and request clear, itemised quotes before committing. A proportionate investment in prevention and recovery can help reduce the potential cost of an incident.

What do small businesses need in cyber security?

Small businesses need a practical set of cyber security measures to protect their accounts, devices, data and day-to-day operations. Start with multi-factor authentication, strong unique passwords, regular software updates, reputable security software and restricted access to sensitive information. Keep secure, separate backups and test that data can be restored, train staff to recognise phishing, and have a simple plan for responding to incidents. The right measures depend on the business, so review key risks, essential systems and supplier security regularly.

What are the solutions of cyber security?

Cyber security solutions for a small business include multi-factor authentication and strong, unique passwords; regularly updated software and devices; anti-malware protection and secure firewalls; encrypted, tested backups; restricted access to business data; and staff training to spot phishing and other scams. The right combination depends on the business’s systems and risks, so begin with essential protections and review them regularly.

What are the solutions for cyber security for business?

Cyber security solutions for a business include multi-factor authentication, strong and unique passwords, regular software updates, security software, secure Wi-Fi and carefully managed access to systems and data. Businesses should also back up important information and test that it can be restored, train staff to recognise phishing attempts, and prepare a clear plan for responding to incidents. The right combination depends on the size of the business, the information it holds and the systems it uses, so start by identifying key risks and prioritising the protections that matter most.

Information Security Consulting Services: A Practical Guide

Information security is an essential part of running a modern organisation. Businesses rely on digital systems to store information, deliver services and communicate with customers, while facing risks such as phishing, ransomware, data theft and accidental disclosure. Information security consulting services help organisations understand these risks and put effective safeguards in place.

A consultant can provide specialist knowledge, an independent assessment and practical support. Whether an organisation needs to meet regulatory obligations, strengthen its defences or prepare for an incident, consulting can help turn security concerns into a clear programme of work.

What are information security consulting services?

Information security consulting services provide advice and hands-on assistance to help protect an organisation’s information, systems and operations. The scope can range from a focused review of a particular system to a broader security strategy covering people, processes, technology and suppliers.

Consultants may work with an organisation’s internal IT and security teams, senior leaders or compliance functions. Their recommendations should reflect the organisation’s size, sector, risk profile and available resources, rather than relying on a one-size-fits-all approach.

Common information security consulting services

Security risk assessments

A risk assessment identifies important information and systems, considers how they could be threatened, and evaluates the potential impact. The result is a prioritised view of security risks, helping decision-makers focus investment where it is most needed.

Security audits and reviews

An audit or review examines existing controls, policies and practices. This may include access management, system configuration, logging, backup arrangements, supplier oversight and incident procedures. The findings can highlight weaknesses and provide a basis for improvements.

Penetration testing and vulnerability assessments

Vulnerability assessments look for known weaknesses in systems and applications. Penetration testing goes further by safely testing whether selected weaknesses could be exploited. These activities should be properly scoped and authorised, with clear reporting and guidance on remediation.

Security strategy and planning

Consultants can help develop a security strategy that supports business objectives. This may include setting priorities, defining responsibilities, planning improvements and establishing measures to track progress. A practical roadmap can help organisations manage security work over time and avoid treating it as a series of disconnected projects.

Policies, standards and governance

Clear policies help staff understand how information should be handled and who is responsible for protecting it. Consultants may assist with developing or reviewing policies covering areas such as acceptable use, access control, data classification, remote working and supplier security.

Compliance support

Organisations may need to demonstrate that they meet legal, regulatory, contractual or industry requirements. A consultant can help interpret relevant obligations, assess existing controls and prepare evidence for audits or certifications. Compliance is not a substitute for security, but well-designed controls can support both.

Incident response and resilience

Security incidents can disrupt operations and put sensitive information at risk. Consulting support may include developing incident response plans, defining escalation routes, running exercises and reviewing recovery arrangements. Preparation helps teams respond more consistently when an incident occurs.

Security awareness and training

Staff behaviour can affect an organisation’s exposure to risk. Training can help employees recognise suspicious messages, protect credentials, handle information appropriately and report concerns quickly. Effective awareness programmes are relevant to people’s roles and reinforced regularly.

How a consulting engagement usually works

Although each engagement is different, the process often follows several stages:

  1. Scoping: The organisation and consultant agree the objectives, systems in scope, timescales and expected outputs.
  2. Discovery: The consultant gathers information through interviews, document reviews, technical analysis or workshops.
  3. Assessment: Existing controls and risks are evaluated against the agreed criteria and the organisation’s needs.
  4. Reporting: Findings are explained in clear language, with risks prioritised by significance and practical recommendations provided.
  5. Remediation: The organisation implements agreed changes. The consultant may provide advice or hands-on support.
  6. Follow-up: Progress is reviewed to confirm that actions have been completed and that improvements are working as intended.

A useful report should do more than list technical weaknesses. It should explain why each issue matters, what should be done, who should take ownership and, where possible, how urgently the action should be addressed.

Benefits for organisations

Information security consulting can help organisations:

  • Gain an independent view of their security posture.
  • Identify and prioritise risks before they lead to disruption or loss.
  • Make better-informed decisions about security investment.
  • Improve readiness for audits, regulatory reviews and customer assessments.
  • Strengthen incident response and business continuity planning.
  • Access specialist expertise that may not be available in-house.

Consulting is most effective when recommendations are realistic and supported by the organisation’s leadership. A report alone does not reduce risk; value comes from acting on the findings and maintaining the controls over time.

Choosing an information security consultant

When selecting a consultant or consultancy, consider the following:

  • Relevant experience: Look for experience with organisations, technologies and challenges similar to yours.
  • Clear methods: Ask how the work will be conducted, what standards or frameworks may be used, and how findings will be validated.
  • Practical recommendations: Advice should be prioritised, understandable and achievable within your operating environment.
  • Communication: Consultants should be able to explain technical risks to both specialists and business leaders.
  • Independence and confidentiality: Confirm how conflicts of interest, sensitive information and access to systems will be managed.
  • Defined deliverables: Agree what the engagement will produce, including reports, presentations, action plans or follow-up support.

It is also important to agree the limits of the work. For example, a security assessment only covers the systems, locations and time period included in its scope. Confirming these details in advance helps prevent misunderstandings.

Making consulting part of an ongoing security programme

Information security is not a one-off project. Systems change, employees join and leave, suppliers evolve, and new threats emerge. Organisations should review risks regularly, assign responsibility for actions and check that key controls remain effective.

Information security consulting services can provide the expertise and structure needed to make those improvements. With a clear scope, realistic recommendations and committed follow-through, organisations can build stronger defences, improve resilience and make more confident decisions about protecting their information.


Essential Tips for Choosing the Right Information Security Consulting Services

  1. Define your security goals before engaging a consultant.
  2. Check the consultant’s relevant certifications and experience.
  3. Ask for a clear scope, timeline and deliverables.
  4. Ensure recommendations fit your organisation’s risks.
  5. Confirm how sensitive information will be protected.
  6. Request practical actions, not just a findings report.
  7. Agree how progress and success will be measured.
  8. Check references from similar organisations.
  9. Review the engagement regularly as risks change.

Define your security goals before engaging a consultant.

Before engaging an information security consultant, define what you want to achieve. Your goals might include assessing cyber risks, preparing for a compliance audit, improving incident response or protecting a particular system or type of data. Clear objectives help the consultant shape the scope of work, recommend relevant services and provide useful, measurable outcomes. They also make it easier to agree priorities, timescales and budget from the outset.

Check the consultant’s relevant certifications and experience.

Before appointing an information security consultant, check that their certifications and experience match your organisation’s needs. Relevant, current qualifications can demonstrate specialist knowledge, while experience in your sector or with similar systems can help ensure their advice is practical and appropriate. Ask about previous projects, the methods they use and the outcomes they have achieved, and verify any credentials where possible.

Ask for a clear scope, timeline and deliverables.

Before appointing an information security consultant, agree a clear scope, timeline and set of deliverables. Define which systems, locations and risks are included, when each stage will take place, and what you will receive—such as a findings report, prioritised recommendations or an action plan. This helps everyone understand their responsibilities, keeps the work focused and makes it easier to assess progress and value.

Ensure recommendations fit your organisation’s risks.

Choose recommendations that reflect your organisation’s specific risks, priorities and resources. A consultant should consider factors such as the information you hold, the systems you rely on, relevant regulations and the impact a security incident could have on your operations. This helps ensure that advice is practical and proportionate, so you can focus on the measures that will make the greatest difference rather than adopting controls that do not suit your needs.

Confirm how sensitive information will be protected.

Before sharing information with a consultant, confirm how sensitive data will be protected throughout the engagement. Ask how it will be collected, stored, accessed, transferred and securely deleted, and who will be authorised to handle it. Check that appropriate confidentiality agreements and security measures are in place, and clarify whether any information will be shared with subcontractors or stored outside the UK. These steps help protect your organisation’s data and set clear expectations from the outset.

Request practical actions, not just a findings report.

When engaging an information security consultant, ask for practical, prioritised actions alongside the findings report. Each recommendation should explain the risk it addresses, what needs to change, who should take responsibility and how urgently it should be done. This makes the results easier to turn into a realistic improvement plan, rather than leaving your team with a list of problems but no clear route to resolving them.

Agree how progress and success will be measured.

Agree how progress and success will be measured before the engagement begins. Set clear, practical measures linked to the work, such as completing priority actions by agreed dates, reducing identified risks, improving incident-response times or meeting relevant compliance requirements. Decide how often progress will be reviewed, who is responsible for providing updates and what evidence will demonstrate that changes are working. This helps everyone share the same expectations and keeps the focus on lasting improvements, rather than simply completing a report.

Check references from similar organisations.

Before choosing an information security consultant, ask for references from organisations with a similar size, sector or security needs. Their experience can help you assess whether the consultant communicates clearly, delivers practical recommendations and understands challenges like yours. Where possible, ask about the results of the engagement and how well the consultant handled sensitive information.

Review the engagement regularly as risks change.

Review your information security consulting engagement regularly to ensure it still reflects your organisation’s needs. Risks can change as technology, business operations, suppliers and threats evolve, so revisit the scope, priorities and recommendations with your consultant. Regular reviews help identify new areas of concern, adjust the work accordingly and keep security advice relevant and effective.

Enhancing Security with Managed Cybersecurity Services: Safeguarding Your Business in the Digital Age

Managed Cybersecurity Services

The Importance of Managed Cybersecurity Services

In today’s digital age, where cyber threats are constantly evolving and becoming more sophisticated, the need for robust cybersecurity measures is paramount. Many businesses, regardless of their size or industry, are turning to managed cybersecurity services to protect their valuable data and systems from cyber attacks.

What are Managed Cybersecurity Services?

Managed cybersecurity services involve outsourcing the management of an organisation’s security processes to a third-party provider. These services typically include continuous monitoring, threat detection, incident response, and security updates to ensure that a company’s IT infrastructure remains secure.

The Benefits of Managed Cybersecurity Services

Enhanced Security: Managed cybersecurity services employ advanced tools and technologies to detect and prevent cyber threats in real-time, providing a higher level of security than traditional in-house solutions.

Cost-Effective: Outsourcing cybersecurity services can be more cost-effective for businesses compared to maintaining an in-house security team. Managed services allow companies to access expert security professionals without the need for additional hiring and training costs.

Proactive Monitoring: Managed cybersecurity services offer round-the-clock monitoring of networks and systems, allowing for early detection of potential security breaches before they escalate into major incidents.

Compliance Assistance: Many managed security service providers help businesses comply with industry regulations and standards by implementing appropriate security controls and conducting regular audits.

Choosing the Right Provider

When selecting a managed cybersecurity service provider, it is essential to consider factors such as experience, reputation, range of services offered, and scalability. A reputable provider should have a proven track record in delivering effective security solutions tailored to the specific needs of your business.

Conclusion

Managed cybersecurity services play a crucial role in safeguarding businesses against the ever-growing threat landscape of cyber attacks. By entrusting your security needs to experienced professionals, you can focus on your core business activities with the peace of mind that your digital assets are protected.


Understanding Managed Cybersecurity Services: Key Concepts and FAQs

  1. What are the 5 security services in cyber security?
  2. What are managed security services?
  3. What is cyber security management?
  4. What is the difference between managed security services and cyber security services?
  5. What are managed soc services?
  6. Who is the largest MSSP?

What are the 5 security services in cyber security?

In the realm of cybersecurity, there are five key security services that play a significant role in safeguarding organisations against cyber threats. These services include threat intelligence, vulnerability management, incident response, access management, and security awareness training. Threat intelligence involves monitoring and analysing potential threats to proactively protect systems. Vulnerability management focuses on identifying and addressing weaknesses in IT infrastructures. Incident response is crucial for swiftly reacting to security breaches. Access management ensures that only authorised individuals have appropriate access to resources. Lastly, security awareness training educates employees on best practices to mitigate risks and enhance overall security posture.

What are managed security services?

Managed security services refer to the outsourcing of cybersecurity functions to a third-party provider who takes responsibility for monitoring, managing, and enhancing an organisation’s security posture. These services typically include threat detection, incident response, security updates, and compliance management to ensure that a company’s IT infrastructure remains protected from cyber threats. By utilising managed security services, businesses can benefit from advanced technologies, expert security professionals, and round-the-clock monitoring to proactively safeguard their digital assets and mitigate risks effectively.

What is cyber security management?

Cybersecurity management encompasses the strategic planning, implementation, and monitoring of security measures to protect digital assets from cyber threats. It involves a proactive approach to identifying vulnerabilities, assessing risks, and deploying appropriate controls to mitigate potential attacks. Effective cybersecurity management includes tasks such as creating security policies, conducting risk assessments, implementing security technologies, monitoring network activity, and responding to incidents promptly. By adopting a comprehensive cybersecurity management strategy, organisations can strengthen their defences against cyber threats and safeguard their sensitive information from malicious actors.

What is the difference between managed security services and cyber security services?

When considering the distinction between managed security services and cybersecurity services, it is important to understand that managed security services encompass a broader range of offerings. Managed security services typically involve outsourcing the monitoring and management of an organisation’s security infrastructure to a third-party provider. On the other hand, cybersecurity services focus specifically on protecting digital systems, networks, and data from cyber threats. While cybersecurity services may include elements of managed security, they are more narrowly focused on safeguarding against cyber attacks through measures such as risk assessments, penetration testing, and incident response. In essence, managed security services provide ongoing support and oversight of security operations, while cybersecurity services concentrate on proactively defending against digital threats.

What are managed soc services?

Managed SOC (Security Operations Centre) services refer to outsourcing the monitoring, detection, and response to cybersecurity incidents to a third-party provider. A Managed SOC team typically operates 24/7 and utilises advanced technologies to continuously monitor an organisation’s network for suspicious activities, analyse security alerts, and respond to potential threats promptly. By leveraging the expertise of a Managed SOC service provider, businesses can enhance their security posture, detect and mitigate cyber threats more effectively, and improve overall incident response capabilities.

Who is the largest MSSP?

When it comes to the frequently asked question of “Who is the largest Managed Security Service Provider (MSSP)?” in the cybersecurity industry, the answer can vary depending on different metrics such as revenue, client base, or global presence. Several well-known companies, including IBM Security, SecureWorks, Trustwave, and Symantec, are often recognised as some of the largest MSSPs in terms of market share and industry reputation. These leading MSSPs offer a wide range of cybersecurity services tailored to meet the diverse needs of businesses seeking comprehensive security solutions and proactive threat management.

Enhancing Security with Managed Cybersecurity Solutions

The Importance of Managed Cybersecurity Services

The Importance of Managed Cybersecurity Services

In today’s digital age, where cyber threats are constantly evolving and becoming more sophisticated, businesses and organisations face a significant challenge in protecting their sensitive data and IT infrastructure. Managed cybersecurity services have emerged as a crucial solution to address these challenges effectively.

What are Managed Cybersecurity Services?

Managed cybersecurity services involve outsourcing the management of an organisation’s security processes to a third-party provider. These services typically include round-the-clock monitoring, threat detection, incident response, vulnerability assessments, and security updates.

The Benefits of Managed Cybersecurity Services

Proactive Protection: Managed cybersecurity services employ advanced tools and technologies to proactively monitor for potential security threats and vulnerabilities before they can cause harm.

Expertise and Experience: By partnering with a managed cybersecurity service provider, businesses can access a team of highly skilled security professionals with expertise in the latest cyber threats and best practices.

Cost-Effectiveness: Outsourcing cybersecurity management can be more cost-effective than hiring an in-house security team, as it eliminates the need for investing in training, tools, and infrastructure.

Compliance Assistance: Managed cybersecurity services help organisations comply with industry regulations and standards by ensuring that security measures are in place to protect sensitive data.

Choosing the Right Provider

When selecting a managed cybersecurity service provider, it is essential to consider factors such as reputation, experience, service offerings, scalability, and customer support. A trusted provider will work closely with your organisation to tailor solutions that meet your specific security needs.

Conclusion

Managed cybersecurity services play a vital role in safeguarding businesses against cyber threats and ensuring the continuity of operations. By entrusting security management to experienced professionals, organisations can focus on their core activities while having peace of mind knowing that their digital assets are protected.


Essential Tips for Strengthening Your Managed Cybersecurity Strategy

  1. Regularly update all software and systems to patch security vulnerabilities.
  2. Implement strong password policies and use multi-factor authentication where possible.
  3. Train employees on cybersecurity best practices to prevent social engineering attacks.
  4. Encrypt sensitive data both in transit and at rest to protect it from unauthorized access.
  5. Monitor network traffic for any unusual activity that could indicate a security breach.
  6. Backup data regularly and store backups in a secure offsite location to prevent data loss.
  7. Conduct regular security assessments and penetration testing to identify potential weaknesses.
  8. Establish incident response procedures to quickly respond to and mitigate cybersecurity incidents.

Regularly update all software and systems to patch security vulnerabilities.

Regularly updating all software and systems is a fundamental tip in managed cybersecurity to patch security vulnerabilities effectively. By staying current with software updates, organisations can address known vulnerabilities and protect their systems from potential cyber threats. These updates often include patches that fix security flaws identified by software developers or security researchers, making it essential for maintaining a strong defence against malicious attacks. Prioritising regular updates as part of a proactive cybersecurity strategy is crucial in safeguarding sensitive data and ensuring the overall integrity of IT infrastructure.

Implement strong password policies and use multi-factor authentication where possible.

Implementing strong password policies and utilising multi-factor authentication where feasible are fundamental steps in bolstering cybersecurity measures. Strong passwords, comprising a mix of alphanumeric characters and symbols, act as the first line of defence against unauthorised access. Multi-factor authentication provides an additional layer of security by requiring users to verify their identity through multiple means, such as a password combined with a unique code sent to their mobile device. By adhering to these practices, organisations can significantly reduce the risk of data breaches and enhance overall protection of sensitive information.

Train employees on cybersecurity best practices to prevent social engineering attacks.

Training employees on cybersecurity best practices is a crucial aspect of preventing social engineering attacks. By educating staff on how to recognise and respond to suspicious emails, phone calls, or messages, organisations can significantly reduce the risk of falling victim to social engineering tactics. Empowering employees with the knowledge to identify potential threats and exercise caution when sharing sensitive information online can enhance the overall security posture of the company and mitigate the impact of cyber attacks.

Encrypt sensitive data both in transit and at rest to protect it from unauthorized access.

To enhance the security of sensitive data, it is crucial to encrypt it both in transit and at rest. Encrypting data in transit ensures that information remains secure while being transferred between devices or networks, preventing interception by malicious actors. Similarly, encrypting data at rest safeguards it when stored on servers, databases, or other storage devices, making it unreadable to unauthorised users even if they gain access to the physical storage medium. By implementing robust encryption measures, organisations can significantly reduce the risk of unauthorised access and protect their valuable data from potential breaches.

Monitor network traffic for any unusual activity that could indicate a security breach.

Monitoring network traffic for any unusual activity is a critical aspect of managed cybersecurity. By regularly analysing network data, organisations can detect anomalies that may signal a security breach or potential threat. Unusual spikes in traffic, unauthorized access attempts, or suspicious patterns can be early indicators of malicious activity. Implementing robust network monitoring tools and practices allows businesses to proactively identify and respond to security incidents, helping to safeguard sensitive data and maintain the integrity of their IT infrastructure.

Backup data regularly and store backups in a secure offsite location to prevent data loss.

Backing up data regularly and storing backups in a secure offsite location is a fundamental tip in managed cybersecurity. In the event of a cyber attack, natural disaster, or hardware failure, having secure and up-to-date backups ensures that critical data can be restored swiftly, minimising the risk of data loss and operational downtime. By following this practice, organisations can enhance their resilience against unforeseen incidents and maintain business continuity with minimal disruption.

Conduct regular security assessments and penetration testing to identify potential weaknesses.

Conducting regular security assessments and penetration testing is a crucial tip in managed cybersecurity. By proactively evaluating the security measures in place and simulating real-world cyber attacks, organisations can identify potential weaknesses in their IT infrastructure and applications. This proactive approach allows businesses to address vulnerabilities before they are exploited by malicious actors, enhancing the overall resilience of their cybersecurity defences. Regular assessments and testing help ensure that security measures remain effective in safeguarding sensitive data and maintaining the integrity of the organisation’s digital assets.

Establish incident response procedures to quickly respond to and mitigate cybersecurity incidents.

Establishing robust incident response procedures is a critical component of effective managed cybersecurity. By defining clear protocols and workflows for responding to cybersecurity incidents, organisations can swiftly detect, contain, and mitigate potential threats. A well-prepared incident response plan helps minimise the impact of security breaches, reduces downtime, and enhances overall resilience against cyber attacks. With structured procedures in place, businesses can act promptly to address security incidents, protect sensitive data, and maintain the trust of their stakeholders in the face of evolving cyber threats.

Enhancing Data Protection: The Ultimate Information Security Solution Guide

The Importance of Information Security Solutions

The Importance of Information Security Solutions

In today’s digital age, where data breaches and cyber-attacks are becoming increasingly common, the need for robust information security solutions has never been more critical. Businesses of all sizes and industries are facing constant threats to their sensitive information, making it essential to invest in comprehensive security measures.

Information security solutions encompass a range of technologies, processes, and practices designed to protect data from unauthorised access, disclosure, disruption, modification or destruction. These solutions play a vital role in safeguarding confidential information, maintaining the integrity of systems, and ensuring business continuity.

Key Components of Information Security Solutions:

  • Firewalls: Firewalls act as a barrier between a trusted internal network and untrusted external networks, monitoring and controlling incoming and outgoing network traffic based on predetermined security rules.
  • Encryption: Encryption converts data into a code to prevent unauthorised access. It ensures that even if data is intercepted, it remains unreadable without the decryption key.
  • Antivirus Software: Antivirus software detects and removes malicious software such as viruses, worms, and trojans from computer systems to prevent damage and data loss.
  • Intrusion Detection Systems (IDS): IDS monitor network traffic for suspicious activity or policy violations. They alert IT administrators when potential threats are detected.
  • Access Control Systems: Access control systems regulate who can access certain resources within an organisation. This includes user authentication mechanisms like passwords, biometrics, and multi-factor authentication.

The Benefits of Implementing Information Security Solutions:

By investing in information security solutions, businesses can enjoy a myriad of benefits:

  • Data Protection: Protect sensitive data from unauthorised access or theft.
  • Compliance: Ensure compliance with industry regulations and standards regarding data protection.
  • Business Continuity: Minimise downtime due to cyber incidents by safeguarding critical systems and information.
  • Credibility: Build trust with customers by demonstrating a commitment to protecting their data.
  • Cost Savings: Avoid financial losses associated with data breaches by proactively securing systems.

In conclusion, information security solutions are indispensable in today’s digital landscape. By implementing robust security measures tailored to their specific needs, businesses can mitigate risks, protect valuable assets, and maintain a competitive edge in an increasingly connected world.


8 Key Benefits of Implementing an Information Security Solution

  1. Protect sensitive data from unauthorised access
  2. Prevent costly data breaches and cyber-attacks
  3. Ensure compliance with industry regulations and standards
  4. Maintain business continuity by safeguarding critical systems
  5. Enhance customer trust and credibility
  6. Mitigate financial losses associated with security incidents
  7. Improve overall system performance and reliability
  8. Stay ahead of evolving cybersecurity threats


Challenges and Drawbacks of Implementing Information Security Solutions

  1. Costly implementation and maintenance of security solutions can strain a company’s budget.
  2. Complexity of security measures may require specialised knowledge and training for effective deployment.
  3. Over-reliance on technology-based solutions can lead to a false sense of security, overlooking human error and social engineering tactics.
  4. Integration challenges may arise when trying to implement multiple security solutions across different systems and platforms.
  5. Security solutions can sometimes cause performance issues or slow down system processes, impacting productivity.
  6. Constantly evolving threats mean that security solutions need regular updates and upgrades to remain effective, adding to the workload of IT teams.
  7. Intrusive security measures such as strict access controls can hinder user convenience and workflow efficiency.

Protect sensitive data from unauthorised access

One of the key advantages of implementing information security solutions is the ability to protect sensitive data from unauthorised access. By utilising encryption, access control systems, and other security measures, organisations can safeguard confidential information such as customer records, financial data, and intellectual property from cyber threats. This proactive approach not only helps prevent data breaches and theft but also instils trust among stakeholders by demonstrating a commitment to maintaining the privacy and integrity of sensitive data.

Prevent costly data breaches and cyber-attacks

One of the key advantages of implementing information security solutions is the ability to prevent costly data breaches and cyber-attacks. By proactively securing sensitive data and systems, businesses can significantly reduce the risk of falling victim to malicious activities that could result in financial losses, reputational damage, and legal implications. Investing in robust security measures not only protects valuable assets but also ensures business continuity by mitigating the disruptive impact of cyber incidents. Prioritising information security is essential in safeguarding against potential threats and maintaining the trust of customers and stakeholders in an increasingly digital environment.

Ensure compliance with industry regulations and standards

Ensuring compliance with industry regulations and standards is a crucial benefit of information security solutions. By implementing robust security measures that align with regulatory requirements, businesses can demonstrate their commitment to data protection and privacy. Compliance not only helps in avoiding costly fines and legal consequences but also builds trust with customers and stakeholders. Adhering to industry standards ensures that sensitive information is handled responsibly, fostering a culture of transparency and accountability within the organisation.

Maintain business continuity by safeguarding critical systems

The implementation of information security solutions plays a crucial role in maintaining business continuity by safeguarding critical systems. By ensuring the integrity and availability of essential IT infrastructure, businesses can mitigate the risk of downtime caused by cyber incidents such as data breaches or system failures. This proactive approach not only protects valuable assets and sensitive information but also helps organisations to operate smoothly and efficiently, even in the face of potential threats. The ability to keep critical systems secure and operational is paramount for sustaining business operations and meeting customer expectations in today’s digital landscape.

Enhance customer trust and credibility

Incorporating information security solutions can significantly enhance customer trust and credibility for businesses. By demonstrating a commitment to safeguarding sensitive data through robust security measures, organisations instil confidence in their customers that their information is being handled responsibly and securely. This proactive approach not only helps build trust with existing customers but also attracts new ones who prioritise data protection and privacy. Ultimately, investing in information security solutions not only protects the business from potential breaches but also reinforces its reputation as a trustworthy and reliable entity in the eyes of its clientele.

Mitigate financial losses associated with security incidents

Implementing robust information security solutions can significantly mitigate financial losses associated with security incidents. By proactively safeguarding sensitive data and critical systems, businesses can reduce the risk of costly breaches, cyber-attacks, or data theft. Investing in technologies such as firewalls, encryption, and intrusion detection systems not only protects valuable assets but also helps avoid the substantial financial repercussions that often accompany security breaches. Effective information security measures can save organisations from the devastating impact of monetary losses, legal liabilities, reputational damage, and operational disruptions caused by security incidents.

Improve overall system performance and reliability

Implementing information security solutions can significantly enhance overall system performance and reliability. By implementing measures such as firewalls, intrusion detection systems, and regular security updates, organisations can reduce the risk of cyber threats that may compromise system integrity. This proactive approach not only safeguards sensitive data but also ensures that systems operate smoothly without interruptions caused by malicious activities. Improved system performance leads to enhanced efficiency and productivity, allowing businesses to focus on their core operations with confidence in the reliability of their IT infrastructure.

Stay ahead of evolving cybersecurity threats

In today’s rapidly evolving digital landscape, one of the key advantages of implementing information security solutions is the ability to stay ahead of constantly changing cybersecurity threats. By proactively investing in advanced security measures such as threat detection systems, regular vulnerability assessments, and employee training programmes, organisations can effectively identify and mitigate emerging risks before they escalate into full-fledged cyber-attacks. This proactive approach not only enhances the overall resilience of the IT infrastructure but also ensures that businesses are well-prepared to tackle new and sophisticated threats in real-time, safeguarding sensitive data and maintaining operational continuity.

Costly implementation and maintenance of security solutions can strain a company’s budget.

The implementation and maintenance of information security solutions can present a significant challenge for companies due to the associated costs. Investing in robust security measures often requires a substantial financial commitment, which can strain a company’s budget, particularly for small and medium-sized enterprises. From purchasing hardware and software to training staff and conducting regular updates, the expenses involved in maintaining effective security solutions can quickly add up. Balancing the need for comprehensive protection with budgetary constraints is a delicate task that many organisations face, highlighting the conundrum of managing the financial implications of safeguarding sensitive information in today’s cyber-threat landscape.

Complexity of security measures may require specialised knowledge and training for effective deployment.

The complexity of security measures within information security solutions can present a significant challenge, as their effective deployment often necessitates specialised knowledge and training. Managing intricate technologies such as firewalls, encryption protocols, and intrusion detection systems requires a deep understanding of cybersecurity principles and best practices. Without the appropriate expertise, organisations may struggle to configure these tools optimally, leaving their systems vulnerable to potential threats. Investing in ongoing training and upskilling for IT professionals is crucial to ensure that security measures are implemented correctly and maintained effectively to safeguard valuable data assets.

Over-reliance on technology-based solutions can lead to a false sense of security, overlooking human error and social engineering tactics.

An inherent con of information security solutions lies in the potential for organisations to develop an over-reliance on technology-based measures, inadvertently fostering a false sense of security. By placing excessive trust in automated systems and tools, businesses may overlook the critical factors of human error and social engineering tactics. Despite the sophistication of technological defences, the weakest link often remains human behaviour, making employees susceptible to manipulation and exploitation by cybercriminals. This oversight highlights the importance of integrating comprehensive training programmes and awareness initiatives alongside technological solutions to fortify overall information security posture effectively.

Integration challenges may arise when trying to implement multiple security solutions across different systems and platforms.

Integrating multiple security solutions across diverse systems and platforms can present a significant challenge in the realm of information security. The complexity arises from ensuring seamless communication and compatibility between various tools, each designed to address specific threats or vulnerabilities. Coordinating the deployment of these solutions while maintaining system functionality and performance can be a daunting task for organisations. Misconfigurations or conflicts during integration may lead to gaps in security coverage, leaving potential vulnerabilities exposed. Overcoming these integration challenges requires meticulous planning, expertise, and ongoing maintenance to ensure a cohesive and effective security posture across the entire IT infrastructure.

Security solutions can sometimes cause performance issues or slow down system processes, impacting productivity.

Security solutions, while essential for safeguarding sensitive information, can inadvertently introduce performance issues that hinder system processes and productivity. The additional layers of security protocols, encryption processes, and monitoring mechanisms implemented by these solutions can sometimes lead to delays in data processing and system responsiveness. This slowdown in performance may frustrate users, disrupt workflow efficiency, and potentially impact overall productivity within an organisation. Striking a balance between robust security measures and maintaining optimal system performance is crucial to ensure that information security solutions do not impede daily operations.

Constantly evolving threats mean that security solutions need regular updates and upgrades to remain effective, adding to the workload of IT teams.

In the realm of information security solutions, a significant drawback arises from the ever-evolving nature of cyber threats. The continuous emergence of new and sophisticated attack methods necessitates regular updates and upgrades to security measures in order to effectively combat these evolving risks. This ongoing need for maintenance adds a considerable workload to IT teams, requiring them to stay vigilant, proactive, and dedicated to keeping security systems up-to-date and resilient against the latest threats. Balancing the demands of day-to-day operations with the imperative task of maintaining robust security measures can place a strain on IT resources and personnel, highlighting a challenging aspect of managing information security in today’s dynamic threat landscape.

Intrusive security measures such as strict access controls can hinder user convenience and workflow efficiency.

Intrusive security measures, such as implementing strict access controls, can present a significant con in information security solutions by potentially impeding user convenience and workflow efficiency. While these measures are essential for safeguarding sensitive data and preventing unauthorised access, overly restrictive access controls may create barriers for users, leading to frustration and hindering productivity. Balancing robust security protocols with user-friendly practices is crucial to ensure that information remains protected without compromising the usability and efficiency of daily operations within an organisation.

The Benefits of SailPoint Single Sign-On for Enhanced Security and User Experience

In today’s digital age, where multiple applications and systems are integral to daily business operations, managing user access efficiently and securely is paramount. This is where SailPoint Single Sign-On (SSO) comes into play, offering a comprehensive solution that simplifies access management while bolstering security measures.

Streamlined User Experience

SailPoint SSO enables users to access multiple applications and systems with just one set of login credentials. This eliminates the need to remember numerous passwords, leading to a more streamlined and user-friendly experience. With SSO, users can seamlessly navigate between different platforms without the hassle of repeated logins, ultimately boosting productivity.

Enhanced Security Measures

Security breaches and data leaks are significant concerns for organisations of all sizes. SailPoint SSO enhances security by centralising user authentication processes. By consolidating access control into a single system, SSO reduces the risk of password-related vulnerabilities and unauthorised access. Additionally, administrators can implement multi-factor authentication and other advanced security measures to fortify the authentication process further.

Improved Compliance Management

Compliance with industry regulations such as GDPR, HIPAA, or PCI-DSS is non-negotiable for many businesses. SailPoint SSO simplifies compliance management by providing detailed audit trails and reporting capabilities. Organisations can easily track user activities across various applications, ensuring adherence to regulatory requirements and internal policies.

Cost-Efficiency and Scalability

Implementing SailPoint SSO can lead to cost savings in the long run. By reducing password-related helpdesk requests and minimising the risk of security incidents, organisations can lower operational costs associated with access management. Furthermore, as businesses grow and evolve, SailPoint SSO offers scalability to accommodate changing user needs without compromising security or efficiency.

Conclusion

SailPoint Single Sign-On is a powerful solution that not only enhances user experience but also strengthens security measures within an organisation. By streamlining access management processes, improving compliance management, and offering cost-efficient scalability, SailPoint SSO empowers businesses to navigate the complexities of modern IT environments with confidence.

Embrace the future of secure access management with SailPoint Single Sign-On.


Top 7 Tips for Optimising SailPoint Single Sign-On Security and Efficiency

  1. Ensure proper configuration of user authentication methods.
  2. Regularly review and update access policies and permissions.
  3. Implement multi-factor authentication for added security.
  4. Monitor user activities and access logs for any suspicious behaviour.
  5. Integrate SailPoint with other identity management systems for seamless operations.
  6. Provide adequate training to users on how to use Single Sign-On effectively.
  7. Perform regular audits to ensure compliance with security standards.

Ensure proper configuration of user authentication methods.

To maximise the effectiveness of SailPoint Single Sign-On, it is crucial to ensure the proper configuration of user authentication methods. By carefully setting up authentication protocols such as multi-factor authentication, biometric verification, or one-time passwords, organisations can significantly enhance the security of their access management processes. Properly configured user authentication methods not only strengthen the overall security posture but also provide users with a seamless and secure login experience across various applications and systems.

Regularly review and update access policies and permissions.

To ensure the effectiveness of SailPoint Single Sign-On, it is crucial to regularly review and update access policies and permissions. By conducting routine audits of user access rights, organisations can identify and address any discrepancies or potential security risks promptly. Updating access policies in line with changing business requirements and employee roles helps maintain a secure and efficient authentication process. This proactive approach not only enhances data protection but also ensures that users have the appropriate level of access to perform their roles effectively within the system.

Implement multi-factor authentication for added security.

Enhance the security of your SailPoint Single Sign-On implementation by incorporating multi-factor authentication. By requiring users to provide multiple forms of verification before accessing applications and systems, such as a password combined with a unique code sent to their mobile device, you significantly reduce the risk of unauthorised access and data breaches. Multi-factor authentication adds an extra layer of protection to sensitive information, ensuring that only authorised individuals can gain entry, thereby bolstering the overall security posture of your organisation.

Monitor user activities and access logs for any suspicious behaviour.

Monitoring user activities and access logs for any suspicious behaviour is a crucial tip when utilising SailPoint Single Sign-On. By keeping a close eye on user interactions within the system and regularly reviewing access logs, organisations can quickly identify any anomalies or potential security threats. Detecting unusual patterns or unauthorised access attempts early on allows for prompt intervention, mitigating the risk of data breaches and ensuring the integrity of the IT environment. Proactive monitoring not only enhances security but also demonstrates a commitment to maintaining a robust defence against cyber threats in today’s digital landscape.

Integrate SailPoint with other identity management systems for seamless operations.

To maximise the efficiency and effectiveness of SailPoint Single Sign-On, it is highly recommended to integrate SailPoint with other identity management systems. By seamlessly connecting SailPoint with existing identity management solutions, organisations can achieve a unified and cohesive approach to access management. This integration facilitates streamlined operations, enhances user experience, and strengthens security measures by leveraging the combined capabilities of different systems. Ultimately, integrating SailPoint with other identity management systems paves the way for a seamless and comprehensive access management strategy that optimises productivity and fortifies data protection across the organisation.

Provide adequate training to users on how to use Single Sign-On effectively.

To maximise the benefits of SailPoint Single Sign-On, it is crucial to provide users with adequate training on how to utilise the system effectively. By offering comprehensive training sessions, organisations can ensure that users understand the functionality of SSO, how to navigate between applications seamlessly, and best practices for maintaining security. Empowering users with the knowledge and skills to leverage SailPoint SSO not only enhances their user experience but also contributes to a more secure and efficient access management environment overall.

Perform regular audits to ensure compliance with security standards.

Performing regular audits is a crucial aspect of maintaining compliance with security standards when utilising SailPoint Single Sign-On. These audits help organisations to assess the effectiveness of their access management policies, identify any potential vulnerabilities or non-compliance issues, and take proactive measures to address them. By conducting frequent audits, businesses can ensure that their SailPoint SSO implementation remains robust, secure, and aligned with industry best practices, ultimately enhancing overall security posture and reducing the risk of data breaches.

The Power of Enablon GRC: Streamlining Governance, Risk, and Compliance

In today’s complex business landscape, organisations face a myriad of challenges when it comes to managing governance, risk, and compliance (GRC) requirements. Ensuring regulatory compliance, mitigating risks, and maintaining operational efficiency are crucial for sustainable business success. This is where Enablon GRC comes into play as a comprehensive solution to streamline and enhance GRC processes.

What is Enablon GRC?

Enablon GRC is a leading software platform that empowers organisations to effectively manage their GRC initiatives in a unified manner. By integrating governance, risk management, and compliance functions into a single platform, Enablon GRC enables businesses to centralise their processes, data, and reporting for improved visibility and control.

The Benefits of Enablon GRC

Enablon GRC offers a wide range of benefits that help organisations optimise their GRC activities:

  • Centralised Data Management: By consolidating all GRC-related information in one place, Enablon GRC eliminates data silos and provides a holistic view of risks and compliance status.
  • Risk Mitigation: The platform facilitates proactive risk identification and assessment, enabling organisations to implement mitigation strategies effectively.
  • Compliance Automation: With automated workflows and monitoring capabilities, Enablon GRC simplifies compliance management processes and ensures adherence to regulations.
  • Reporting and Analytics: Enablon GRC offers robust reporting tools that enable stakeholders to generate customised reports on key performance indicators (KPIs) and trends for informed decision-making.
  • Audit Trail Transparency: The platform maintains an audit trail of all activities within the system, enhancing accountability and transparency across the organisation.

Use Cases of Enablon GRC

Organisations across various industries can leverage Enablon GRC to address specific GRC challenges:

  • Financial Services: Financial institutions can use Enablon GRC to ensure regulatory compliance with stringent industry standards such as Basel III or GDPR.
  • Healthcare: Healthcare providers can utilise the platform to manage data privacy regulations like HIPAA while enhancing patient safety through effective risk management.
  • Manufacturing: Manufacturing companies can streamline environmental health and safety (EHS) compliance efforts with Enablon GRC’s EHS management capabilities.

The Future of Enablon GRC

As regulatory requirements continue to evolve and businesses face increasing scrutiny over their operations, the role of Enablon GRC will become even more critical. The platform’s adaptability and scalability make it well-positioned to meet the changing needs of organisations seeking robust GRC solutions in an ever-changing business environment.

In conclusion, Enablon GRC stands as a powerful tool for organisations looking to enhance their governance, risk management, and compliance practices. By leveraging its capabilities, businesses can navigate the complexities of the modern regulatory landscape with confidence and efficiency.


Understanding Enablon GRC: Key Features, Benefits, and Customisation for Governance, Risk, and Compliance

  1. What is Enablon GRC and what does it stand for?
  2. How can Enablon GRC help streamline governance, risk, and compliance processes?
  3. What are the key benefits of implementing Enablon GRC in an organisation?
  4. Is Enablon GRC suitable for businesses in regulated industries such as finance and healthcare?
  5. Can Enablon GRC be customised to meet specific GRC requirements of different organisations?

What is Enablon GRC and what does it stand for?

Enablon GRC is a sophisticated software platform designed to streamline governance, risk management, and compliance processes within organisations. The acronym “GRC” stands for Governance, Risk, and Compliance, representing the core functions that Enablon GRC integrates and enhances. By centralising data, automating workflows, and providing robust reporting capabilities, Enablon GRC empowers businesses to effectively manage regulatory compliance, mitigate risks, and maintain operational efficiency. This comprehensive solution offers a holistic approach to GRC management, enabling organisations to achieve greater visibility and control over their governance practices, risk exposure, and compliance adherence.

How can Enablon GRC help streamline governance, risk, and compliance processes?

Enablon GRC offers a comprehensive solution to streamline governance, risk, and compliance processes by centralising and integrating key functions into a single platform. Through its centralised data management capabilities, Enablon GRC eliminates silos and provides a unified view of risks and compliance status across the organisation. The platform facilitates proactive risk identification and assessment, enabling businesses to implement effective mitigation strategies. With automation features for compliance workflows and monitoring, Enablon GRC simplifies compliance management tasks, ensuring adherence to regulations. Its robust reporting tools enable stakeholders to generate customised reports on key performance indicators and trends, empowering informed decision-making. Overall, Enablon GRC enhances transparency, efficiency, and control over GRC activities, helping organisations navigate complex regulatory landscapes with ease.

What are the key benefits of implementing Enablon GRC in an organisation?

Implementing Enablon GRC in an organisation offers a multitude of key benefits that can significantly enhance governance, risk management, and compliance processes. Some of the primary advantages include centralised data management, enabling a unified view of risks and compliance status; proactive risk mitigation through effective identification and assessment; streamlined compliance management with automation capabilities; robust reporting and analytics for informed decision-making based on KPIs and trends; as well as enhanced transparency and accountability through comprehensive audit trail maintenance. Overall, the implementation of Enablon GRC empowers organisations to optimise their GRC initiatives, improve operational efficiency, and ensure adherence to regulatory requirements with greater ease and effectiveness.

Is Enablon GRC suitable for businesses in regulated industries such as finance and healthcare?

Businesses operating in regulated industries, such as finance and healthcare, often wonder if Enablon GRC is a suitable solution for their specific needs. The answer is a resounding yes. Enablon GRC offers tailored functionalities that cater to the stringent regulatory requirements of these sectors. From managing financial regulations like Basel III in the finance industry to ensuring compliance with data privacy laws such as HIPAA in healthcare, Enablon GRC provides the necessary tools and capabilities to streamline governance, risk management, and compliance processes effectively. Its centralised data management, automated workflows, and robust reporting features make it an ideal choice for businesses seeking to navigate the complex regulatory landscape with confidence and efficiency.

Can Enablon GRC be customised to meet specific GRC requirements of different organisations?

One of the frequently asked questions about Enablon GRC is whether it can be customised to meet the specific GRC requirements of different organisations. The answer is a resounding yes. Enablon GRC is designed with flexibility and scalability in mind, allowing organisations to tailor the platform to align with their unique governance, risk, and compliance needs. Through customisation options such as configurable workflows, data fields, reporting templates, and user permissions, Enablon GRC empowers businesses to adapt the system to reflect their specific GRC frameworks and regulatory obligations. This flexibility ensures that organisations can effectively address their individual compliance challenges and achieve optimal alignment with their strategic objectives.

Identity Access Management in SAP

The Importance of Identity Access Management in SAP

In today’s digital landscape, data security is paramount for organisations across all industries. As businesses rely on enterprise resource planning (ERP) systems like SAP to manage their operations efficiently, the need for robust identity access management (IAM) within these platforms has become increasingly crucial.

What is Identity Access Management?

Identity Access Management refers to the processes and technologies used to manage and control user access to critical information within an organisation. In the context of SAP, IAM involves defining and managing user roles, permissions, and privileges within the system to ensure that only authorised individuals have access to specific data and functionalities.

The Role of IAM in SAP Security

Effective IAM in SAP helps prevent unauthorised access to sensitive data, mitigates the risk of data breaches, and ensures compliance with regulatory requirements such as GDPR and SOX. By implementing IAM controls, organisations can enforce segregation of duties, least privilege principles, and multi-factor authentication to enhance security within their SAP environment.

Benefits of Implementing IAM in SAP

  • Enhanced Security: IAM reduces the risk of insider threats and external cyberattacks by controlling user access based on predefined policies.
  • Compliance: Organisations can demonstrate compliance with industry regulations by implementing IAM controls that govern user permissions and activities.
  • Operational Efficiency: By streamlining user provisioning and deprovisioning processes, IAM helps improve operational efficiency and reduce administrative overhead.
  • Auditing and Monitoring: IAM enables organisations to track user activities, generate audit trails, and monitor system access for suspicious behaviour.
  • Risk Mitigation: Proactive identification of potential risks through IAM allows organisations to address vulnerabilities before they are exploited.

In Conclusion

In conclusion, Identity Access Management plays a vital role in safeguarding sensitive information within SAP environments. Organisations that prioritise IAM implementation benefit from improved security posture, regulatory compliance, operational efficiency, and risk mitigation. By investing in robust IAM solutions tailored to their SAP systems, businesses can proactively protect their data assets and maintain trust with stakeholders.


9 Essential Tips for Effective Identity Access Management in SAP

  1. Implement role-based access control to restrict user permissions.
  2. Regularly review and update user access rights to ensure security.
  3. Enforce strong password policies for user accounts.
  4. Enable multi-factor authentication for an added layer of security.
  5. Monitor and log user activities to detect any suspicious behaviour.
  6. Provide training to users on best practices for identity access management.
  7. Integrate identity access management with other security solutions for comprehensive protection.
  8. Establish clear procedures for granting and revoking access privileges.
  9. Regularly audit user access to maintain compliance and security.

Implement role-based access control to restrict user permissions.

To enhance security and streamline user access within SAP systems, it is recommended to implement role-based access control. By assigning specific roles to users based on their job functions and responsibilities, organisations can restrict permissions to only the necessary data and functionalities required to perform their tasks. This approach helps enforce the principle of least privilege, reducing the risk of unauthorised access to sensitive information and mitigating potential security threats. Role-based access control in SAP not only enhances data protection but also simplifies user management processes by ensuring that users have appropriate access levels aligned with their roles within the organisation.

Regularly review and update user access rights to ensure security.

Regularly reviewing and updating user access rights in SAP is a fundamental practice in maintaining robust security measures within the system. By conducting periodic audits of user permissions and roles, organisations can identify and address any discrepancies or potential security risks promptly. Ensuring that users have only the necessary access rights based on their roles not only enhances data security but also helps in complying with regulatory requirements. Proactive management of user access rights in SAP contributes to a more secure environment, minimises the risk of unauthorised activities, and strengthens overall cybersecurity posture.

Enforce strong password policies for user accounts.

Enforcing strong password policies for user accounts is a fundamental aspect of effective Identity Access Management in SAP. By requiring users to create complex passwords that include a combination of letters, numbers, and special characters, organisations can significantly enhance the security of their SAP environment. Strong passwords help prevent unauthorised access to sensitive data and reduce the risk of password-related security breaches. Additionally, regular password changes and restrictions on password reuse further strengthen the overall security posture of the system, ensuring that only authorised users with secure credentials can access critical information within SAP.

Enable multi-factor authentication for an added layer of security.

Enabling multi-factor authentication in SAP is a highly recommended practice to enhance security measures within the system. By requiring users to provide multiple forms of verification before accessing sensitive data or functionalities, such as a password combined with a unique code sent to their mobile device, organisations can significantly reduce the risk of unauthorised access and potential data breaches. This additional layer of security adds an extra barrier for malicious actors trying to compromise user accounts, reinforcing the overall integrity of the identity access management framework in SAP.

Monitor and log user activities to detect any suspicious behaviour.

Monitoring and logging user activities within SAP is a crucial tip in Identity Access Management. By tracking and recording user interactions, organisations can proactively identify any suspicious behaviour or unauthorised access attempts. This practice not only helps in detecting potential security threats but also enables swift response and mitigation of risks. By maintaining detailed logs of user activities, businesses can enhance their overall security posture, strengthen compliance efforts, and ensure the integrity of their SAP environment.

Provide training to users on best practices for identity access management.

To enhance the effectiveness of identity access management in SAP, it is essential to provide comprehensive training to users on best practices. Educating users about the importance of maintaining secure access credentials, following proper authentication protocols, and understanding their roles and responsibilities within the system can significantly reduce the risk of security breaches. By promoting a culture of awareness and accountability through training sessions, organisations can empower their employees to actively contribute to maintaining a secure IAM environment in SAP.

Integrate identity access management with other security solutions for comprehensive protection.

To enhance the security of your SAP environment, it is advisable to integrate identity access management with other security solutions. By combining IAM with technologies such as threat detection, encryption, and endpoint protection, organisations can establish a layered defence strategy that offers comprehensive protection against a wide range of cyber threats. This integrated approach not only strengthens access controls within SAP but also helps in detecting and responding to security incidents more effectively. By leveraging the synergy between IAM and other security solutions, businesses can fortify their defences and safeguard their critical data assets from evolving cybersecurity risks.

Establish clear procedures for granting and revoking access privileges.

Establishing clear procedures for granting and revoking access privileges is a fundamental aspect of effective Identity Access Management in SAP. By defining transparent processes for assigning user permissions and removing access rights when necessary, organisations can ensure that only authorised individuals have the appropriate level of system access. This practice not only enhances security by preventing unauthorised usage but also streamlines administrative tasks, improves compliance with regulations, and minimises the risk of insider threats. Clear procedures for managing access privileges in SAP contribute to a more secure and efficient IT environment overall.

Regularly audit user access to maintain compliance and security.

Regularly auditing user access within SAP is a fundamental practice to uphold compliance standards and enhance security measures. By conducting routine audits, organisations can ensure that user permissions align with business requirements and regulatory mandates. Identifying and addressing any discrepancies or unauthorised access promptly not only mitigates the risk of data breaches but also fosters a culture of accountability and transparency. Through consistent monitoring and auditing of user access, businesses can proactively safeguard their SAP environment, maintain compliance with industry regulations, and bolster overall cybersecurity resilience.

Article: Mobile Identity and Access Management

The Importance of Mobile Identity and Access Management

Mobile devices have become an integral part of our daily lives, enabling us to stay connected and productive on the go. However, with this convenience comes the challenge of securing access to sensitive data and applications. This is where Mobile Identity and Access Management (IAM) plays a crucial role.

What is Mobile IAM?

Mobile IAM refers to the processes and technologies used to manage and secure access to resources on mobile devices. It encompasses authentication, authorisation, and other security measures to ensure that only authorised users can access data and applications from their mobile devices.

The Benefits of Mobile IAM

Implementing a robust Mobile IAM solution offers several benefits:

  • Enhanced Security: By implementing multi-factor authentication, device profiling, and encryption, Mobile IAM enhances the security of mobile access to corporate resources.
  • User Experience: A seamless user experience is essential for user adoption. Mobile IAM solutions provide convenient yet secure access to applications and data from any location.
  • Compliance: With regulations such as GDPR and HIPAA governing data privacy and security, mobile IAM helps organisations achieve compliance by enforcing access controls and audit trails.
  • Remote Management: IT administrators can remotely manage user access rights, permissions, and policies on mobile devices, ensuring consistent security across the organisation.

Challenges in Mobile IAM

While Mobile IAM offers numerous benefits, organisations may face challenges in its implementation:

  • User Acceptance: Balancing security with usability is crucial. Complex authentication processes may hinder user acceptance of Mobile IAM solutions.
  • Device Diversity: Managing access across a diverse range of mobile devices with varying operating systems can be challenging for IT teams.
  • Data Protection: Securing data stored on or accessed by mobile devices requires robust encryption mechanisms to prevent data breaches.

The Future of Mobile IAM

As the use of mobile devices continues to grow in the workplace, the importance of effective Mobile IAM will only increase. Future trends in Mobile IAM include biometric authentication, context-aware access controls based on user behaviour, and integration with cloud-based identity services for enhanced security.


Understanding Mobile Identity and Access Management: Key FAQs and Best Practices

  1. What is mobile identity and access management (IAM)?
  2. Why is mobile IAM important for businesses?
  3. How does mobile IAM enhance security on mobile devices?
  4. What are the common challenges in implementing mobile IAM?
  5. What are the best practices for securing mobile identity and access management?

What is mobile identity and access management (IAM)?

Mobile identity and access management (IAM) refers to the set of processes and technologies that govern how users are authenticated and authorised to access resources on mobile devices. It involves establishing secure protocols for verifying the identities of users, managing their permissions to access specific data or applications, and enforcing security policies to protect sensitive information. Mobile IAM plays a vital role in ensuring that only authorised individuals can securely access corporate resources from their mobile devices while maintaining a balance between user convenience and robust security measures.

Why is mobile IAM important for businesses?

Mobile Identity and Access Management (IAM) is crucial for businesses due to the proliferation of mobile devices in the workplace. With employees accessing corporate data and applications from various locations and devices, ensuring secure and controlled access is paramount. Mobile IAM provides a robust framework for authentication, authorisation, and data protection, safeguarding sensitive information against unauthorised access or breaches. By implementing mobile IAM solutions, businesses can enhance security, streamline user access management, achieve regulatory compliance, and mitigate the risks associated with mobile device usage in the corporate environment. Ultimately, mobile IAM empowers businesses to embrace the productivity benefits of mobile technology while maintaining a strong security posture.

How does mobile IAM enhance security on mobile devices?

Mobile Identity and Access Management (IAM) enhances security on mobile devices through a range of advanced measures. By implementing multi-factor authentication, mobile IAM ensures that only authorised users can access sensitive data and applications, adding an extra layer of security beyond traditional password protection. Additionally, device profiling capabilities enable organisations to identify and verify devices accessing their networks, reducing the risk of unauthorised access. Encryption mechanisms employed by mobile IAM solutions safeguard data in transit and at rest, protecting it from potential breaches. Overall, mobile IAM plays a critical role in bolstering security on mobile devices by combining authentication, authorisation, and encryption to create a robust defence against cyber threats.

What are the common challenges in implementing mobile IAM?

Implementing mobile Identity and Access Management (IAM) poses several common challenges for organisations. One major challenge is ensuring a balance between security and user experience. Complex authentication processes can lead to user frustration and resistance to adopting secure practices. Additionally, managing access across a diverse range of mobile devices with different operating systems can be complex for IT teams. Data protection is another critical challenge, as securing data stored on or accessed by mobile devices requires robust encryption mechanisms to prevent potential data breaches. Overcoming these challenges requires a strategic approach that prioritises both security and usability in mobile IAM implementation.

What are the best practices for securing mobile identity and access management?

When it comes to securing mobile identity and access management, following best practices is essential to safeguard sensitive data and applications on mobile devices. Some key recommendations include implementing multi-factor authentication to add an extra layer of security, enforcing strong password policies, regularly updating mobile device operating systems and applications to patch vulnerabilities, encrypting data both at rest and in transit, leveraging biometric authentication where possible for added security, conducting regular security audits and assessments, and providing comprehensive user training on mobile security practices. By adhering to these best practices, organisations can enhance the overall security posture of their mobile identity and access management systems.