Identity Management in Cloud Security
As organisations move applications, data and infrastructure to the cloud, controlling who can access what becomes a central security challenge. Identity management provides the processes and technologies needed to identify users and services, verify their identity and grant access to the resources they need. Done well, it helps reduce the risk of data breaches while supporting efficient, flexible working.
What is identity management?
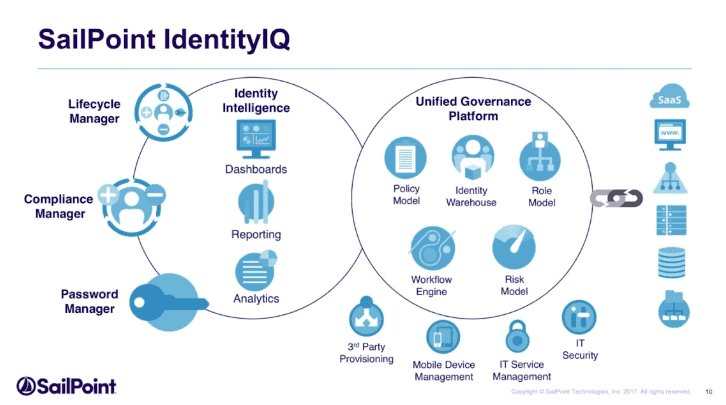
Identity management is the administration of digital identities and their permissions throughout their lifecycle. An identity might belong to an employee, contractor, customer, application or automated workload. Identity and access management (IAM) brings identity management together with the rules and tools used to control access.
In a cloud environment, IAM commonly includes:
- Authentication: confirming that a user or service is who or what it claims to be.
- Authorisation: deciding which resources an authenticated identity can use and what actions it can perform.
- Provisioning and deprovisioning: creating, changing and removing accounts and access as requirements change.
- Governance: reviewing permissions, enforcing policies and maintaining evidence of access decisions.
Why identity matters in cloud security
Cloud services can be accessed from different locations and devices, and organisations may use several cloud platforms alongside on-premises systems. Traditional network boundaries are therefore less reliable as the main way to determine trust. Identity offers a more direct way to manage access: each request can be evaluated according to the identity, the resource, the context and the applicable policy.
Weak identity controls can leave accounts over-privileged, unused or protected by inadequate authentication. If an attacker obtains a valid account, they may be able to operate within cloud systems using legitimate access. Strong identity management helps limit the opportunities available to compromised accounts and makes suspicious activity easier to investigate.
Core principles for managing cloud identities
Apply least privilege
Give each identity only the permissions required for its role, and only for as long as those permissions are needed. Avoid broad, permanent access where a narrower role or time-limited approval will do. Regular reviews can identify permissions that have accumulated or are no longer necessary.
Use multi-factor authentication
Multi-factor authentication (MFA) requires more than one form of proof, such as a password and an authentication app. It can reduce the risk of account takeover if a password is stolen or reused. MFA should be prioritised for administrators, remote access and other sensitive accounts, with secure recovery processes in place.
Centralise identity where practical
Connecting cloud services to a central identity provider can make access easier to manage and improve consistency. Federation and single sign-on allow users to access approved services with centrally managed identities, reducing the need for separate passwords in each application. Centralisation should be supported by strong protections for the identity provider itself, as it can become a high-value target.
Manage privileged access carefully
Administrative accounts can make significant changes to cloud environments. Keep privileged access separate from everyday user accounts where possible, restrict who can use it and monitor its use. Just-in-time access, in which elevated permissions are granted temporarily when required, can reduce exposure compared with standing administrator access.
Secure non-human identities
Applications, virtual machines, containers and automation tools also need identities to access cloud resources. These identities should have their own narrowly scoped permissions rather than sharing a user account or a long-lived credential. Where available, use managed identities or short-lived credentials, and rotate or revoke secrets according to a defined process.
Managing the identity lifecycle
Identity security depends on reliable processes from the moment access is requested until it is removed. Joiner, mover and leaver processes should ensure that access matches a person’s current responsibilities. When someone changes role, permissions should be updated promptly; when they leave, access should be disabled across relevant systems without delay.
Access requests should have a clear owner and approval path. Managers or resource owners should be able to see what access is being requested and why. Periodic access reviews can then confirm that existing permissions remain appropriate, including access held by external partners and service accounts.
Monitoring and detection
Identity logs can show sign-ins, permission changes, authentication failures and administrative actions. Combining these records with cloud activity logs helps security teams identify unusual patterns, such as a sign-in from an unexpected location or an account suddenly accessing sensitive resources.
Logging is most useful when it is protected from unauthorised alteration, retained for an appropriate period and reviewed through alerts or investigations. Organisations should also define how to respond to suspected identity compromise, including how to disable accounts, revoke sessions and rotate credentials.
Common challenges
- Permission sprawl: access grows over time and is not removed when it is no longer needed.
- Unmanaged credentials: secrets are embedded in scripts or stored in locations that are difficult to monitor.
- Inconsistent policies: different cloud services apply different authentication and access rules.
- Incomplete visibility: organisations lack a clear inventory of users, service accounts and permissions.
- Over-reliance on passwords: password policies alone do not provide sufficient protection against phishing or credential theft.
Building a stronger identity strategy
A practical programme starts with an inventory of identities, cloud services and existing permissions. From there, organisations can prioritise sensitive accounts and data, establish consistent authentication requirements, reduce excessive access and improve the management of non-human identities. Automation can help apply policies consistently, but it should be tested and monitored to avoid granting or removing access incorrectly.
Identity management is not a one-off configuration task. Cloud services, teams and threats change, so access policies and processes need regular review. By treating identity as a core part of cloud security, organisations can make access more controlled, auditable and responsive to changing business needs.
7 Essential Tips for Secure Identity Management in the Cloud
- Enforce multi-factor authentication for all users.
- Apply least-privilege access by default.
- Use single sign-on with strong authentication.
- Review permissions regularly and remove unused access.
- Disable accounts promptly when people leave.
- Use separate accounts for admin tasks.
- Monitor sign-ins for unusual activity.
Enforce multi-factor authentication for all users.
Enforce multi-factor authentication (MFA) for every user accessing cloud services, not just administrators. Requiring a second form of verification alongside a password makes it harder for attackers to take over an account with stolen or reused credentials. Choose secure methods, such as an authenticator app or a passkey, and provide clear guidance on enrolment and account recovery. Review MFA coverage regularly to ensure that new users and services are included.
Apply least-privilege access by default.
Apply least-privilege access by default: give each user, application and service only the permissions it needs to do its job, and avoid broad or permanent access. Review permissions regularly, remove those that are no longer required, and use temporary elevated access for sensitive tasks where possible. This limits the potential damage if an account is compromised and helps keep your cloud environment easier to manage and audit.
Use single sign-on with strong authentication.
Use single sign-on (SSO) to let users access approved cloud services through one centrally managed identity, making access easier to administer and reducing the need for multiple passwords. Protect that identity with strong authentication, such as multi-factor authentication, particularly for administrators and access to sensitive data. Because SSO concentrates access in one account, monitor sign-in activity closely and ensure there is a secure process for responding to suspected compromise.
Review permissions regularly and remove unused access.
Review cloud permissions regularly to ensure that users, applications and service accounts still have the access they need—and nothing more. Remove unused accounts and permissions promptly, particularly when someone changes role or leaves the organisation. Routine reviews help reduce the risk of compromised or forgotten accounts being used to reach sensitive data and systems.
Disable accounts promptly when people leave.
Disable user accounts as soon as someone leaves the organisation, rather than waiting for a routine access review. Prompt deprovisioning helps prevent former employees or contractors from using their credentials to access cloud services, data or systems. Include cloud platforms, connected applications, remote access and any privileged accounts in the offboarding process, and revoke active sessions and authentication tokens where possible. A clear, documented process helps ensure access is removed consistently and on time.
Use separate accounts for admin tasks.
Use separate accounts for administrative tasks and everyday work. A dedicated admin account limits exposure if a standard account is compromised and makes privileged activity easier to monitor. Keep the admin account’s permissions to the minimum required, protect it with multi-factor authentication, and use it only when elevated access is needed.
Monitor sign-ins for unusual activity.
Monitor sign-ins for unusual activity, such as logins from unfamiliar locations, unexpected devices or unusual times, repeated failed attempts, or sudden changes in access patterns. Set up alerts for potentially risky events and investigate them promptly. Where appropriate, require additional verification or temporarily block access while a suspicious sign-in is assessed. Regular monitoring can help identify compromised accounts early and limit the damage they may cause.