AD Privileged Identity Management: A Practical Guide
Active Directory (AD) is central to identity and access management in many organisations. It controls how users, computers and services authenticate and access network resources. When highly privileged accounts are compromised or misused, an attacker may be able to change security settings, access sensitive information or take control of large parts of the environment.
AD privileged identity management is the set of processes and technologies used to control, monitor and protect accounts with elevated permissions. The aim is to ensure that privileged access is granted only when needed, for the right amount of time, and with appropriate oversight.
What counts as a privileged identity?
A privileged identity is an account or identity with permissions beyond those of a standard user. In an Active Directory environment, this may include:
- Domain Administrator and Enterprise Administrator accounts
- Accounts belonging to groups that can manage users, computers, Group Policy or domain controllers
- Service accounts used by applications, scripts or scheduled tasks
- Delegated administrator accounts with control over particular organisational units or systems
- Emergency or “break-glass” accounts intended for exceptional situations
Privilege is not limited to membership of well-known administrator groups. An account may have significant control through delegated permissions, nested group membership or access to systems that hold credentials. Regularly reviewing effective permissions is therefore essential.
Why privileged identity management matters
Privileged accounts are attractive targets because they can provide broad access and allow security controls to be changed. A single compromised administrator account can sometimes enable an attacker to create new accounts, alter permissions, deploy malicious software or move between systems.
Good privileged identity management helps organisations to:
- Reduce the number of accounts with standing administrative access
- Limit the impact of stolen credentials
- Identify excessive, unused or unexpected permissions
- Improve accountability by linking privileged actions to named individuals
- Support security reviews, incident investigations and compliance requirements
Core principles for managing AD privileges
Apply least privilege
Give users and services only the permissions required to perform their duties. Avoid using broad domain-level privileges where a narrower delegated role will do. Review permissions regularly, especially when people change roles or leave the organisation.
Separate standard and administrative accounts
Administrators should use a standard account for everyday tasks such as email and web browsing, and a separate, controlled account for administrative work. This reduces the chance that routine activity exposes privileged credentials to phishing or malware.
Use time-limited access where possible
Standing privileges remain available even when they are not being used. Where the environment and tooling allow it, grant elevated access only for an approved task and remove it afterwards. Just-in-time access can reduce the period in which an account is exposed to misuse.
Protect authentication
Use multi-factor authentication for privileged access wherever supported, particularly for remote administration and access to management systems. Strong authentication should be combined with secure credential storage, managed administrative workstations and restrictions on where privileged accounts can sign in.
Keep service accounts under control
Service accounts can be overlooked because they operate in the background. Document their owners and purpose, grant only the permissions they need, and avoid interactive logon where it is not required. Use managed service account options where suitable, and review accounts that are unused or no longer linked to an active service.
Active Directory PIM and Microsoft Entra PIM
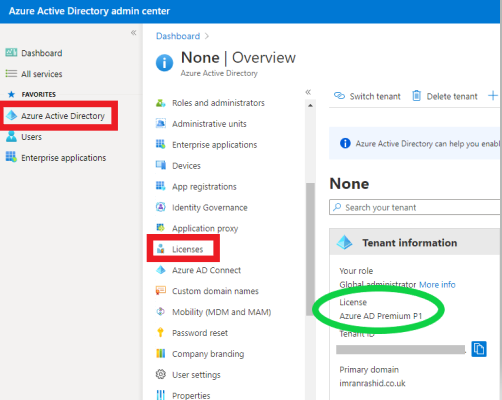
The term “PIM” is often associated with Microsoft Entra Privileged Identity Management, a service that helps manage eligible and active role assignments in Microsoft Entra ID and certain Microsoft services. This is distinct from managing privileged access in a traditional on-premises Active Directory domain.
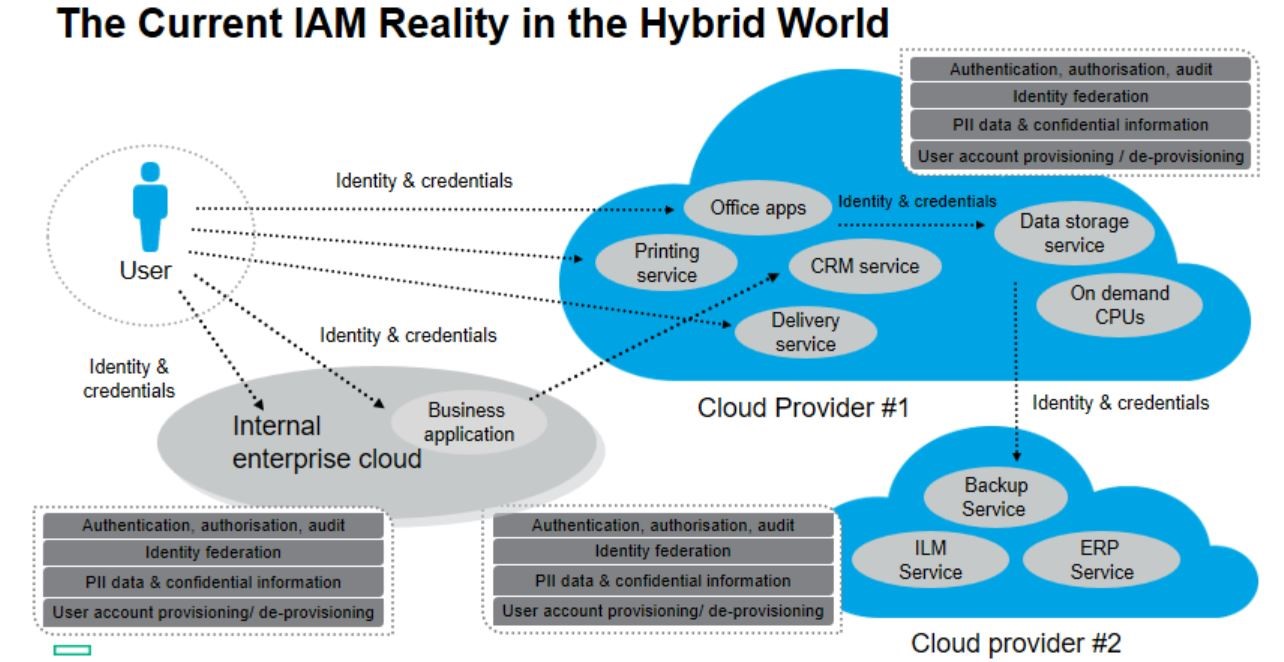
Organisations may use Entra PIM for cloud roles while using separate controls and processes for on-premises AD privileges. A hybrid environment needs a joined-up approach: cloud and on-premises identities, groups, administrative workstations and trust relationships should all be considered. Entra PIM should not be assumed to automatically manage every privilege in an on-premises AD environment.
Monitoring and auditing privileged activity
Privilege management is not a one-off exercise. Organisations should monitor changes to privileged groups, account permissions, Group Policy and domain controller settings. Alerts can help security teams investigate unexpected changes promptly.
Useful audit questions include:
- Who is a member of each privileged group, including through nested groups?
- Which accounts have not been used recently?
- Are administrator accounts signing in from appropriate systems?
- Have new accounts, delegations or service permissions been created?
- Are privileged actions attributable to an individual rather than a shared account?
Audit data should be retained and protected in line with the organisation’s security and operational requirements. Monitoring is most effective when alert rules are tuned to identify meaningful activity without overwhelming the team with false positives.
How to improve privileged identity management
- Discover privileged access. Identify administrator accounts, privileged groups, delegated permissions, service accounts and systems that can influence AD security.
- Validate business need. Confirm an owner and purpose for each privileged identity, then remove unnecessary access.
- Reduce standing privilege. Use narrower roles and time-limited access where practical.
- Strengthen administrative access. Separate accounts, require strong authentication and restrict privileged sign-ins to trusted devices and locations.
- Secure credentials and systems. Protect domain controllers, administrative workstations, backup systems and credential stores as high-value assets.
- Monitor and review. Audit sensitive changes, investigate anomalies and schedule regular access reviews.
- Test emergency procedures. Maintain carefully controlled emergency access and confirm that it works without leaving it exposed to routine use.
Common mistakes to avoid
- Using one administrator account for email, browsing and infrastructure management
- Leaving former employees or old service accounts in privileged groups
- Relying on group membership checks without reviewing delegated permissions
- Sharing administrator credentials between several people
- Assuming that cloud privileged access controls cover on-premises AD automatically
- Enabling auditing without reviewing alerts or protecting the resulting logs
Conclusion
AD privileged identity management is a vital part of protecting an organisation’s identity infrastructure. By discovering privileged access, applying least privilege, limiting standing permissions, securing authentication and monitoring sensitive changes, organisations can reduce the risk associated with powerful accounts.
The most effective approach combines technology with clear ownership, regular access reviews and well-practised operational procedures. As environments evolve across on-premises Active Directory and cloud identity platforms, privileged access controls should be reviewed as a connected part of the wider security strategy.
8 Benefits of Privileged Identity Management in Active Directory
- Reduces the risk of privileged account misuse.
- Limits access to only what each role requires.
- Helps protect sensitive data and systems.
- Supports stronger authentication controls.
- Makes privileged actions easier to monitor.
- Helps identify excessive or unused permissions.
- Improves accountability for administrative changes.
- Supports security reviews and compliance efforts.
Drawbacks of Active Directory Privileged Identity Management
- Can be complex to implement and maintain.
- May require additional tools and staff training.
- Poorly configured controls can disrupt admin tasks.
- Regular reviews take time and resources.
Reduces the risk of privileged account misuse.
AD privileged identity management reduces the risk of privileged account misuse by ensuring that administrative access is limited to authorised people and granted only when required. Applying least-privilege permissions, using separate admin accounts and reviewing access regularly can help prevent accidental changes and make it harder for compromised credentials to be abused. Monitoring privileged activity also helps organisations spot unusual behaviour and respond more quickly.
Limits access to only what each role requires.
AD privileged identity management helps ensure that users receive only the access needed to carry out their specific responsibilities. By assigning permissions according to defined roles and removing unnecessary privileges, organisations can reduce the risk of accidental changes, misuse and compromised accounts being used to access sensitive systems. This least-privilege approach also makes access easier to review and manage as roles change.
Helps protect sensitive data and systems.
AD privileged identity management helps protect sensitive data and systems by restricting powerful access to authorised people and services that genuinely need it. Applying least-privilege permissions, requiring stronger authentication and monitoring privileged activity can reduce the risk of accidental changes, misuse and stolen credentials being used to access critical resources.
Supports stronger authentication controls.
AD privileged identity management supports stronger authentication controls by applying additional safeguards to accounts with elevated access. Organisations can require multi-factor authentication, restrict sign-ins to trusted devices or locations, and use separate accounts for administrative tasks. These measures make it harder for attackers to misuse stolen credentials and help protect critical Active Directory resources.
Makes privileged actions easier to monitor.
AD privileged identity management makes privileged actions easier to monitor by providing clearer oversight of who accessed elevated permissions, when they used them and what changes they made. This visibility helps security teams spot unusual activity, investigate incidents more quickly and maintain an audit trail for reviews and compliance. By linking privileged actions to specific accounts and setting alerts for sensitive changes, organisations can improve accountability and respond more confidently to potential threats.
Helps identify excessive or unused permissions.
AD privileged identity management helps organisations identify permissions that are broader than a user’s role requires or are no longer being used. Regularly reviewing privileged accounts, group memberships and delegated access makes it easier to remove unnecessary rights, reduce the risk of misuse and ensure people retain only the access needed to do their jobs.
Improves accountability for administrative changes.
AD privileged identity management improves accountability by making it clearer who performed an administrative change, when it happened and, where auditing is configured, what was changed. Using named accounts, controlled access and activity logs helps organisations trace actions back to the responsible administrator, investigate unexpected changes and support compliance reviews. This visibility can also encourage more careful handling of privileged access.
Supports security reviews and compliance efforts.
AD privileged identity management supports security reviews and compliance efforts by giving organisations clearer visibility of who has elevated access, what permissions they hold and how those privileges are used. Regular access reviews can help identify excessive or outdated permissions, while audit logs provide evidence of administrative activity for investigations and compliance checks. This makes it easier to demonstrate that access is appropriately controlled and to address potential risks before they become serious issues.
Can be complex to implement and maintain.
One potential drawback of AD privileged identity management is that it can be complex to implement and maintain. Identifying every privileged account, mapping permissions and designing appropriate approval workflows takes time and specialist expertise. In larger or hybrid environments, integrating tools with existing systems and processes can add further challenges. Ongoing reviews, policy updates and monitoring also require dedicated resources, so organisations need to plan for continuous management rather than treating implementation as a one-off task.
May require additional tools and staff training.
One potential drawback of AD privileged identity management is that it may require additional tools and staff training. Organisations might need to invest in software for managing elevated access, monitoring activity and producing audit reports, as well as time to configure and maintain it. Staff must also understand new processes, such as requesting temporary privileges and using separate administrator accounts. These costs and learning requirements can make implementation more challenging, particularly for smaller IT teams.
Poorly configured controls can disrupt admin tasks.
Poorly configured privileged identity management controls can disrupt routine administrative work by blocking legitimate access, adding approval delays or allowing permissions to expire before a task is complete. If access policies are too restrictive or workflows are not designed around operational needs, administrators may struggle to respond quickly to incidents or complete essential maintenance. Controls should therefore be carefully tested, clearly documented and regularly reviewed to balance security with the need for reliable day-to-day administration.
Regular reviews take time and resources.
Regular reviews of privileged access can take considerable time and resources, particularly in large or complex Active Directory environments. Teams need to verify account owners, assess permissions, check whether access is still necessary and follow up on any changes. If reviews are too frequent or handled manually, they can add to administrators’ workloads and divert attention from other security tasks. Automating discovery and reporting, while prioritising high-risk accounts, can make the process more manageable.